WD My Book Live Mass Wipe: The EOL IoT Disaster
Tens of thousands of abandoned Western Digital NAS drives got factory-reset by strangers through a decade-old unpatched flaw. The definitive end-of-life IoT case study.


Hands-on cybersecurity tutorials, CVE breakdowns, and guided learning paths. Every technique is explained, tested, and paired with its mitigation — so you learn the attack and the defense together.
Tens of thousands of abandoned Western Digital NAS drives got factory-reset by strangers through a decade-old unpatched flaw. The definitive end-of-life IoT case study.
Since January 2024, ships manage cyber risk under IMO-derived requirements enforced by flag and port-state control, IACS E26 and E27 give class societies assessment criteria, and the US Coast Guard can detain deficient vessels. Bridge, cargo, propulsion, SATCOM and crew IT share one hull: treat the vessel as an OT estate.
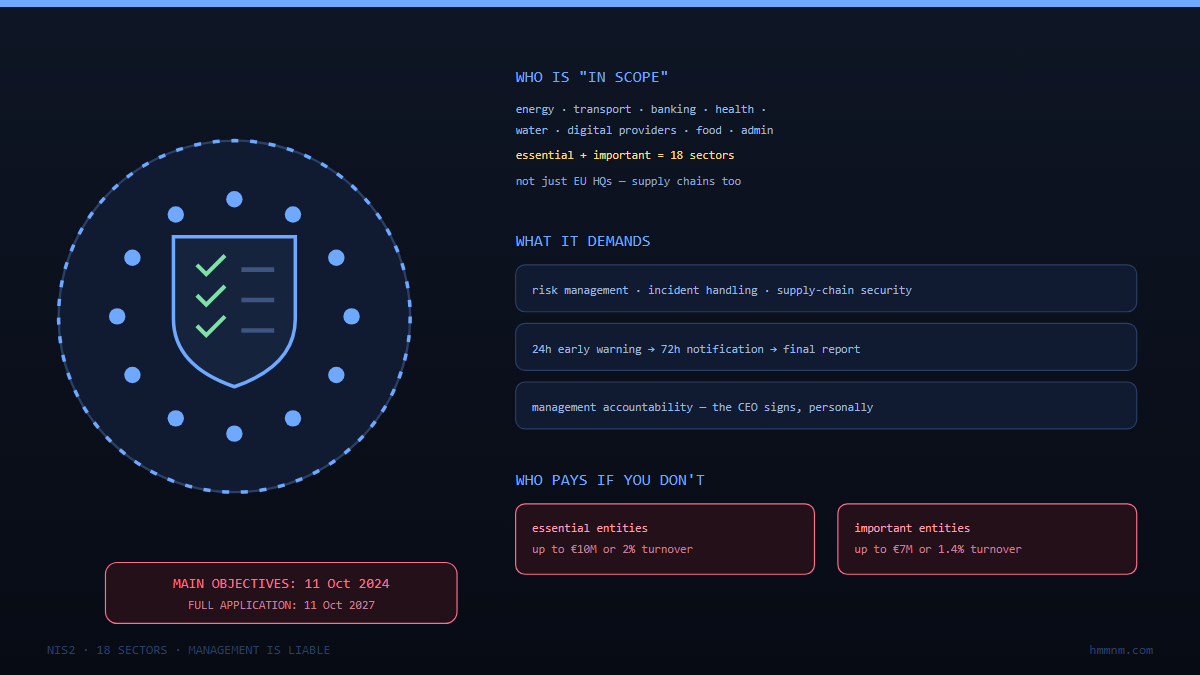
Food plants, logistics firms, waste management, research labs: 18 sectors are in scope, plus everyone their covered customers drag in via contracts. The duties read like an incident-readiness program — 24-hour early warning, 72-hour notification, personal accountability for executives — and the basics were overdue anyway.
DragonForce’s Backdoor.Turn routes ransomware C2 through Microsoft Teams TURN relays using anonymous visitor tokens — LOTI, living off trusted infrastructure. Why network detection dies and what still works.
Comprehensive guide to securing login and registration systems. Covers authentication vulnerabilities, brute-force protection, session management, CAPTCHA implementation, and security best practices.
SQL injection stayed in the OWASP Top 10 for 20+ years. Prompt injection is the same bug with worse permissions — here’s the history, real examples, and the defense playbook.
Class 1, 2, 3 EFB hardware explained — plus how AC 120-76E replaced classes with portable vs installed. Displays, AIDs, buses, power, mounting.
CVE-2023-2868 gave pre-auth RCE in Barracuda’s email gateways via spreadsheet parsing, exploited since October 2022. The final verdict: replace every appliance. Remediation doctrine lessons.
Ireland’s DPC fined Meta €1.2B over EU-US transfers that Schrems II had already doomed — the largest GDPR fine ever, ordering suspension and deletion. Transfer-governance lessons for security teams.
A server-side fault in ASUS’s firmware-update mechanism crashed routers worldwide, requiring manual recovery — a global outage delivered through the trusted update path, no attacker required.
WD’s 2023 intrusion took My Cloud services offline mid-extortion claims, locking users out of their own files. Cloud-tethered storage lessons.
3CX’s signed desktop app shipped a trojan after its build pipeline fell to an upstream vendor compromise — the first documented double supply-chain attack.