Travelex Ransomware 2020: When Sodinokibi Crippled a Currency Giant

On 31 December 2019, foreign exchange giant Travelex took its UK and international websites and mobile apps offline following a cyberattack, an outage that also knocked out white-label travel money services at ASDA, Tesco and Sainsbury’s overnight. When the story became public on 7 January 2020, the criminals behind Sodinokibi (REvil) ransomware were demanding 4.6 million pounds, claiming to have copied more than 5GB of customer data, and the company would spend weeks rebuilding systems by hand. This account reconstructs the verified timeline, the double-extortion playbook, and how the incident contributed to an August 2020 administration that cut more than a thousand UK jobs.
Continue ReadingTravelex Ransomware 2020: When Sodinokibi Crippled a Currency Giant

Ransomware at a Gas Compression Facility: CISA’s OT Alert

On 20 February 2020, CISA published AA20-030A, a joint advisory describing how ransomware had disrupted a natural gas compression facility: a phishing link let commodity ransomware spread from IT into the OT network, encrypting data historians and polling servers, severing HMI visibility, and leaving operators blind to real-time pressure and flow data for two days. The advisory became a reference model for oil and gas asset owners because it mapped, step by step, how a single email chained into loss of operational visibility without directly controlling pipeline equipment. This retrospective walks through the kill chain, the defensive gaps, and the guidance that followed.

Continue ReadingRansomware at a Gas Compression Facility: CISA’s OT Alert

Change Healthcare ALPHV: The Ransomware That Broke US Healthcare

One ALPHV/BlackCat intrusion in February 2024 froze claims and pharmacy payments across US healthcare for weeks — the single most consequential ransomware attack of the year. This account covers the nine-day dwell time, the $22 million ransom payment and the exit-scam double-cross that brought RansomHub back for seconds, the eventual disclosure of hundreds of millions of records, and why one processor’s central position converted a single encryptor into a national healthcare liquidity crisis.

Continue ReadingChange Healthcare ALPHV: The Ransomware That Broke US Healthcare
Read more about the article The First 24 Hours of a Ransomware Attack: Survival Playbook
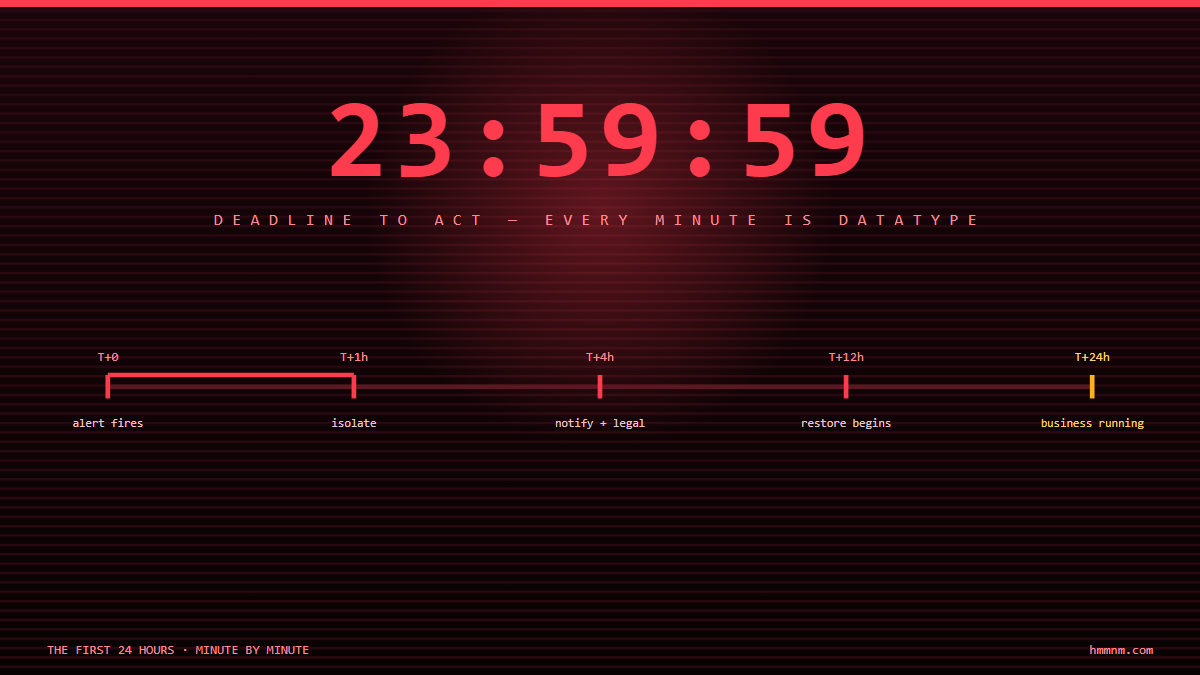
Ransomware countdown first 24 hours timeline

The First 24 Hours of a Ransomware Attack: Survival Playbook

Change Healthcare lost the claims pipeline of a nation in hours. This minute-by-minute playbook covers hour zero containment, the command structure by hour four, backup verification, pay/no-pay, regulatory clocks — and the non-technical decisions that decide survival.

Continue ReadingThe First 24 Hours of a Ransomware Attack: Survival Playbook