Hmmnm
All articles published by

Hmmnm

Hands-on cybersecurity tutorials, CVE breakdowns, and guided learning paths. Every technique is explained, tested, and paired with its mitigation — so you learn the attack and the defense together.

Learning Paths · About Hmmnm · Editorial policy

Read more about the article How to Pentest OT Networks Without Halting Production
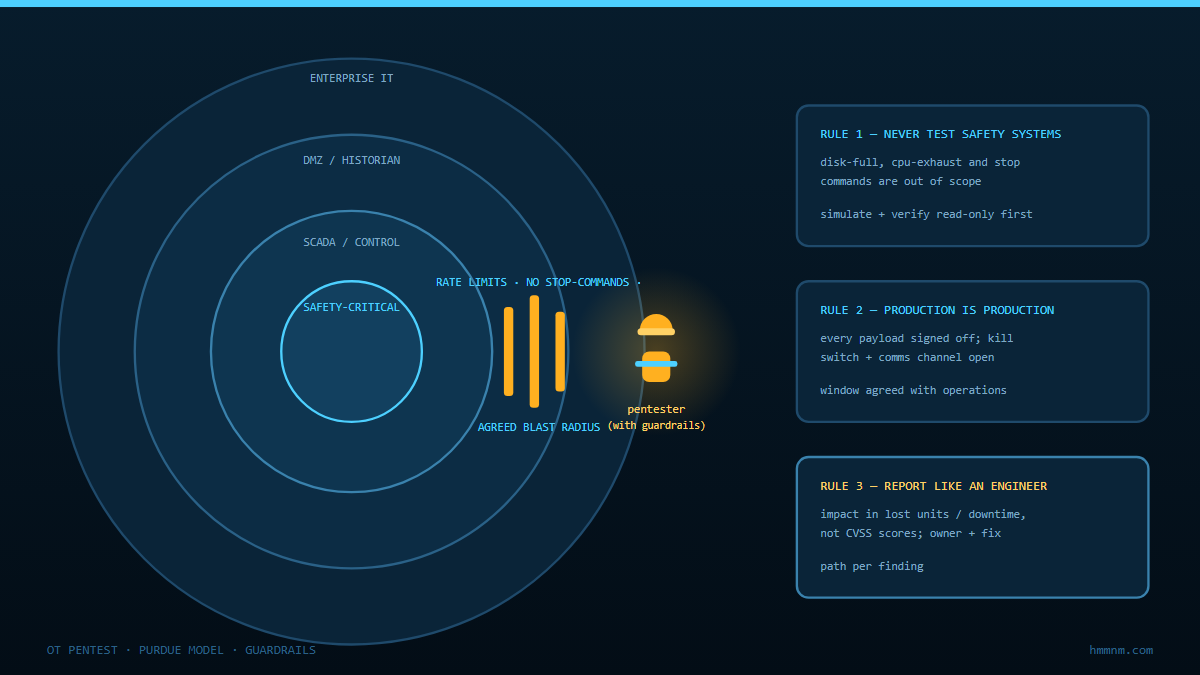
OT pentest Purdue model zones with guardrails

How to Pentest OT Networks Without Halting Production

Oldsmar proved an intruder can move a plant setpoint from a browser tab. This is the safe method: passive-first discovery, read-only active testing, writes proven on clone benches, and findings ranked in downtime currency — not CVSS.
Continue ReadingHow to Pentest OT Networks Without Halting Production
Read more about the article Identity Security: Modern Attacks on Users, Sessions & Trust
Identity Security: Modern Attacks on Users, Sessions & Trust

Identity Security: Modern Attacks on Users, Sessions & Trust

How identity became the new perimeter in modern cybersecurity. Explore MFA bypass techniques, OAuth consent phishing, device code attacks, token theft, and defense strategies for identity-centric security.

Continue ReadingIdentity Security: Modern Attacks on Users, Sessions & Trust

Internet Archive Breach and DDoS: 31M Accounts, One Pop-Up

On October 9, 2024, visitors to the Internet Archive’s Wayback Machine were greeted by an injected JavaScript pop-up announcing the compromise of 31,081,179 user accounts — the HIBP-confirmed count of the organization’s authentication database, loaned from a September exposure of its Zendesk support portal. A concurrent DDoS attributed to SN_BlackMeta compounded the disruption; days later, archived XSS attempts confirmed the org’sJavaScript security debt. This account traces the initial access, the pop-up’s evidence chain, and the funding-and-fragility story of a library built on hope.

Continue ReadingInternet Archive Breach and DDoS: 31M Accounts, One Pop-Up

Marriott’s FTC Settlement: 20 Years of Audits for Starwood’s Ghosts

On October 9, 2024, the FTC announced a pair of consent orders — Marriott and its Starwood subsidiary — resolving claims that skimped security contributed to the 2014-2018 Starwood intrusions and a 2018 breach affecting over 131 million consumers from which attackers extracted 5.25 million unencrypted passport numbers. The order imposes 20 years of independent assessments and a claims program offering $150 cash orotomy spending on security — close kin to the UK ICO’s £18.4M fine and the states’ $52M settlement. This account traces the 2014→2018 intrusion, the regulatory pile-on, and what a two-decade oversight tail teaches about inherited security debt.

Continue ReadingMarriott’s FTC Settlement: 20 Years of Audits for Starwood’s Ghosts

Kia’s Web Portal: Register Any Car’s Account, Control It From Your Phone

On September 25, 2024, researchers Karan Saini and Sam Curry published an access-control flaw in Kia’s dealer and consumer web infrastructure: given only a license plate, an attacker could register an account with remote lock, unlock, start, stop, locate and horn control over 2014-2025 connected vehicles they did not own. Kia patched in August before disclosure. This account walks the plate-to-command chain, the ownership-verification gap, the threat model for tracking and theft, and the automotive-API authorization lesson that outlasts the brand.

Continue ReadingKia’s Web Portal: Register Any Car’s Account, Control It From Your Phone

Cisco SSM On-Prem Flaws: CVSS 10.0 and a CLI Zero-Day in One Week

In early October 2024, Cisco’s disclosure cadence stacked two unrelated but equally urgent problems: CVE-2024-20419, a CVSS 10.0 unauthenticated password-change flaw in Smart Software Manager On-Prem that let anyone with network access reset the admin API account, and CVE-2024-20399, a CLI command-injection bug in NX-OS already being exploited in the wild per the CISA KEV catalog. This account reconstructs both flaws’ mechanics, the patch timelines, and what this pairing says about authentication surface area in management tooling.

Continue ReadingCisco SSM On-Prem Flaws: CVSS 10.0 and a CLI Zero-Day in One Week

Google AI Overviews: Prompt Injection Hits the Homepage of the Internet

When Google rolled AI Overviews into US search in May 2024, satirical sources got quoted as fact at national scale — glue on pizza, rocks as vitamins — and security researchers reframed the comedy as indirect prompt injection: retrieved content steering the answer in Google’s own voice. This piece tracks the launch-week failures, the overview-bait SEO economy that followed, the manual-removal treadmill, provenance-aware retrieval as the real fix, and why RAG systems inherit the trust profile of their worst-cited source.

Continue ReadingGoogle AI Overviews: Prompt Injection Hits the Homepage of the Internet

KnowBe4 vs a Fake North Korean IT Worker: The AI-Era Insider Case Study

In July 2024, security-awareness firm KnowBe4 hired a remote principal software engineer who turned out to be a North Korean IT worker using an AI-groomed persona, a US PPPoE front, and a stolen identity. Detected within 32 minutes of suspicious activity and fully rigged with granular session logging, the case became the definitive inside look at DPRK pension applicantFraud — from laptop farms to paycheck revenue streams funding weapons programs. This piece reconstructs the fraud chain, the detection story, and the hiring controls that failed.

Continue ReadingKnowBe4 vs a Fake North Korean IT Worker: The AI-Era Insider Case Study

Ray AI Framework’s ‘Won’t Fix’ CVEs: A Control-Plane Debate

When Protect AI disclosed five Ray vulnerabilities in March 2024 — including critical RCE via the unauthenticated control plane — Anyscale’s ‘won’t fix, trusted-networks design’ stance ignited the year’s sharpest debate over AI infrastructure responsibility. This piece unpacks the job-submission RCE, the exposed-cluster census, the bounty economics, what Anyscale later shipped anyway, and the hardening playbook that became standard for every exposed ML control plane.

Continue ReadingRay AI Framework’s ‘Won’t Fix’ CVEs: A Control-Plane Debate

Sisense Breach: CI Credentials, AWS Keys and a CISA Advisory

On April 24, 2024, CISA and the FBI advised every Sisense customer to rotate credentials after attackers compromised the BI vendor’s development environment — and by week’s end, Sisense-issued AWS keys were circulating publicly. This piece reconstructs the five-day arc from detection to contained, explains why business-intelligence platforms are credential funnels that turn vendor CI/CD breaches into customer incidents, and extracts the third-party-risk doctrine the episode left behind for every embedded-analytics supply chain.

Continue ReadingSisense Breach: CI Credentials, AWS Keys and a CISA Advisory

BGP Hijacking’s 2023 Resurgence, and What RPKI Fixed

All through 2023, route leaks and suspected BGP hijacks kept redirecting chunks of internet traffic — events touching Rostelecom-linked infrastructure, financial services, and a persistent streak of cryptocurrency-targeting interception paths. None matched the famed mass redirections of prior years, but the pattern of brief, deniable, hard-to-attribute incidents kept routing security in the research headlines. This year-end review explains how BGP trust fails, walks the 2023 incident ledger with appropriately hedged attribution, and covers the defensive state of the art: RPKI signing crossing majority coverage, MANRS norms, and external route monitoring.

Continue ReadingBGP Hijacking’s 2023 Resurgence, and What RPKI Fixed