Hmmnm
All articles published by

Hmmnm

Hands-on cybersecurity tutorials, CVE breakdowns, and guided learning paths. Every technique is explained, tested, and paired with its mitigation — so you learn the attack and the defense together.

Learning Paths · About Hmmnm · Editorial policy

Oldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call

A remote intruder raised a Florida treatment plant’s lye setpoint from 100 to 11,100 ppm and an operator watching the screen reverted it in minutes. The incident file on shared passwords, exposed TeamViewer, and why OT security failed at a municipal water utility.
Continue ReadingOldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call

Emotet Takedown: How Police Dismantled the World’s Most Dangerous Malware

The incident file on Operation Ladybird: how eight countries dismantled Emotet’s 700-server botnet from inside its own update mechanism, why the loader-as-a-service model made Emotet the on-ramp for Ryuk and Conti ransomware, how the brand was rebuilt from TrickBot within ten months, and what the takedown teaches about the ceiling of law-enforcement disruption.

Continue ReadingEmotet Takedown: How Police Dismantled the World’s Most Dangerous Malware

SonicWall SMA Zero-Day: Inside the January 2021 SSL-VPN Campaign

Days after SUNBURST, researchers caught attackers exploiting a 9.8-severity SQL injection in SonicWall SMA 100 appliances — including against SonicWall’s own network. This incident file covers how unauthenticated credential extraction turned edge appliances into ransomware on-ramps.

Continue ReadingSonicWall SMA Zero-Day: Inside the January 2021 SSL-VPN Campaign

SolarWinds SUNBURST: Inside the Supply-Chain Attack That Rewrote Security

The full incident file on the SolarWinds SUNBURST supply-chain attack: how SVR-linked actors compromised the Orion build pipeline, trojanized signed updates reaching 18,000 customers, hand-picked under 100 targets including nine US federal agencies, and forged SAML tokens to persist. Includes the technical anatomy, timeline, impact numbers, and the build-pipeline hardening lessons that still define defender programs in 2026.

Continue ReadingSolarWinds SUNBURST: Inside the Supply-Chain Attack That Rewrote Security
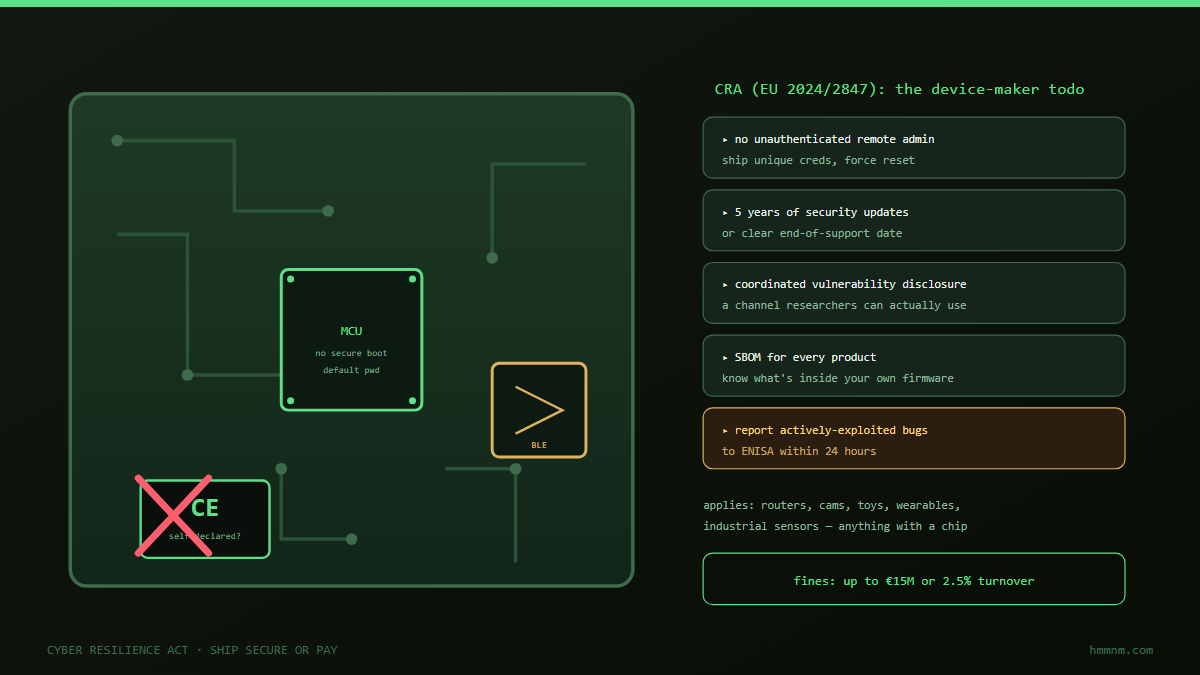
Read more about the article The Cyber Resilience Act: Security Is the Product Now
Cyber Resilience Act CE mark circuit board obligations

The Cyber Resilience Act: Security Is the Product Now

From 2027 connected products without CRA-backed security lose the CE mark and the EU market. EN 303 645 already draws the floor: no default passwords, disclosure policy, update transparency. The real work is turning security into a documented lifecycle — threat models, SBOMs, tested updates — instead of a checkbox before the ceremony.

Continue ReadingThe Cyber Resilience Act: Security Is the Product Now