Engineering deep dives for builders: MCP and AI-tooling internals, API design and abuse cases, cloud and infrastructure (Terraform, Kubernetes, CI/CD), and the platform-security angles that come with them. Written by the researcher behind Hmmnm – practical, current, and tied to the security practice.

Colonial Pipeline Ransomware: One Password, 17 Emergency States

DarkSide entered through a no-MFA legacy VPN password, exfiltrated 100 GB, and encrypted Colonial’s IT — prompting a precautionary shutdown of 45% of East Coast fuel supply. Anatomy of the most policy-consequential ransomware ever.
Continue ReadingColonial Pipeline Ransomware: One Password, 17 Emergency States

App Tracking Transparency: Apple’s Consent Earthquake, Five Years On

ATT turned iOS advertising identifiers opt-in overnight, denial rates hit 80%+, and Meta booked a $10B impact. How one consent dialog restructured an ad economy — and pushed tracking into fingerprinting’s arms.

Continue ReadingApp Tracking Transparency: Apple’s Consent Earthquake, Five Years On

Oldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call

A remote intruder raised a Florida treatment plant’s lye setpoint from 100 to 11,100 ppm and an operator watching the screen reverted it in minutes. The incident file on shared passwords, exposed TeamViewer, and why OT security failed at a municipal water utility.

Continue ReadingOldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call

SolarWinds SUNBURST: Inside the Supply-Chain Attack That Rewrote Security

The full incident file on the SolarWinds SUNBURST supply-chain attack: how SVR-linked actors compromised the Orion build pipeline, trojanized signed updates reaching 18,000 customers, hand-picked under 100 targets including nine US federal agencies, and forged SAML tokens to persist. Includes the technical anatomy, timeline, impact numbers, and the build-pipeline hardening lessons that still define defender programs in 2026.

Continue ReadingSolarWinds SUNBURST: Inside the Supply-Chain Attack That Rewrote Security

How to Read Research Papers With AI: The Nine-Pass Protocol

Most people read papers wrong: linear, once, and credulously. The nine-pass protocol gives every pass one job - intake, attention residual, contradictions, citation chain, gaps, methodology, assumptions, synthesis, and the so-what test - producing verifiable artifacts at each step.

Continue ReadingHow to Read Research Papers With AI: The Nine-Pass Protocol
Read more about the article Forward Deployed Engineering: The Role AI Companies Can’t Hire Fast Enough
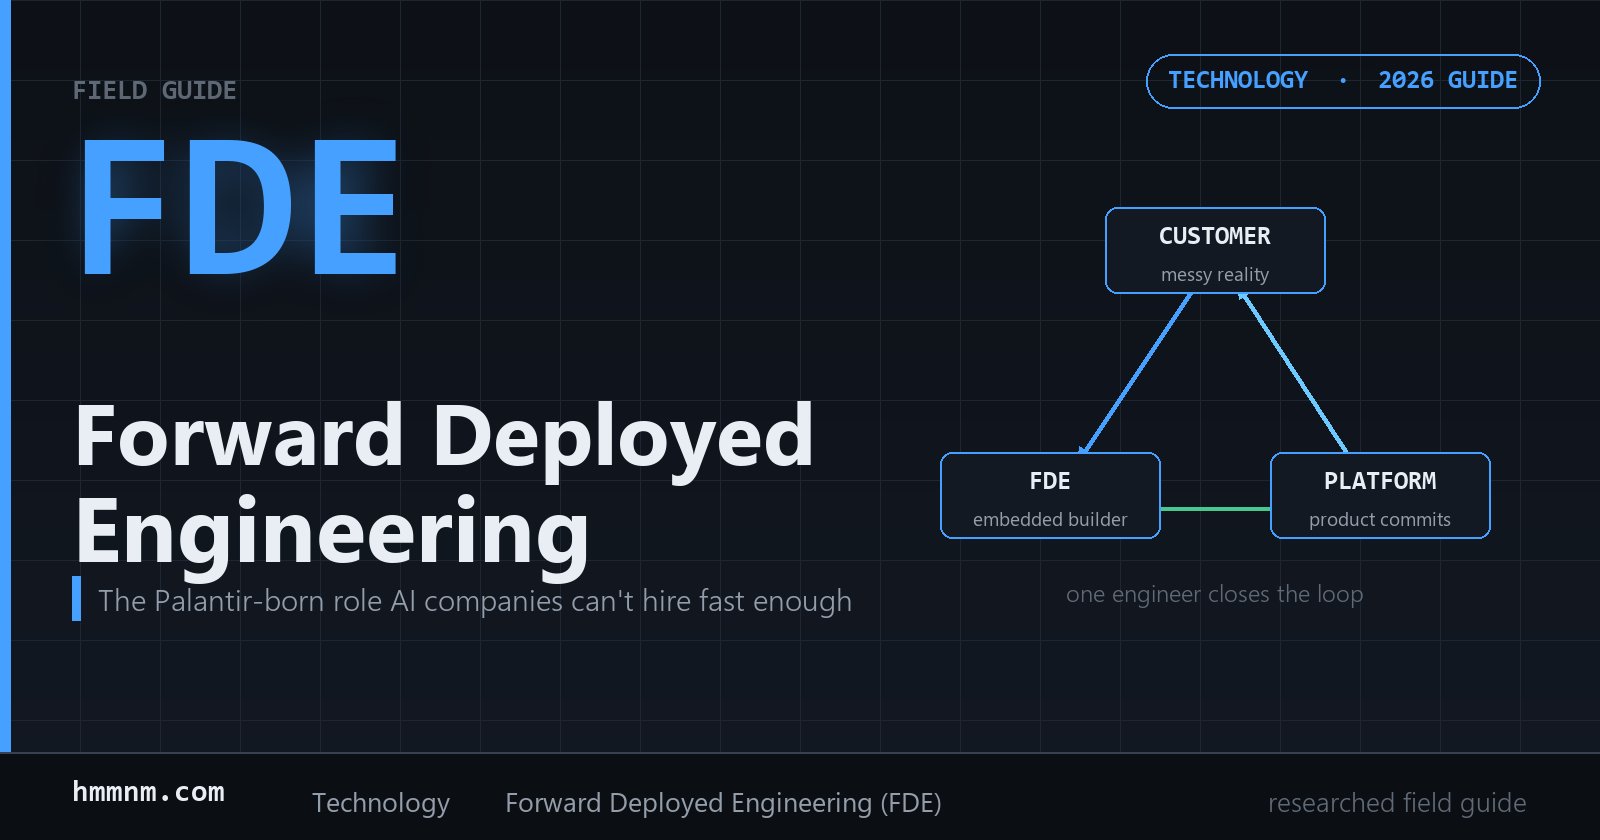
Forward Deployed Engineering featured cover – FDE role, deployer loop diagram

Forward Deployed Engineering: The Role AI Companies Can’t Hire Fast Enough

What is a forward deployed engineer? The Palantir-born role that embeds engineers inside customer environments to ship production code – and why OpenAI, Anthropic and Cursor are hiring FDEs aggressively in 2026.

Continue ReadingForward Deployed Engineering: The Role AI Companies Can’t Hire Fast Enough

AST09 & AST10: Governance and Cross-Platform Reuse

The finale of our OWASP Agentic Skills Top 10 series. AST09: one-line skill installs that no inventory, IAM system, or SOC ever sees — 800+ malicious skills circulating, 83% of organizations deploying agentic AI, 29% ready. AST10: porting skills across platforms silently drops manifests, permissions, and risk tiers. With the Bilateral Receipt Pattern, EU AI Act Article 12, and the Universal Skill Format proposal.

Continue ReadingAST09 & AST10: Governance and Cross-Platform Reuse

Zero Trust Architecture for AI Systems: Implementation Guide

Zero Trust for AI systems requires rethinking identity, data flows, and access control. Learn the five pillars of AI Zero Trust — identity verification, input validation, least privilege, monitoring, and encryption — with practical architecture patterns and implementation roadmap.

Continue ReadingZero Trust Architecture for AI Systems: Implementation Guide