HermeticWiper: Cyber Arson on Invasion Eve
Hours before tanks rolled, a signed wiper shredded hundreds of Ukrainian networks. The anatomy of the first invasion-synced destructive campaign.

Hours before tanks rolled, a signed wiper shredded hundreds of Ukrainian networks. The anatomy of the first invasion-synced destructive campaign.
Five years of notice, one expired root, and a clever cross-sign that kept old Android trusting Let’s Encrypt. The rehearsal for every future trust migration.
No malware, no zero-day — one exposed internal endpoint handed over Twitch’s entire codebase and three years of creator earnings.
A 2019 contact-import scrape of 533M users hit every phone number to profile, free-dumped in 2021 and still fueling vishing and SIM-swaps today. Why data age barely dents attacker value.
Tens of thousands of abandoned Western Digital NAS drives got factory-reset by strangers through a decade-old unpatched flaw. The definitive end-of-life IoT case study.
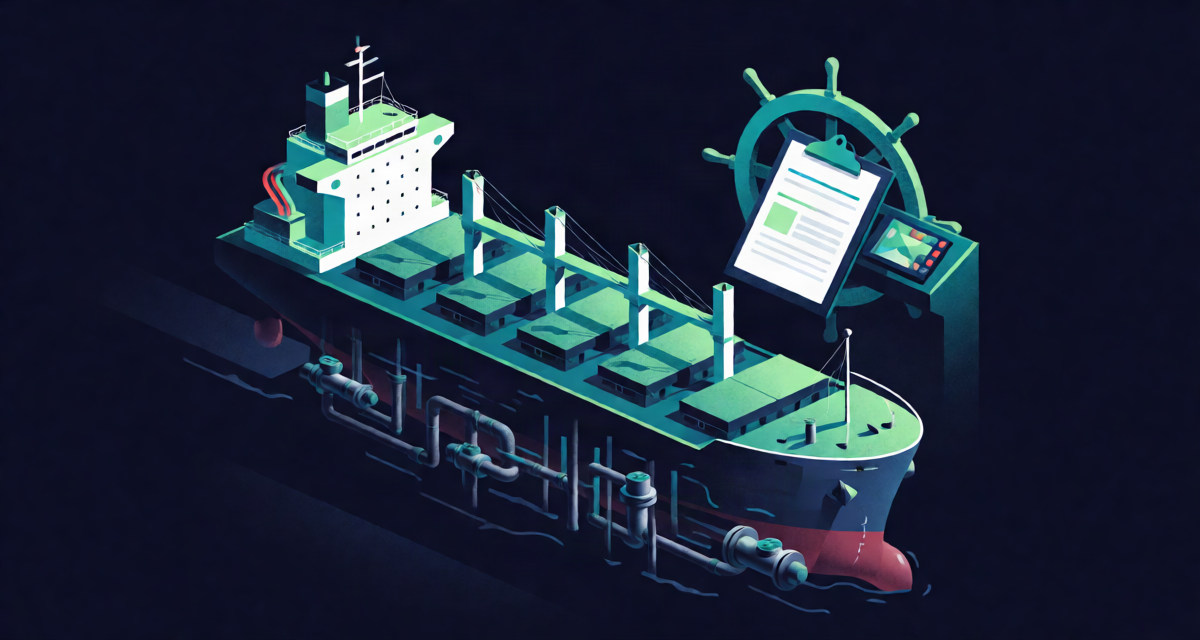
Since January 2024, ships manage cyber risk under IMO-derived requirements enforced by flag and port-state control, IACS E26 and E27 give class societies assessment criteria, and the US Coast Guard can detain deficient vessels. Bridge, cargo, propulsion, SATCOM and crew IT share one hull: treat the vessel as an OT estate.
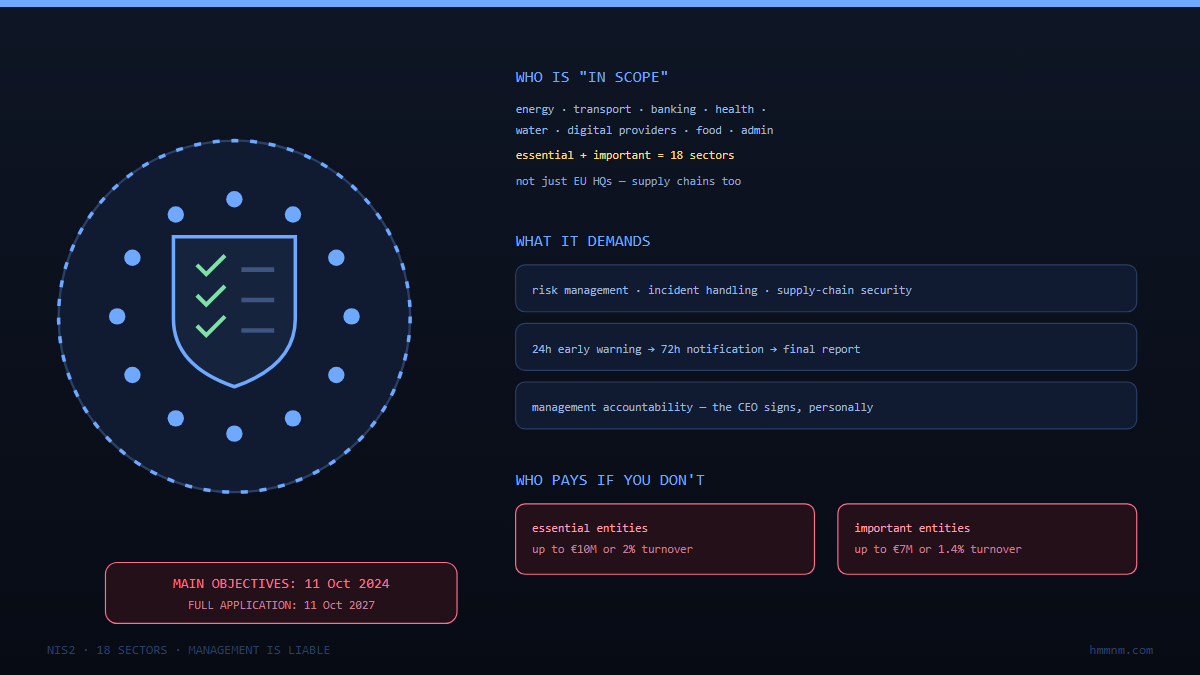
Food plants, logistics firms, waste management, research labs: 18 sectors are in scope, plus everyone their covered customers drag in via contracts. The duties read like an incident-readiness program — 24-hour early warning, 72-hour notification, personal accountability for executives — and the basics were overdue anyway.
DragonForce’s Backdoor.Turn routes ransomware C2 through Microsoft Teams TURN relays using anonymous visitor tokens — LOTI, living off trusted infrastructure. Why network detection dies and what still works.
Comprehensive guide to securing login and registration systems. Covers authentication vulnerabilities, brute-force protection, session management, CAPTCHA implementation, and security best practices.
CVE-2023-2868 gave pre-auth RCE in Barracuda’s email gateways via spreadsheet parsing, exploited since October 2022. The final verdict: replace every appliance. Remediation doctrine lessons.
Ireland’s DPC fined Meta €1.2B over EU-US transfers that Schrems II had already doomed — the largest GDPR fine ever, ordering suspension and deletion. Transfer-governance lessons for security teams.
A server-side fault in ASUS’s firmware-update mechanism crashed routers worldwide, requiring manual recovery — a global outage delivered through the trusted update path, no attacker required.