Crypto Agility After PQC: How to Avoid the Next Migration Failure
Post-quantum crypto migration is just the beginning. Crypto agility strategies to survive future cryptographic transitions.

Post-quantum crypto migration is just the beginning. Crypto agility strategies to survive future cryptographic transitions.
A practical guide to agentic AI security covering goal hijacking, tool misuse, identity and privilege abuse, memory poisoning, multi-agent trust issues, and defense frameworks for autonomous AI systems.
A practical analysis of API security authorization flaws behind modern breaches. Covers BOLA, BFLA, IDOR, mass assignment, shadow APIs, and defense strategies for API-first architectures.
Trace the evolution of phishing attacks from crude 1990s email scams to AI-powered deepfake campaigns. Discover how attackers leverage machine learning and automation to create convincing social engineering attacks.
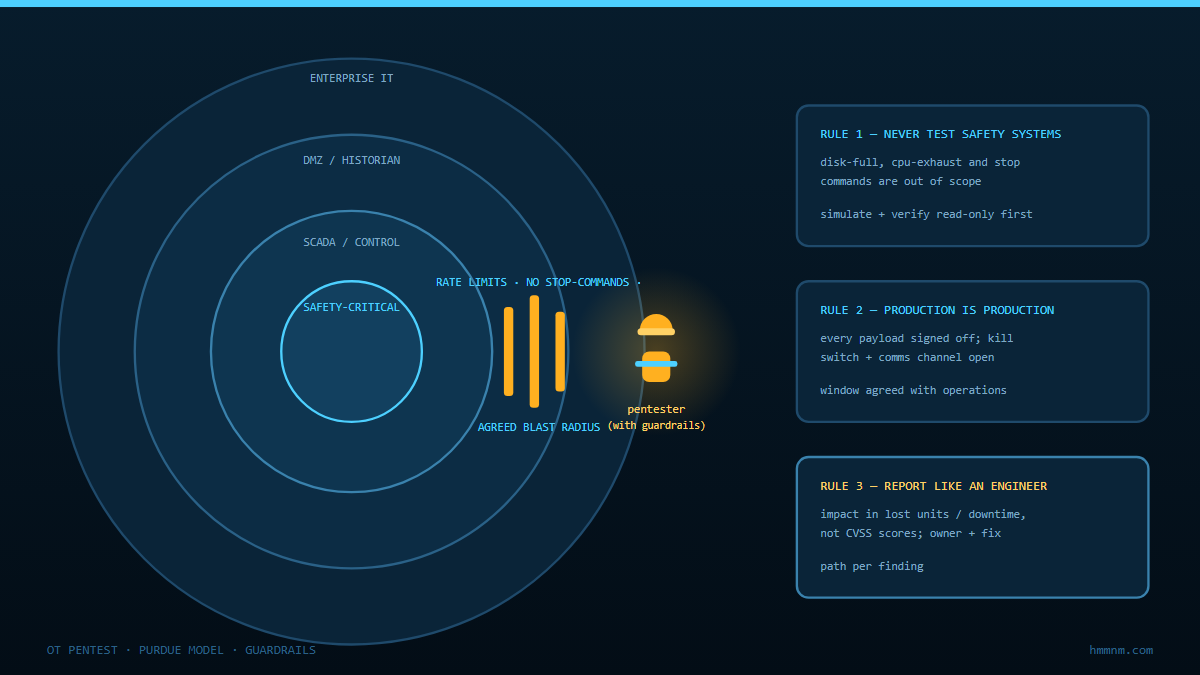
Oldsmar proved an intruder can move a plant setpoint from a browser tab. This is the safe method: passive-first discovery, read-only active testing, writes proven on clone benches, and findings ranked in downtime currency — not CVSS.
How identity became the new perimeter in modern cybersecurity. Explore MFA bypass techniques, OAuth consent phishing, device code attacks, token theft, and defense strategies for identity-centric security.
In-depth guide to HTTP request smuggling attacks. Learn how to exploit discrepancies between frontend proxies and backend servers in both HTTP/1.1 and HTTP/2 environments with practical examples.
On October 9, 2024, visitors to the Internet Archive’s Wayback Machine were greeted by an injected JavaScript pop-up announcing the compromise of 31,081,179 user accounts — the HIBP-confirmed count of the organization’s authentication database, loaned from a September exposure of its Zendesk support portal. A concurrent DDoS attributed to SN_BlackMeta compounded the disruption; days later, archived XSS attempts confirmed the org’sJavaScript security debt. This account traces the initial access, the pop-up’s evidence chain, and the funding-and-fragility story of a library built on hope.
On October 9, 2024, the FTC announced a pair of consent orders — Marriott and its Starwood subsidiary — resolving claims that skimped security contributed to the 2014-2018 Starwood intrusions and a 2018 breach affecting over 131 million consumers from which attackers extracted 5.25 million unencrypted passport numbers. The order imposes 20 years of independent assessments and a claims program offering $150 cash orotomy spending on security — close kin to the UK ICO’s £18.4M fine and the states’ $52M settlement. This account traces the 2014→2018 intrusion, the regulatory pile-on, and what a two-decade oversight tail teaches about inherited security debt.
On September 25, 2024, researchers Karan Saini and Sam Curry published an access-control flaw in Kia’s dealer and consumer web infrastructure: given only a license plate, an attacker could register an account with remote lock, unlock, start, stop, locate and horn control over 2014-2025 connected vehicles they did not own. Kia patched in August before disclosure. This account walks the plate-to-command chain, the ownership-verification gap, the threat model for tracking and theft, and the automotive-API authorization lesson that outlasts the brand.
In early October 2024, Cisco’s disclosure cadence stacked two unrelated but equally urgent problems: CVE-2024-20419, a CVSS 10.0 unauthenticated password-change flaw in Smart Software Manager On-Prem that let anyone with network access reset the admin API account, and CVE-2024-20399, a CLI command-injection bug in NX-OS already being exploited in the wild per the CISA KEV catalog. This account reconstructs both flaws’ mechanics, the patch timelines, and what this pairing says about authentication surface area in management tooling.
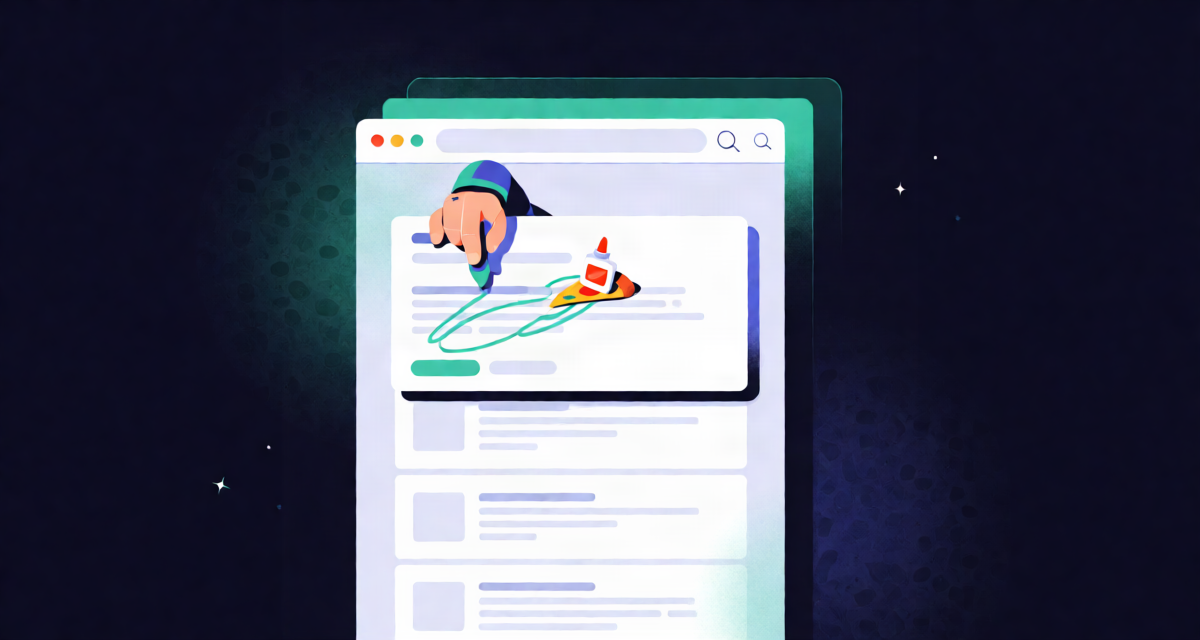
When Google rolled AI Overviews into US search in May 2024, satirical sources got quoted as fact at national scale — glue on pizza, rocks as vitamins — and security researchers reframed the comedy as indirect prompt injection: retrieved content steering the answer in Google’s own voice. This piece tracks the launch-week failures, the overview-bait SEO economy that followed, the manual-removal treadmill, provenance-aware retrieval as the real fix, and why RAG systems inherit the trust profile of their worst-cited source.