Royal Mail vs LockBit: The $80M Ransom Refusal
LockBit encrypted Royal Mail’s international sorting operations in January 2023 and demanded $80M. Royal Mail paid nothing and kept the letters moving.

LockBit encrypted Royal Mail’s international sorting operations in January 2023 and demanded $80M. Royal Mail paid nothing and kept the letters moving.
Rackspace’s December 2022 ransomware incident took Hosted Exchange down for weeks, ended the product’s life, and cost $12M+. Legacy platform lessons.
A 2023 PoC scraped the KeePass master password from memory via a rogue DLL; the maintainer called it working as designed. Both were right — and the endpoint-is-the-perimeter lesson stuck.
Git’s January 2023 advisory flagged plaintext credential stores and verbose logs echoing 2FA tokens. Developer tooling is production security surface.
The SEC’s June 2023 suits against Binance and Coinbase charged unregistered securities operations at crypto’s two biggest exchanges — a custody and platform-risk story wearing legal clothing.
Operation Cookie Monster seized the market selling browser sessions, cookies, and saved credentials for ~2M identities, with 119 arrests across 17+ countries. Session-security lessons.
LastPass confirmed attackers copied encrypted vault backups after pivoting through a DevOps engineer’s endpoint. KDF legacy and unencrypted metadata set the real risk.
Attackers compromised an Okta support engineer’s personal device, stole the session cookies inside it, and used Okta’s own support console against a customer base estimated at five percent of tenants. BeyondTrust, 1Password, and Cloudflare each detected the downstream activity independently — before the full scope was confirmed.
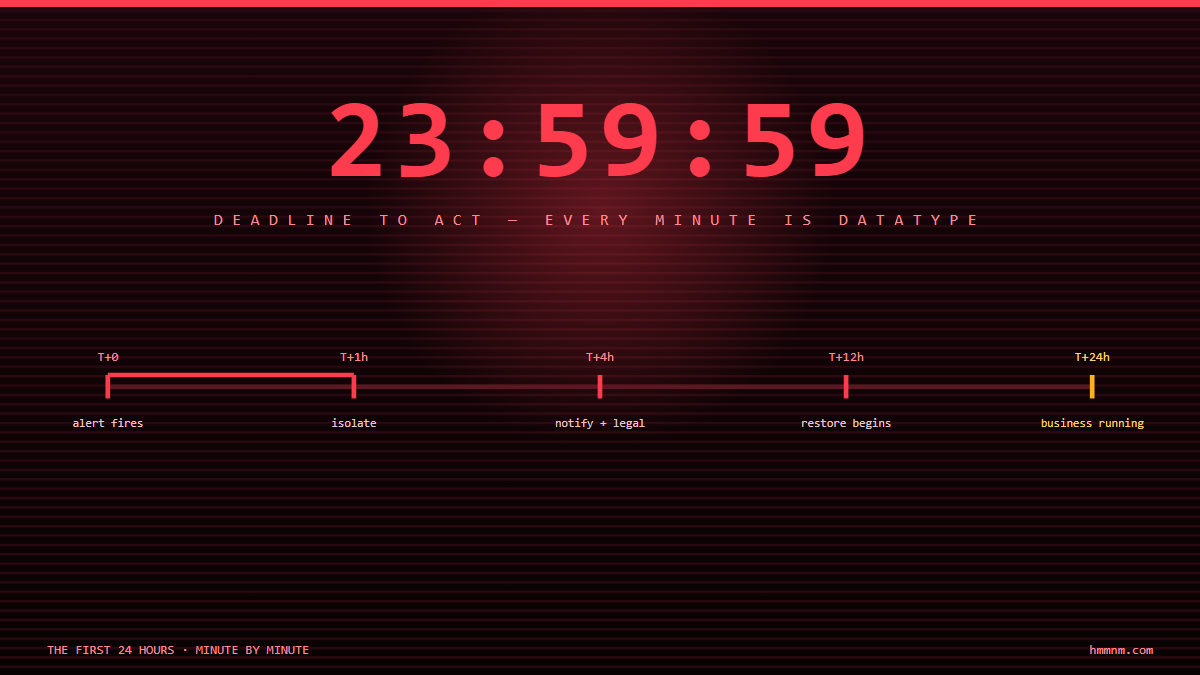
Change Healthcare lost the claims pipeline of a nation in hours. This minute-by-minute playbook covers hour zero containment, the command structure by hour four, backup verification, pay/no-pay, regulatory clocks — and the non-technical decisions that decide survival.
A defunct test tenant, a legacy password without MFA, and a residential-proxy password spray gave Russia’s Midnight Blizzard a foothold inside Microsoft’s own corporate estate in January 2024 — culminating in stolen executive email and a downstream supplier breach wave. This account explains the password-spray tradecraft, how the actors abused OAuth apps to mine mailboxes, why the failure drew a czar-memo mea culpa, and the SEC disclosure mechanics that made the saga public.
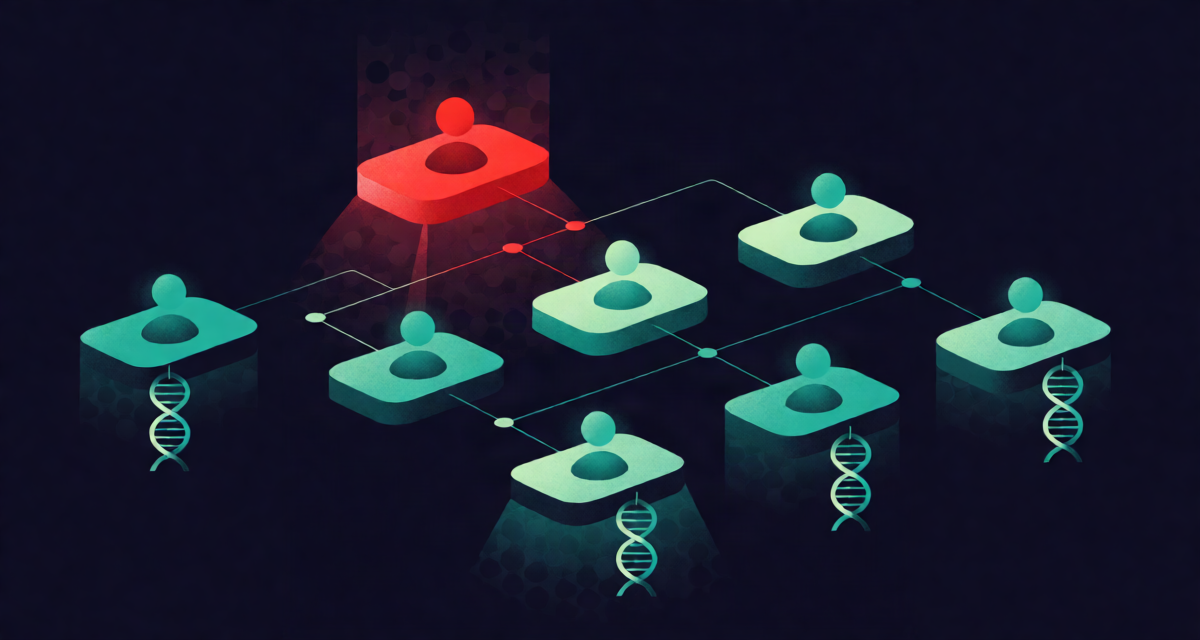
Reused passwords took over 14,000 23andMe accounts, then the DNA Relatives feature amplified the access into profile data for 6.9 million genetically-linked users. The October 2023 breach rewrote breach math: your exposure now includes every relative’s password hygiene.
ChatGPT landed November 30, 2022 and hit 100M users in two months — and immediately made prompt injection a practical attack class. Still unsolved in 2026.