Read more about the article AST01: Malicious Agent Skills (ClawHavoc Case Study)
OWASP Agentic Skills Top 10 series cover (cover_p2.png)

AST01: Malicious Agent Skills (ClawHavoc Case Study)

AST01 of the OWASP Agentic Skills Top 10 dissected: how ClawHavoc shipped 1,184 malicious skills from 12 accounts, why five of ClawHub's top seven downloads were malware, and how three lines of markdown exfiltrated SSH keys - with the full attack playbook and controls.
Continue ReadingAST01: Malicious Agent Skills (ClawHavoc Case Study)
Read more about the article Agent Skills Are the New npm: OWASP Agentic Skills Top 10 Explained
OWASP Agentic Skills Top 10 series cover (cover_p1.png)

Agent Skills Are the New npm: OWASP Agentic Skills Top 10 Explained

The OWASP Agentic Skills Top 10 maps the 10 risks of the AI-agent skill ecosystem - malicious skills, supply chain compromise, over-privileged manifests, metadata attacks, weak isolation, update drift, scanning gaps, governance failures and cross-platform reuse - with real 2026 evidence.

Continue ReadingAgent Skills Are the New npm: OWASP Agentic Skills Top 10 Explained
Read more about the article Keycloak CVE-2026-18963: Account Takeover via Password Reset
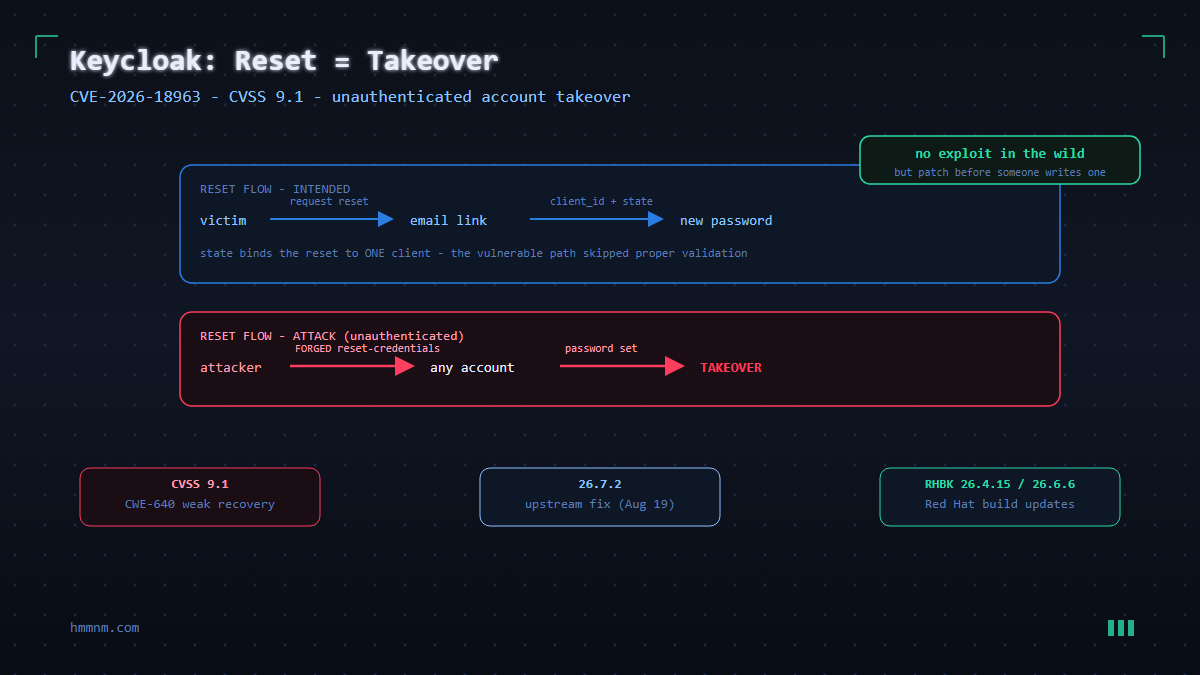
Keycloak CVE-2026-18963 reset-credentials takeover – broken handshake diagram

Keycloak CVE-2026-18963: Account Takeover via Password Reset

  • Post author:
  • Post category:Security

Keycloak's reset-credentials flow skips its own email action token: an unauthenticated attacker can set a new password on any account, including admins. CVSS 9.1, fixed in 26.7.2 - patch guide, detection hunting, and the temporary mitigation inside.

Continue ReadingKeycloak CVE-2026-18963: Account Takeover via Password Reset
Read more about the article GitLab Exploited in Days & the 86-Minute Rust Backdoor
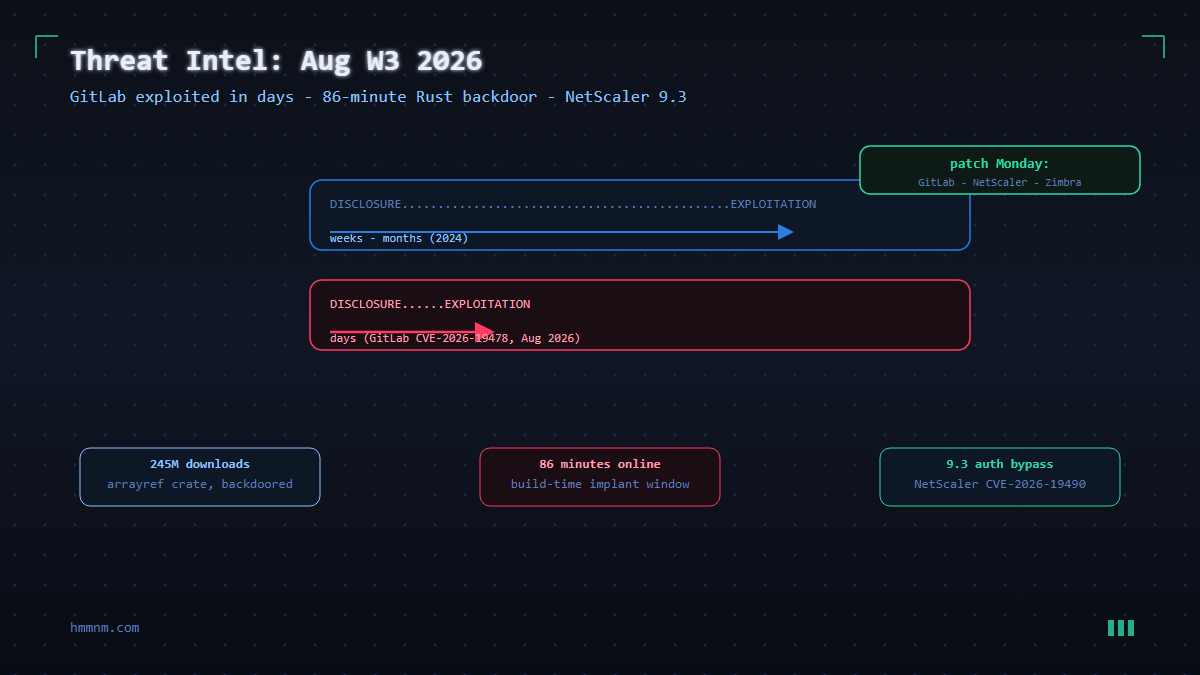
Weekly threat intelligence August 2026 W3 – disclosure-to-exploit delta clock

GitLab Exploited in Days & the 86-Minute Rust Backdoor

  • Post author:
  • Post category:Security

GitLab CVE-2026-19478 went from disclosure to in-the-wild exploitation in days; a compromised maintainer account backdoored three Rust crates with 245M downloads for 86 minutes; Citrix shipped a CVSS 9.3 NetScaler auth bypass. The week's threats, IoCs, and your Monday patch list.

Continue ReadingGitLab Exploited in Days & the 86-Minute Rust Backdoor
Read more about the article Critical Infrastructure Is the Next Target: Late-2026 Threats
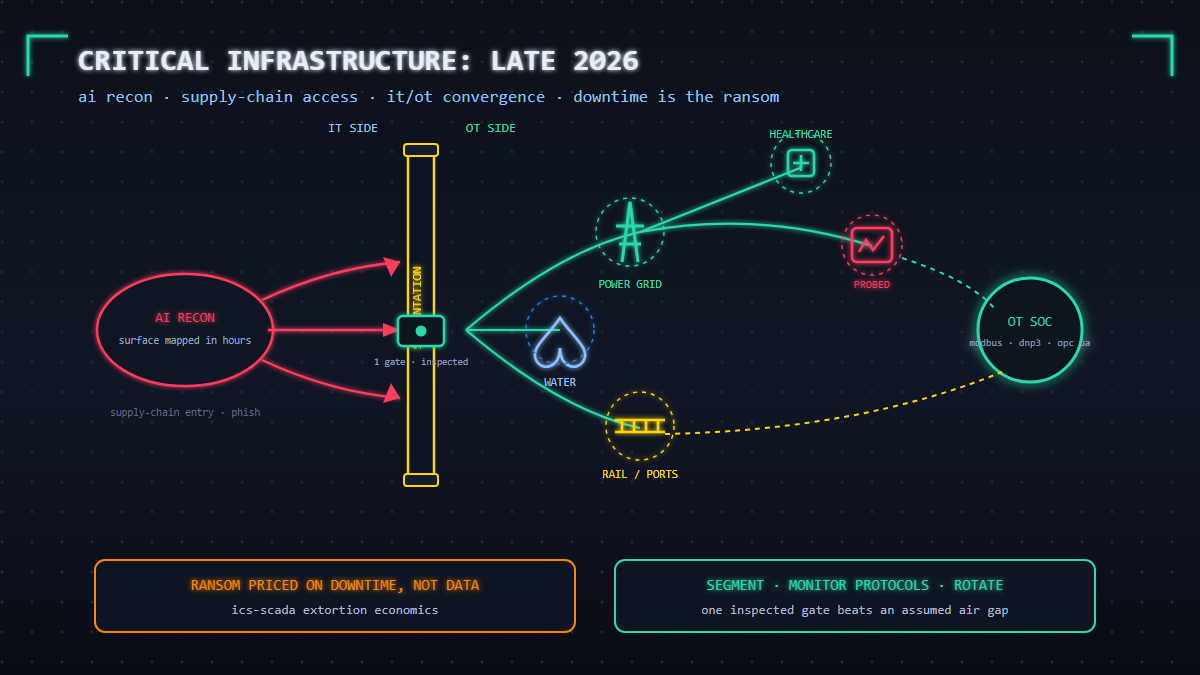
Critical infrastructure IT OT segmentation wall with inspected gate

Critical Infrastructure Is the Next Target: Late-2026 Threats

  • Post author:
  • Post category:Security

The top 5 cyber threats targeting critical infrastructure in late 2026 — AI-powered reconnaissance, supply-chain initial access, IT/OT convergence, ICS ransomware priced on downtime — with defense strategies for defenders.

Continue ReadingCritical Infrastructure Is the Next Target: Late-2026 Threats
Read more about the article AI Deepfake Attacks: Cybersecurity’s 2026 Nightmare
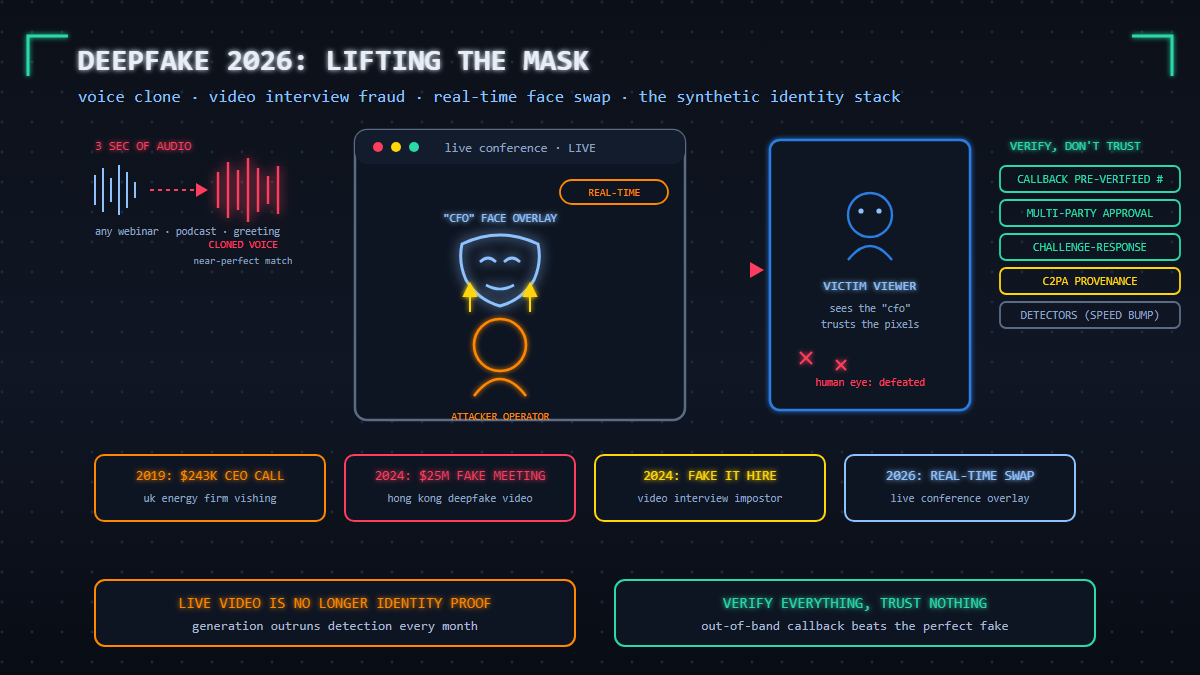
Deepfake mask lift over live video call 2026

AI Deepfake Attacks: Cybersecurity’s 2026 Nightmare

  • Post author:
  • Post category:Security

AI deepfakes have evolved from novelty to enterprise-grade attacks. Voice cloning, video impersonation, and real-time deepfakes are now the biggest threats in cybersecurity. Learn the attack scenarios, detection techniques, and defense framework every security professional needs.

Continue ReadingAI Deepfake Attacks: Cybersecurity’s 2026 Nightmare