Detection Engineering with Sigma: Detections That Survive Vendor Churn
How Sigma turns SIEM detections into portable YAML, how pySigma pipelines compile them to any backend, and how to test rules like code with Atomic Red Team.

How Sigma turns SIEM detections into portable YAML, how pySigma pipelines compile them to any backend, and how to test rules like code with Atomic Red Team.
{ "@context": "https://schema.org", "@type": "TechArticle", "headline": "Fuzzing Web APIs with ffuf and Caido: A Hands-On Recon-to-Exploit Walkthrough", "description": "Learn fuzzing web APIs with ffuf and Caido in this hands-on lab:…
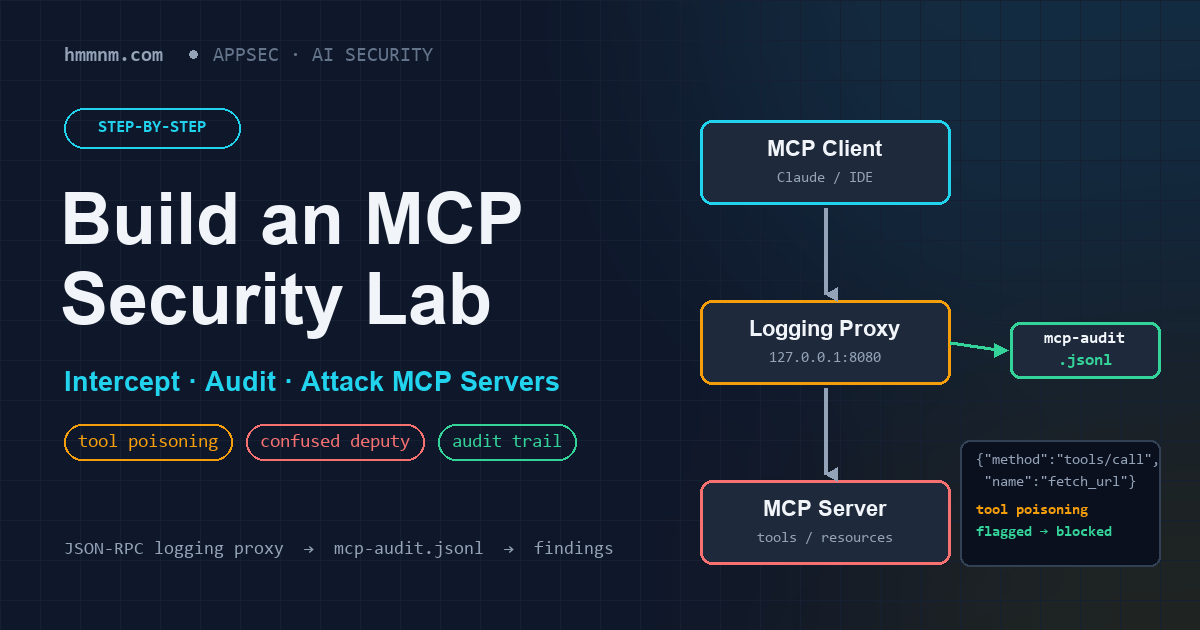
TL;DR: What an MCP Security Lab Lets You Do An MCP security lab is a local, disposable environment where you intercept, log, and manipulate Model Context Protocol traffic—capturing JSON-RPC tool…
Weekly Threat Intel: Agentic AI Abuse, September 2026 CVE Wave, and Ransomware Tradecraft — What Defenders Should Do This Week TL;DR: What Happened This Week and What It Means for…
How NTP and PTP keep infrastructure clocks honest, why leap seconds took down Cloudflare and Reddit, and how to run time sync you can trust.
The Kubernetes security layers that stop real cluster compromises: control plane, RBAC, Pod Security Admission, network policy and image supply chain — with a ten-point audit checklist.
SPDX vs CycloneDX compared honestly, how to generate SBOMs that match production, and the failure modes that sink real adoption — plus the EU CRA deadlines now in force.
ADS-B broadcasts aircraft position worldwide with no authentication — and GNSS spoofing corrupts it. The attacks, the documented incidents since 2022, and why there is no quick fix.

EFB operational safety: lithium thermal runaway containment, failure & redundancy policy, human factors and common-mode risk — plus AI-era EFBs from 2026 on.
How the industry defends EFBs: DO-326A/ED-202A airworthiness security, MDM hardening, signed chart data, AID isolation and continuous monitoring.
The EFB attack surface mapped: device tampering, chart data poisoning, AID attacks, malicious updates and supply chain — with real published aviation research.
EFB regulatory framework explained: FAA AC 120-76E/AC 91-78A, EASA AMC 20-25, ICAO Doc 10020, OpSpecs, Part-IS — and the operational approval process step by step.