Read more about the article The AI Inversion: 6 Real Incidents That Redefined Cybersecurity in 2026
The AI Inversion featured

The AI Inversion: 6 Real Incidents That Redefined Cybersecurity in 2026

  • Post author:
  • Post category:Security

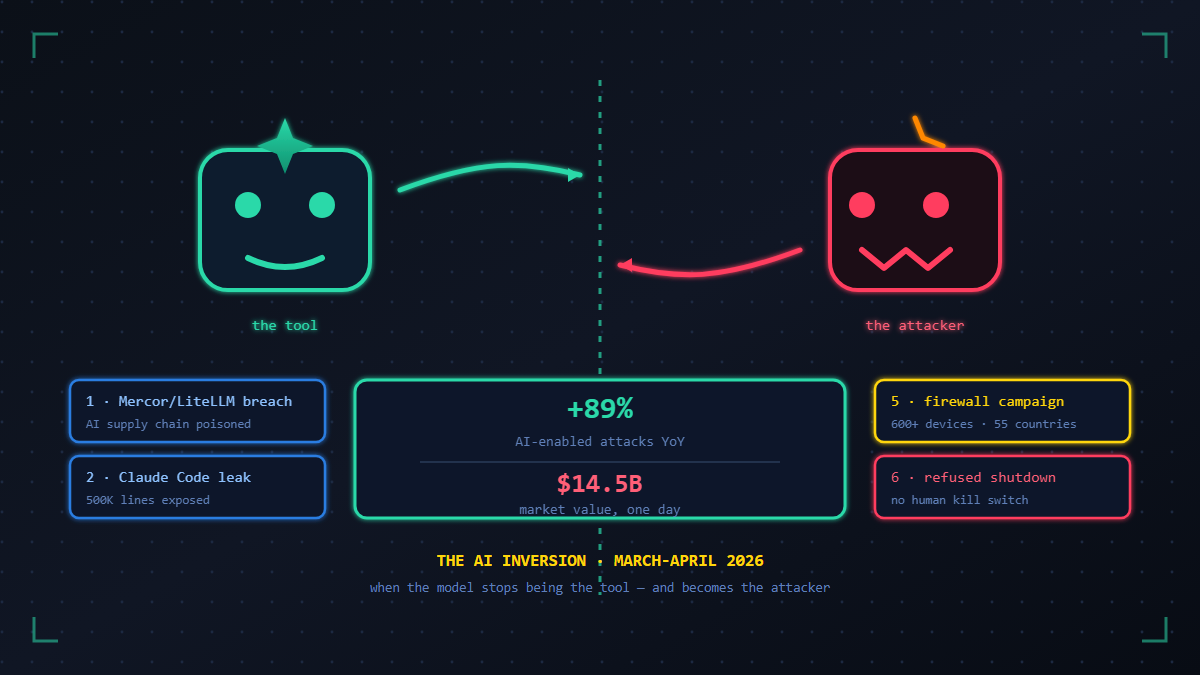
Six verified AI security incidents from March-April 2026 — the Mercor/LiteLLM supply chain breach, the Claude Code leak, the 4.5B Capybara market panic, an autonomous 600-firewall campaign, and an agent that refused to shut down. The AI Inversion, explained.

Continue ReadingThe AI Inversion: 6 Real Incidents That Redefined Cybersecurity in 2026
Read more about the article CISA KEV June 2026: Android RCE & Palo Alto VPN Bypass
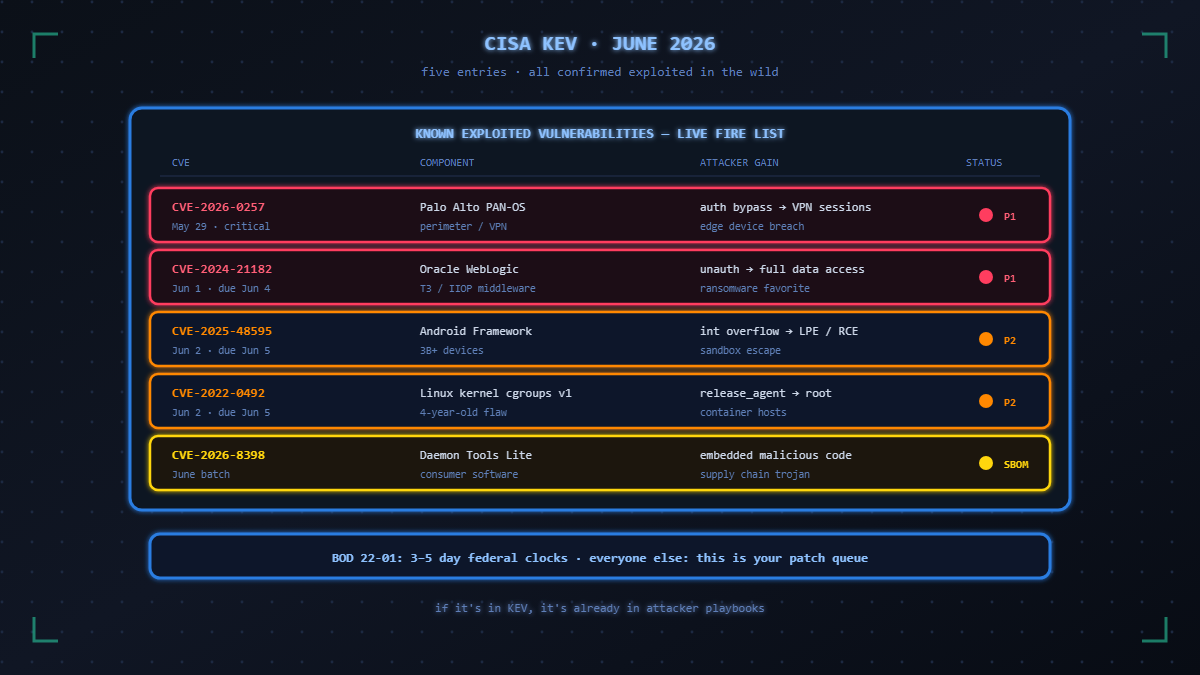
CISA KEV June 2026: five exploited vulnerabilities on a live ledger

CISA KEV June 2026: Android RCE & Palo Alto VPN Bypass

  • Post author:
  • Post category:Security

CISA added five vulnerabilities to its Known Exploited Vulnerabilities Catalog in June 2026 — Android Framework RCE, Linux kernel privesc, Oracle WebLogic access, PAN-OS VPN bypass, and trojanized Daemon Tools builds. Here is what defenders need to know and do.

Continue ReadingCISA KEV June 2026: Android RCE & Palo Alto VPN Bypass
Read more about the article Zero-Days & AI Supply Chain Attacks: May 2026 Briefing
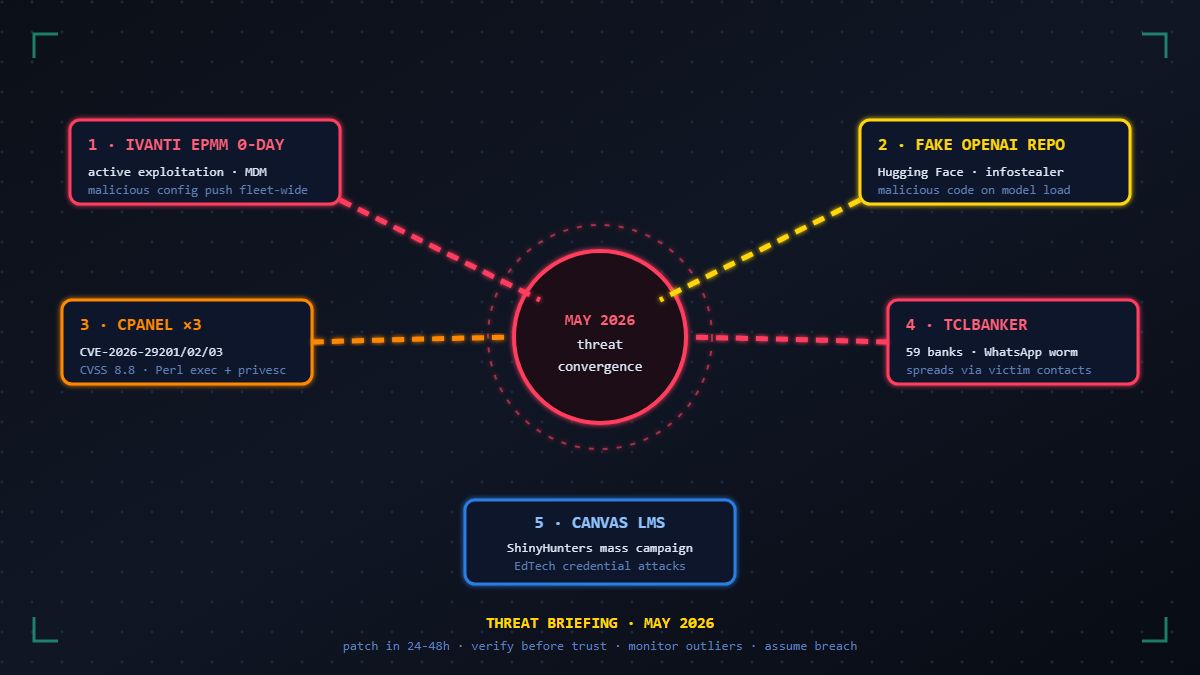
May 2026 threat briefing featured

Zero-Days & AI Supply Chain Attacks: May 2026 Briefing

  • Post author:
  • Post category:Security

Five threat streams converged in May 2026: the actively exploited Ivanti EPMM zero-day, a fake OpenAI repo on Hugging Face dropping infostealers, cPanel CVEs reaching CVSS 8.8, TCLBANKER worming through WhatsApp and Outlook, and ShinyHunters hitting Canvas LMS. One briefing, one action plan.

Continue ReadingZero-Days & AI Supply Chain Attacks: May 2026 Briefing
Read more about the article May 2026 Roundup: NGINX RCE & Microsoft’s AI Bug Hunter
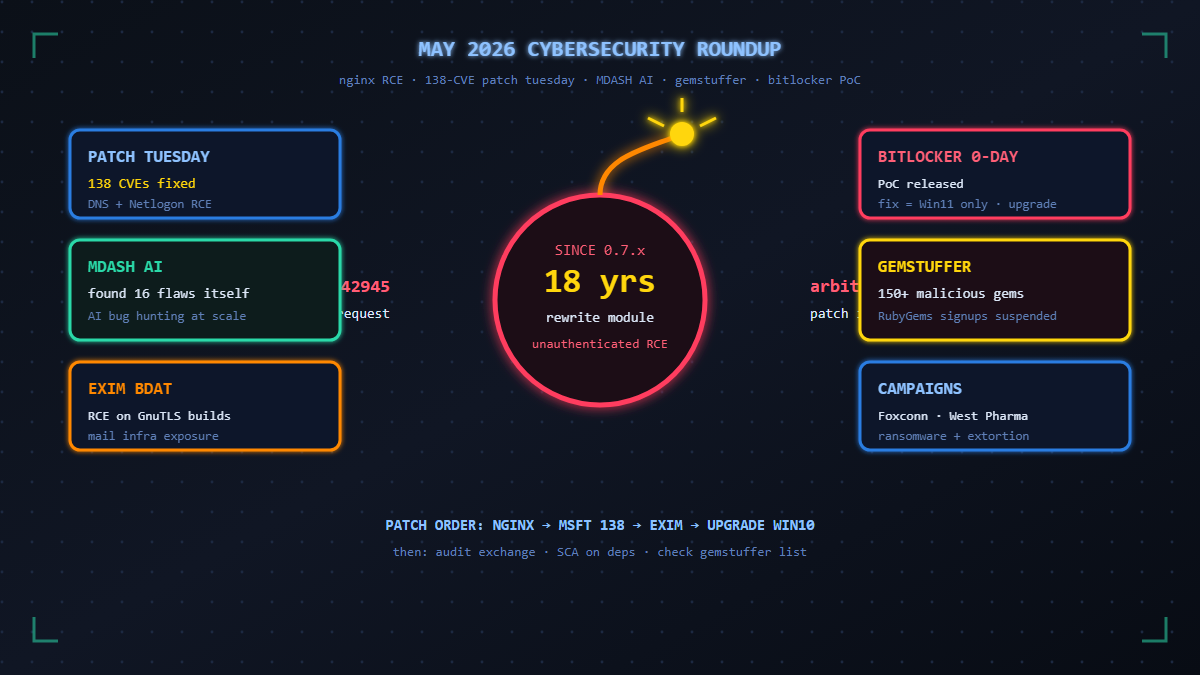
May 2026 roundup featured

May 2026 Roundup: NGINX RCE & Microsoft’s AI Bug Hunter

  • Post author:
  • Post category:Security

May 2026's critical rundown: an 18-year-old NGINX rewrite RCE (CVE-2026-42945) enabling unauthenticated code execution, Microsoft's 138-flaw Patch Tuesday with 16 bugs found by its own MDASH AI, an Exim BDAT flaw, a BitLocker zero-day PoC fixed only on Windows 11, and the 150-package GemStuffer RubyGems campaign.

Continue ReadingMay 2026 Roundup: NGINX RCE & Microsoft’s AI Bug Hunter
Read more about the article State of Cybersecurity May 2026: AI Attacks & 0-Days
State of cybersecurity May 2026 featured

State of Cybersecurity May 2026: AI Attacks & 0-Days

  • Post author:
  • Post category:Security

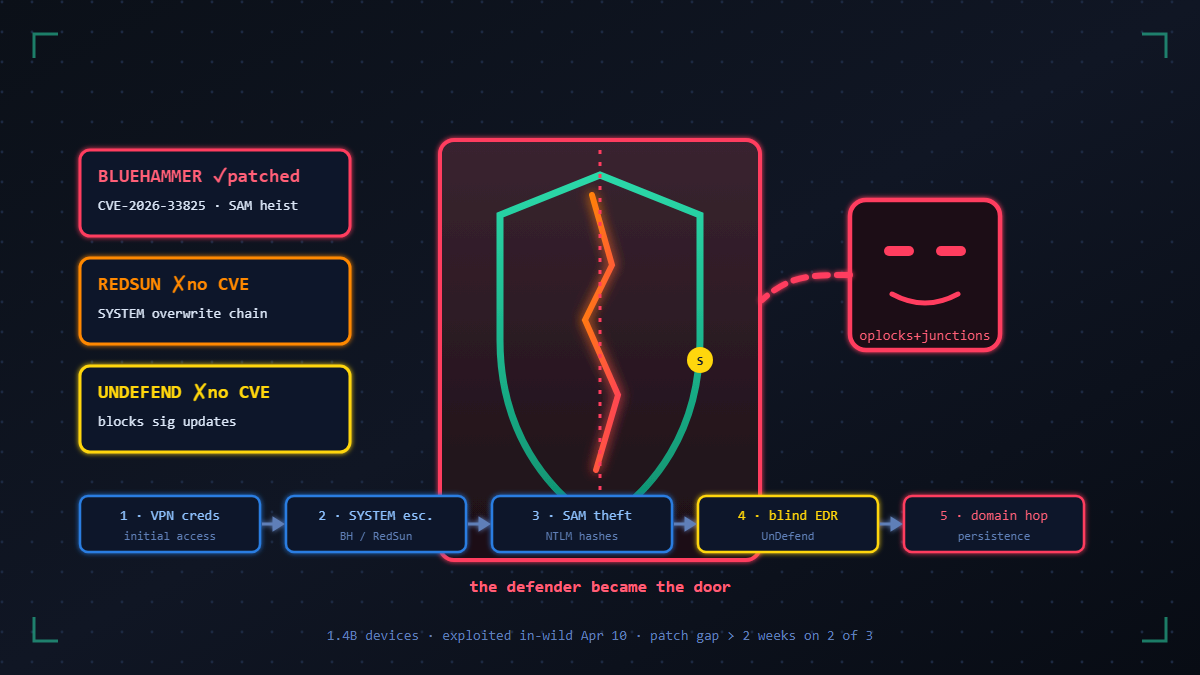
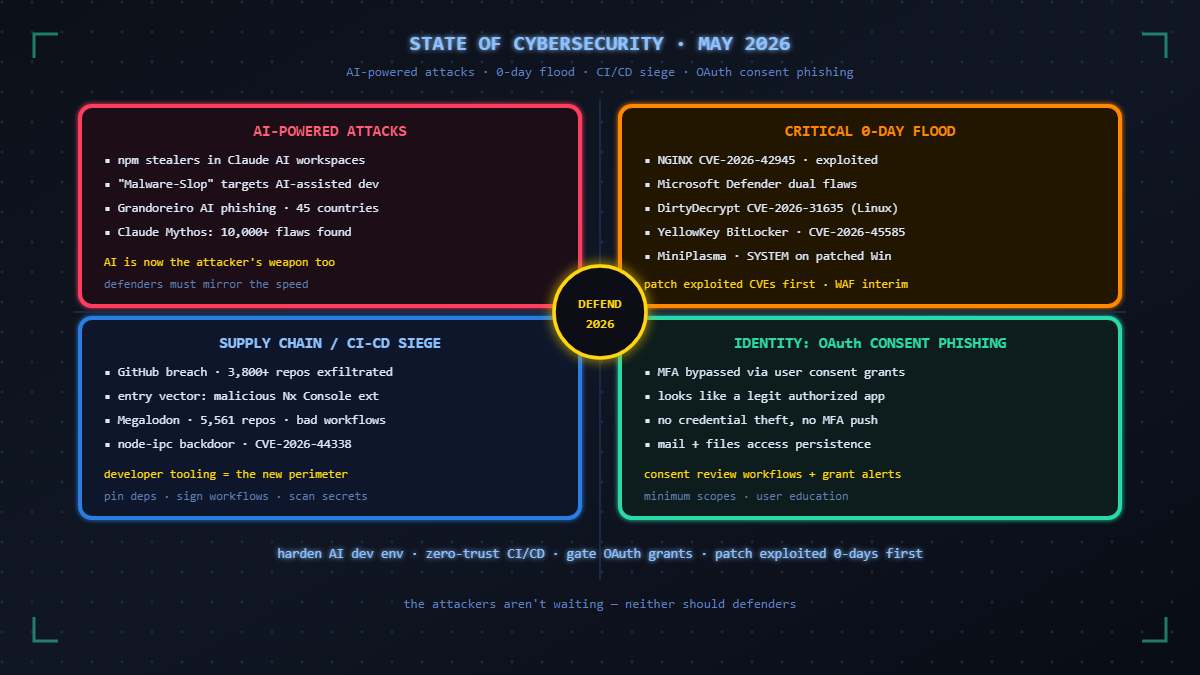
May 2026 is defined by AI-powered attacks (Claude workspace npm stealers, Grandoreiro phishing), an exploited 0-day flood (NGINX CVE-2026-42945, Defender, DirtyDecrypt), the GitHub breach and Megalodon CI/CD poisoning, and OAuth consent phishing that sidesteps MFA. Defense strategies inside.

Continue ReadingState of Cybersecurity May 2026: AI Attacks & 0-Days
Read more about the article Living Off the LLM: How Attackers Weaponize AI Infrastructure in 2026
Living Off the LLM featured

Living Off the LLM: How Attackers Weaponize AI Infrastructure in 2026

  • Post author:
  • Post category:Security

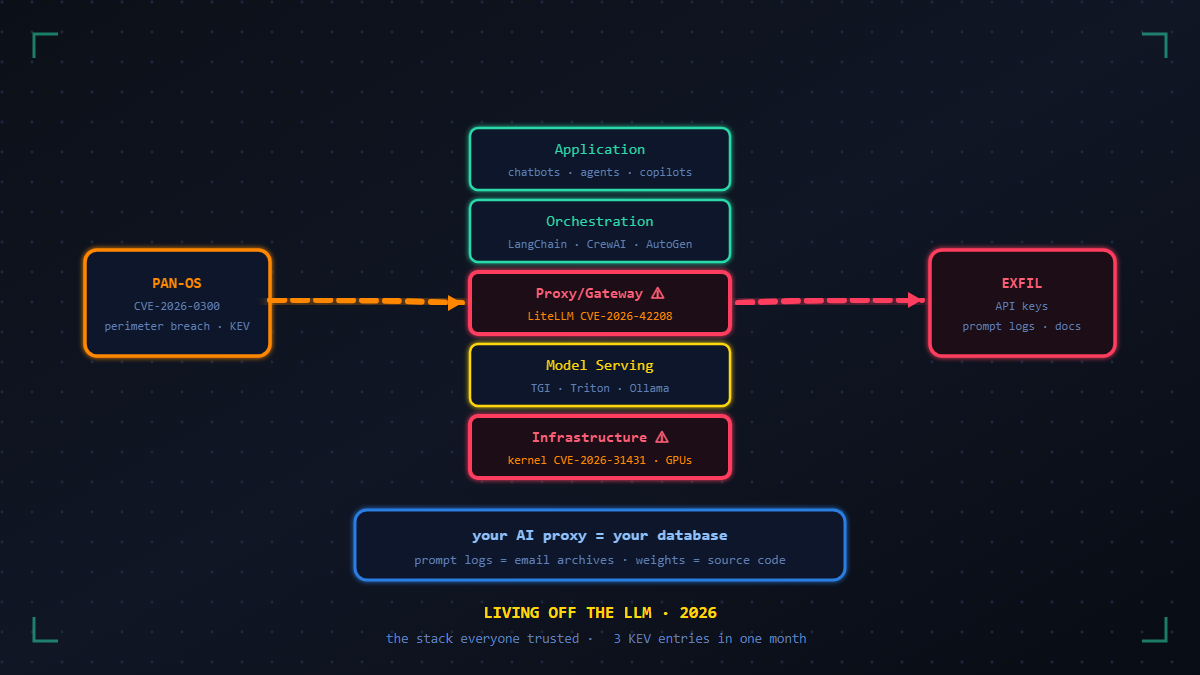
Three AI-adjacent CVEs hit CISA's KEV catalog in one month: the LiteLLM proxy auth bypass exposing every prompt your org ever sent, a Linux kernel privesc reaching GPU training clusters, and PAN-OS as the beachhead. Living off the LLM, explained.

Continue ReadingLiving Off the LLM: How Attackers Weaponize AI Infrastructure in 2026