InfraGard Portal Breach: Account Takeover Inside the Vetted
USDoD hijacked a chapter president’s InfraGard account and listed 87,000 members’ PII for sale. Identity lessons for trusted-community portals.
USDoD hijacked a chapter president’s InfraGard account and listed 87,000 members’ PII for sale. Identity lessons for trusted-community portals.
An 18-year-old bought a contractor’s Uber password, bombarded them with MFA pushes until one was approved, then roamed to vSphere via hardcoded credentials.
Furnaces halted, footage released, workers warned. How a state-aligned group turned industrial sabotage into broadcast messaging.
Hours before tanks rolled, a signed wiper shredded hundreds of Ukrainian networks. The anatomy of the first invasion-synced destructive campaign.
CVE-2021-4034 gave instant root on default Linux installs via pure logic flaw. Why setuid code still deserves emergency attention.
No malware, no zero-day — one exposed internal endpoint handed over Twitch’s entire codebase and three years of creator earnings.
Five years of notice, one expired root, and a clever cross-sign that kept old Android trusting Let’s Encrypt. The rehearsal for every future trust migration.
Tens of thousands of abandoned Western Digital NAS drives got factory-reset by strangers through a decade-old unpatched flaw. The definitive end-of-life IoT case study.
A 2019 contact-import scrape of 533M users hit every phone number to profile, free-dumped in 2021 and still fueling vishing and SIM-swaps today. Why data age barely dents attacker value.
Since January 2024, ships manage cyber risk under IMO-derived requirements enforced by flag and port-state control, IACS E26 and E27 give class societies assessment criteria, and the US Coast Guard can detain deficient vessels. Bridge, cargo, propulsion, SATCOM and crew IT share one hull: treat the vessel as an OT estate.
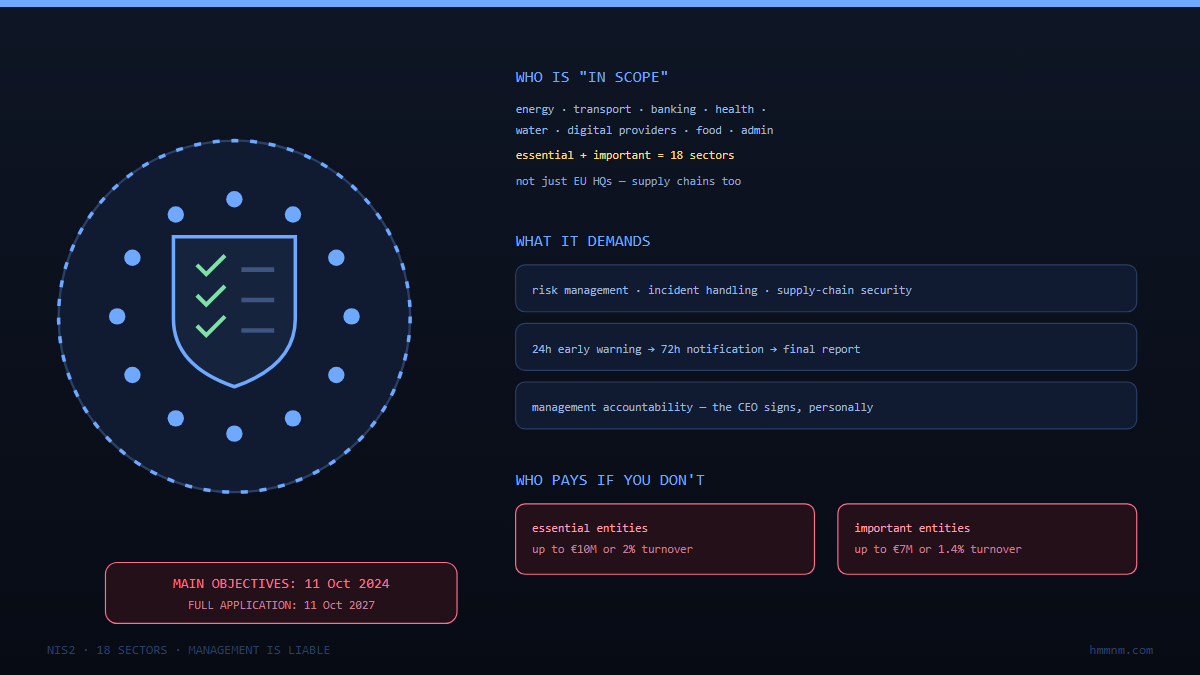
Food plants, logistics firms, waste management, research labs: 18 sectors are in scope, plus everyone their covered customers drag in via contracts. The duties read like an incident-readiness program — 24-hour early warning, 72-hour notification, personal accountability for executives — and the basics were overdue anyway.
DragonForce’s Backdoor.Turn routes ransomware C2 through Microsoft Teams TURN relays using anonymous visitor tokens — LOTI, living off trusted infrastructure. Why network detection dies and what still works.