LastPass Vault Theft Confirmed: The December Reckoning
LastPass confirmed attackers copied encrypted vault backups after pivoting through a DevOps engineer’s endpoint. KDF legacy and unencrypted metadata set the real risk.
LastPass confirmed attackers copied encrypted vault backups after pivoting through a DevOps engineer’s endpoint. KDF legacy and unencrypted metadata set the real risk.
Attackers compromised an Okta support engineer’s personal device, stole the session cookies inside it, and used Okta’s own support console against a customer base estimated at five percent of tenants. BeyondTrust, 1Password, and Cloudflare each detected the downstream activity independently — before the full scope was confirmed.
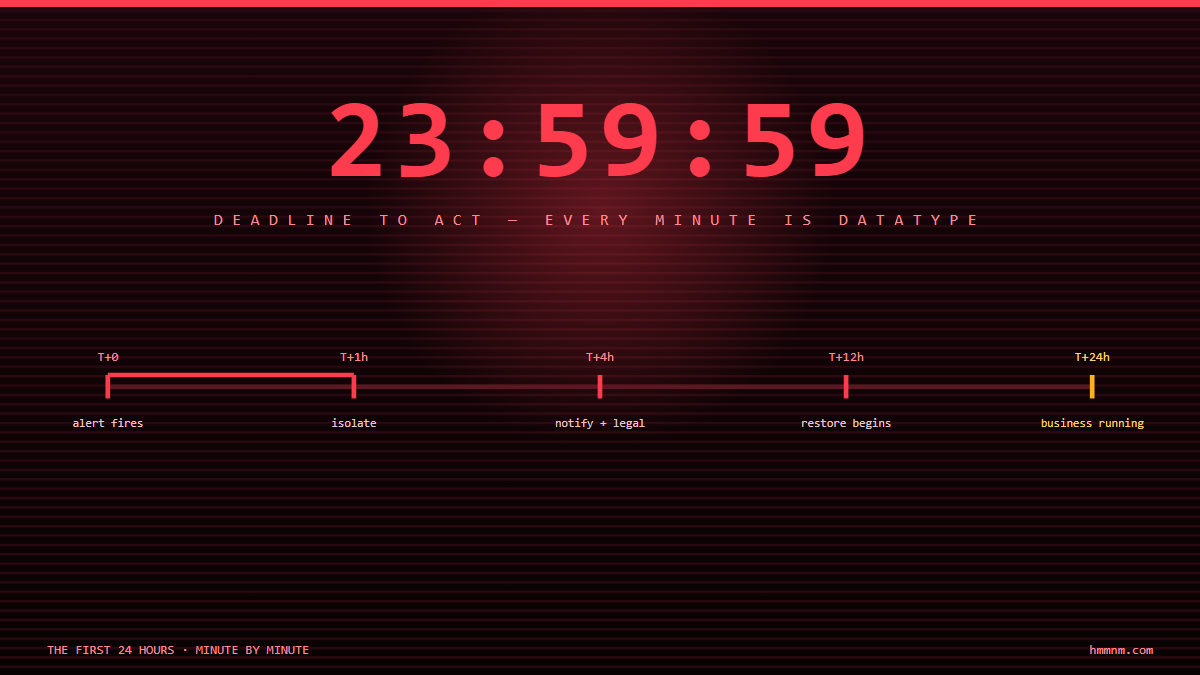
Change Healthcare lost the claims pipeline of a nation in hours. This minute-by-minute playbook covers hour zero containment, the command structure by hour four, backup verification, pay/no-pay, regulatory clocks — and the non-technical decisions that decide survival.
A defunct test tenant, a legacy password without MFA, and a residential-proxy password spray gave Russia’s Midnight Blizzard a foothold inside Microsoft’s own corporate estate in January 2024 — culminating in stolen executive email and a downstream supplier breach wave. This account explains the password-spray tradecraft, how the actors abused OAuth apps to mine mailboxes, why the failure drew a czar-memo mea culpa, and the SEC disclosure mechanics that made the saga public.
Reused passwords took over 14,000 23andMe accounts, then the DNA Relatives feature amplified the access into profile data for 6.9 million genetically-linked users. The October 2023 breach rewrote breach math: your exposure now includes every relative’s password hygiene.
ChatGPT landed November 30, 2022 and hit 100M users in two months — and immediately made prompt injection a practical attack class. Still unsolved in 2026.
When one of America’s largest mortgage servicers went dark for a week, the harm went far beyond stolen data. The Mr. Cooper incident — detected October 24, disclosed October 31, 2023 — halted payments, escrow, and payoffs for millions of borrowers, and later filings put the notification count near 14.7 million people with Social Security numbers and bank account details in the mix. This account covers the stolen-credential entry, the outage that regulators treated as the real injury, the mortgage-sector dependencies that amplified it, and the durable lessons for any payment-critical firm.
CISO guide to ransomware incident response: a complete checklist covering preparation, detection, containment, eradication, and recovery phases for enterprise environments under active ransomware attacks.
On June 19, 2024, ransomware hit CDK Global’s dealer management platform — the operational nervous system of ~15,000 North American dealerships — and a second strike during recovery extended the outage for weeks while finance desks, service bays and OEM ordering reverted to paper and fax. This account covers the June 19/22 double-hit timeline, the billion-dollar industry loss estimates, why DMS lock-in made fallback manual rather than competitive, and the concentration-risk docket the incident left for every regulator to cite.
After Squarespace absorbed roughly 10 million domains from Google Domains in mid-2024, attackers discovered a seam: legacy Google-account login flows stopped being enforced, and formerly eNom-transferred .dev/.us domains could be taken over by re-registering then-unlinked accounts. From late June through July, crypto-draining hijacks of high-value domains — including Matomo founder trust abusing Squarespace lock states — left registry operators and site owners scrambling. This account traces the migration mechanics, the attack window, and the DNS tenure lessons.
An Electronic Flight Bag replaces 40+ lbs of paper charts and manuals with certified apps - how EFBs work, their classes, and their security risks.
10 practical ethical hacking tips for beginners: certifications, labs, tools, mindset, and building your cybersecurity portfolio.