Read more about the article Keycloak CVE-2026-18963: Account Takeover via Password Reset
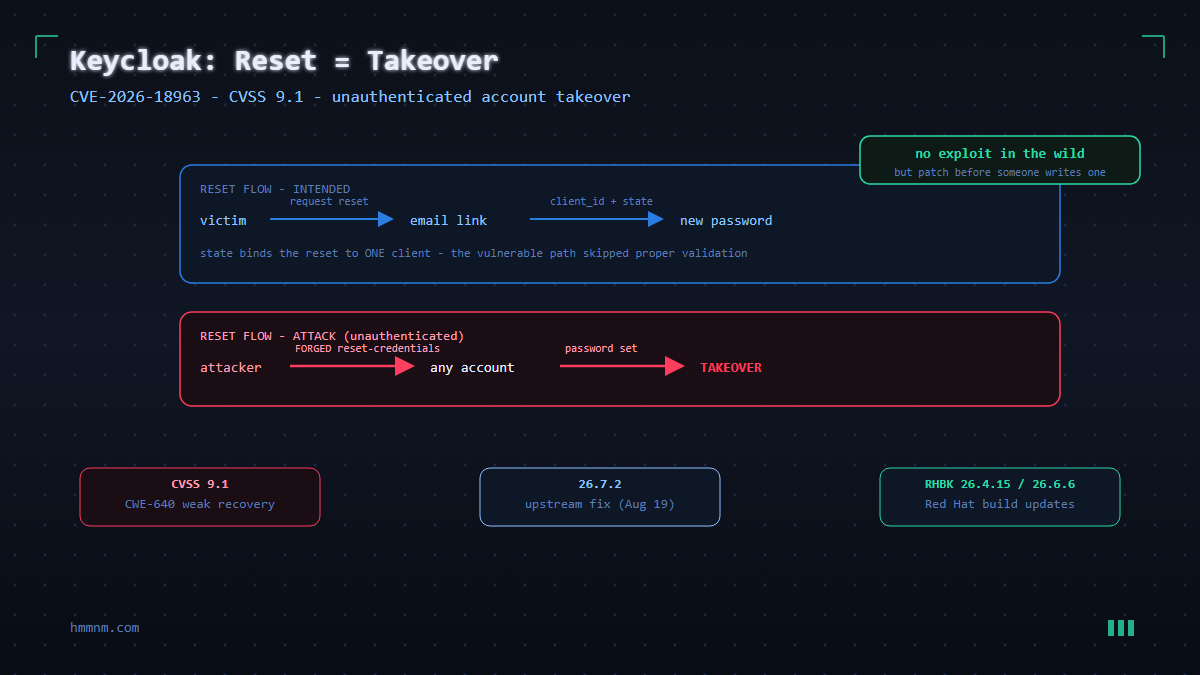
Keycloak CVE-2026-18963 reset-credentials takeover – broken handshake diagram

Keycloak CVE-2026-18963: Account Takeover via Password Reset

Keycloak’s reset-credentials flow skips its own email action token: an unauthenticated attacker can set a new password on any account, including admins. CVSS 9.1, fixed in 26.7.2 – patch guide, detection hunting, and the temporary mitigation inside.

Continue ReadingKeycloak CVE-2026-18963: Account Takeover via Password Reset

Red Teaming LLM Applications: A Practical Playbook (2026)

Red teaming LLM applications requires fundamentally different techniques than traditional penetration testing. This playbook covers the complete methodology: reconnaissance, attack execution across 5 categories, advanced adversarial ML techniques, and a reporting framework for AI security assessments.

Continue ReadingRed Teaming LLM Applications: A Practical Playbook (2026)
Read more about the article XXE Injection: A Detection and Prevention Guide
XXE Injection: A Detection and Prevention Guide

XXE Injection: A Detection and Prevention Guide

XXE Injection remains one of the most dangerous web vulnerabilities, allowing attackers to read server files, execute SSRF, and even achieve remote code execution. Master in-band, out-of-band, and blind XXE techniques with practical payload examples.

Continue ReadingXXE Injection: A Detection and Prevention Guide
Read more about the article Memory Forensics: Evidence That Never Touches Disk
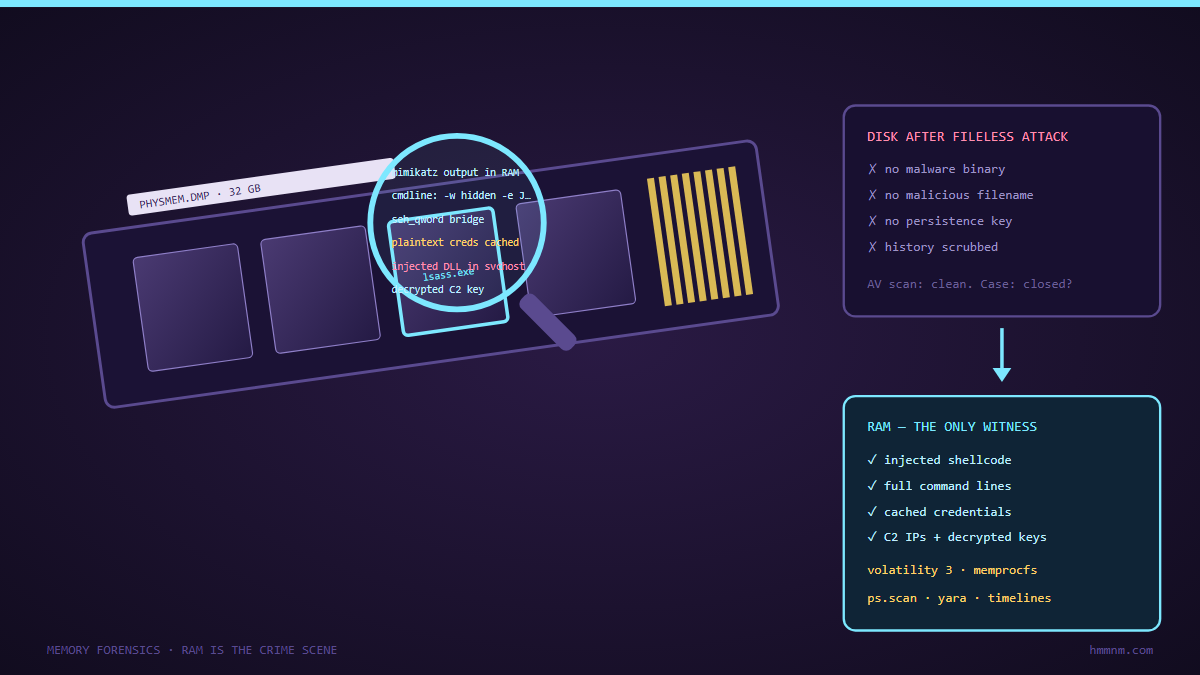
Memory forensics RAM stick under magnifier

Memory Forensics: Evidence That Never Touches Disk

Fileless attacks deleted their tracks from disk years ago. The injected shells, decrypted payloads, and cached credentials that decide an investigation live only in RAM. The acquisition-to-attribution workflow: Volatility 3 triage, MemProcFS deep dives, and the corroboration step that makes findings stand up.

Continue ReadingMemory Forensics: Evidence That Never Touches Disk