Read more about the article How to Pentest OT Networks Without Halting Production
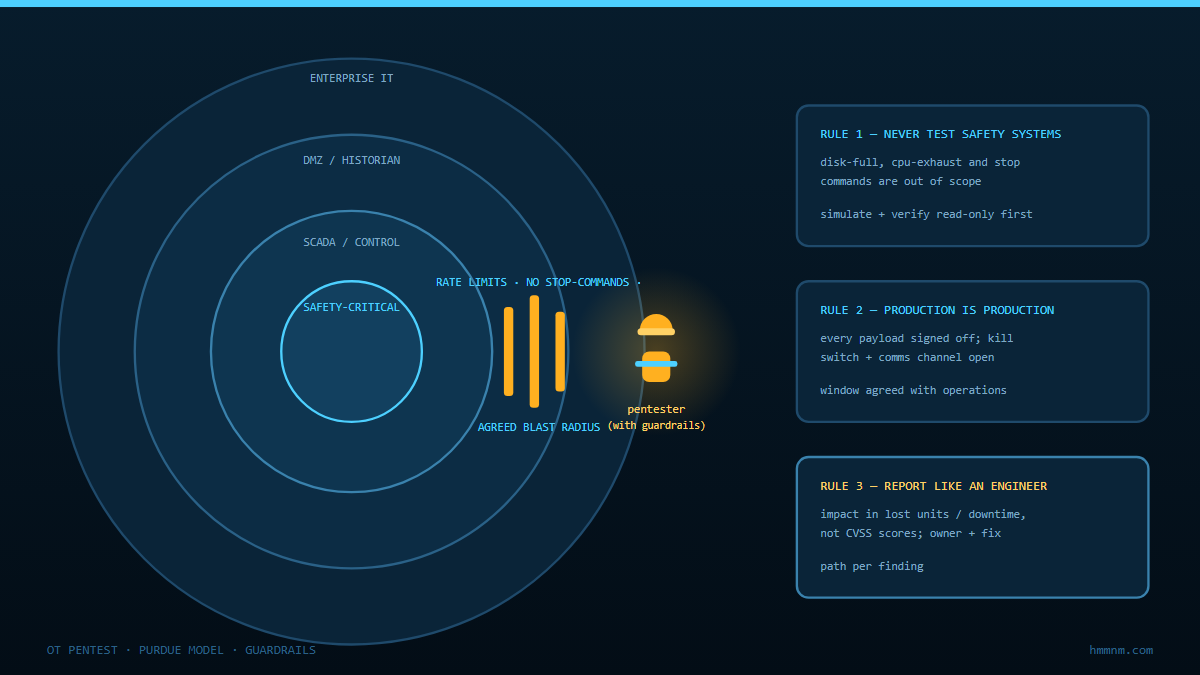
OT pentest Purdue model zones with guardrails

How to Pentest OT Networks Without Halting Production

Oldsmar proved an intruder can move a plant setpoint from a browser tab. This is the safe method: passive-first discovery, read-only active testing, writes proven on clone benches, and findings ranked in downtime currency — not CVSS.
Continue ReadingHow to Pentest OT Networks Without Halting Production

SMTP Smuggling: Spoofing Email With Authenticated Mail

December 2023 brought one of email’s most elegant attacks: SMTP smuggling, a parser-level desync that tricks receiving servers into writing attacker-authored messages that pass SPF and DMARC because the victim’s own infrastructure vouches for them. This deep dive covers the technique mechanics (end-of-data ambiguity, the second hidden MAIL FROM conversation), the December 19 disclosure and DHL demonstration, the two anchoring CVEs, which product families patched, and the durable lessons for mail admins running anything that speaks SMTP.

Continue ReadingSMTP Smuggling: Spoofing Email With Authenticated Mail

F5 BIG-IP Request Smuggling 2023: The 9.8 Desync

CVE-2023-46747 let unauthenticated attackers smuggle requests through BIG-IP TMM into the iControl REST management plane — a framing bug that became full device compromise. Exploitation followed the October patch within days, and CISA put it on the KEV catalog before month end.

Continue ReadingF5 BIG-IP Request Smuggling 2023: The 9.8 Desync
Read more about the article The Exposed .git Mistake We Keep Finding After 10 Years
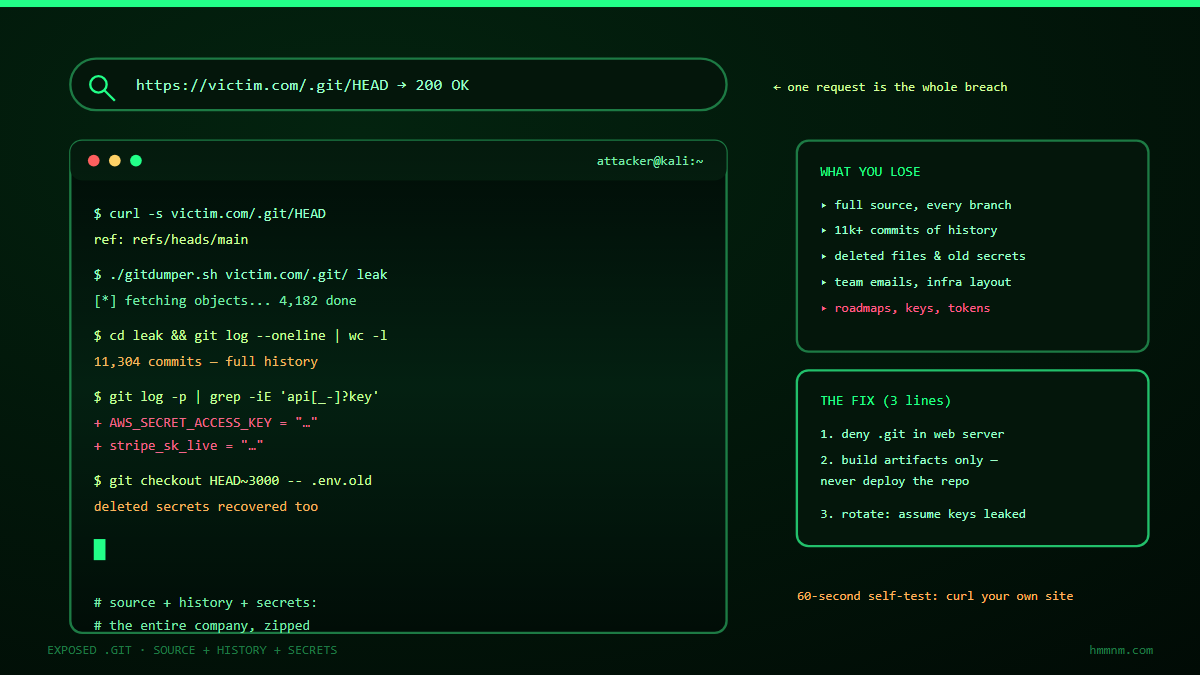
Exposed git directory terminal session

The Exposed .git Mistake We Keep Finding After 10 Years

One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.

Continue ReadingThe Exposed .git Mistake We Keep Finding After 10 Years
Read more about the article HTTP Request Smuggling: One Request, Two Interpretations
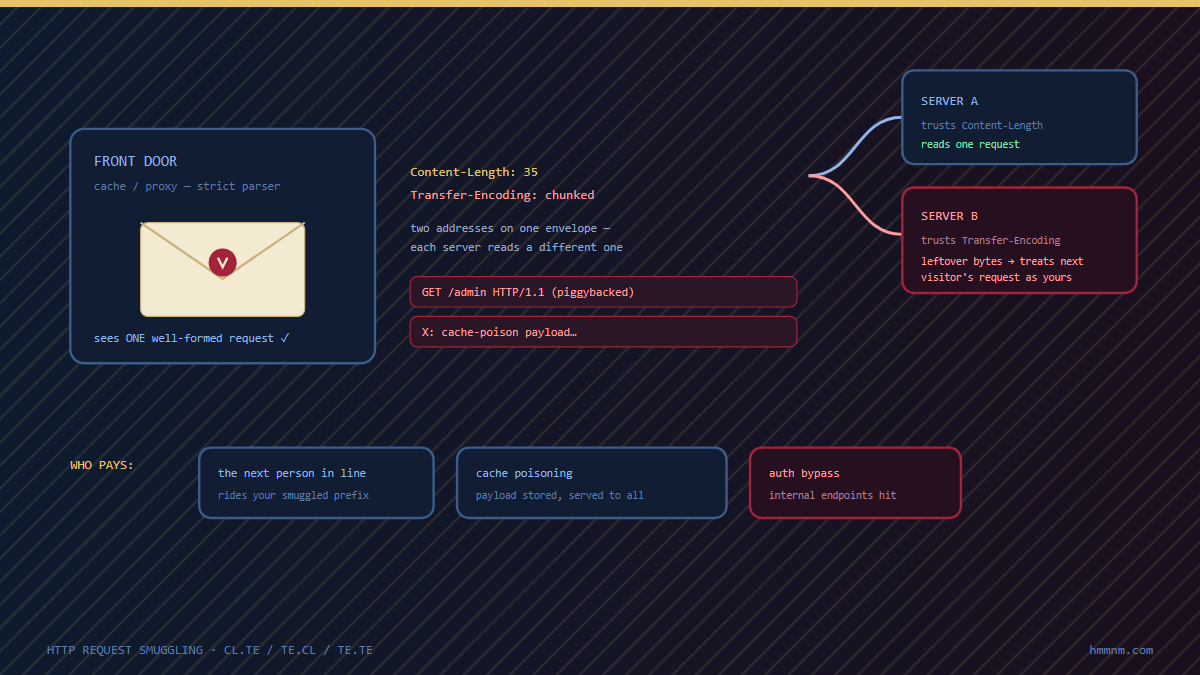
HTTP request smuggling elegant envelope desync

HTTP Request Smuggling: One Request, Two Interpretations

Your front end and your back end disagree about where one request ends and the next begins. The smuggled prefix slides under the WAF, defeats the rate limiter, and poisons the cache under someone else else URL. How CL-TE and TE-CL desyncs work, and the configuration discipline that closes them.

Continue ReadingHTTP Request Smuggling: One Request, Two Interpretations
Read more about the article CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them
CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.

Continue ReadingCORS Misconfigurations in Modern Web Apps: How to Find and Fix Them