Chrome V8 Zero-Day CVE-2021-21148: Anatomy of a Drive-By

Google’s February 2021 emergency Chrome patch opened a record zero-day year. This incident file breaks down how the V8 heap overflow worked, how it chained with a sandbox escape, why watering-hole delivery leaves no trace, and what fleet-level browser defenses it forced.
Continue ReadingChrome V8 Zero-Day CVE-2021-21148: Anatomy of a Drive-By

SonicWall SMA Zero-Day: Inside the January 2021 SSL-VPN Campaign

Days after SUNBURST, researchers caught attackers exploiting a 9.8-severity SQL injection in SonicWall SMA 100 appliances — including against SonicWall’s own network. This incident file covers how unauthenticated credential extraction turned edge appliances into ransomware on-ramps.

Continue ReadingSonicWall SMA Zero-Day: Inside the January 2021 SSL-VPN Campaign
Read more about the article The Exposed .git Mistake We Keep Finding After 10 Years
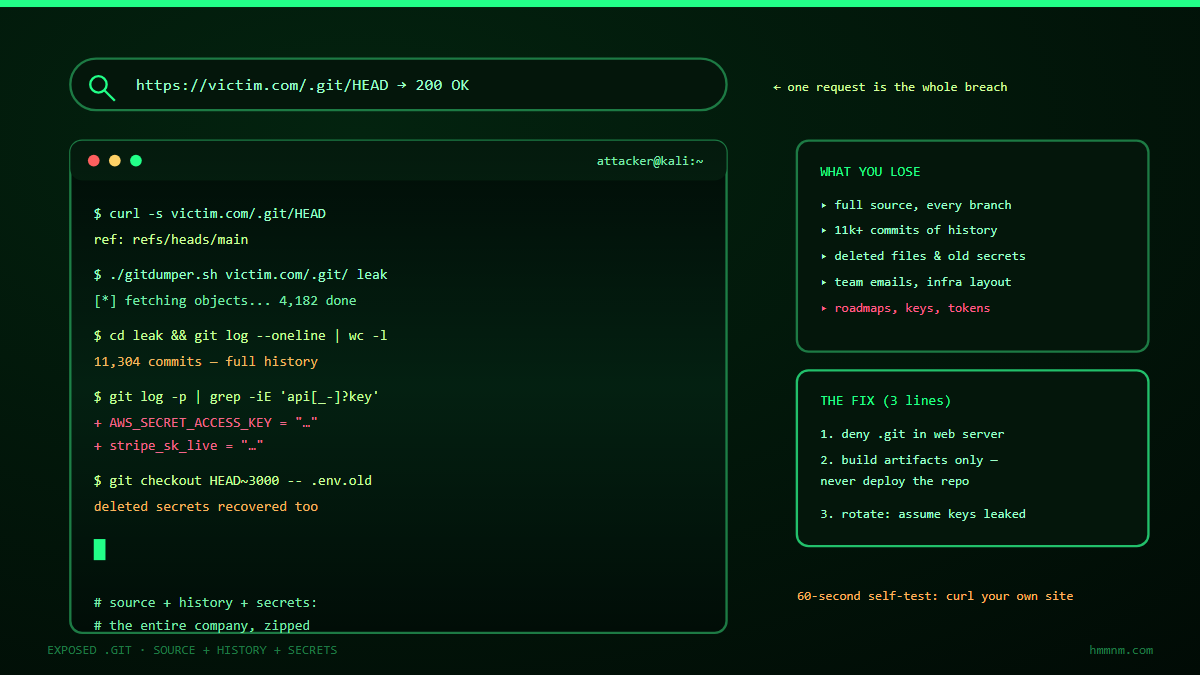
Exposed git directory terminal session

The Exposed .git Mistake We Keep Finding After 10 Years

One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.

Continue ReadingThe Exposed .git Mistake We Keep Finding After 10 Years
Read more about the article HTTP Request Smuggling: One Request, Two Interpretations
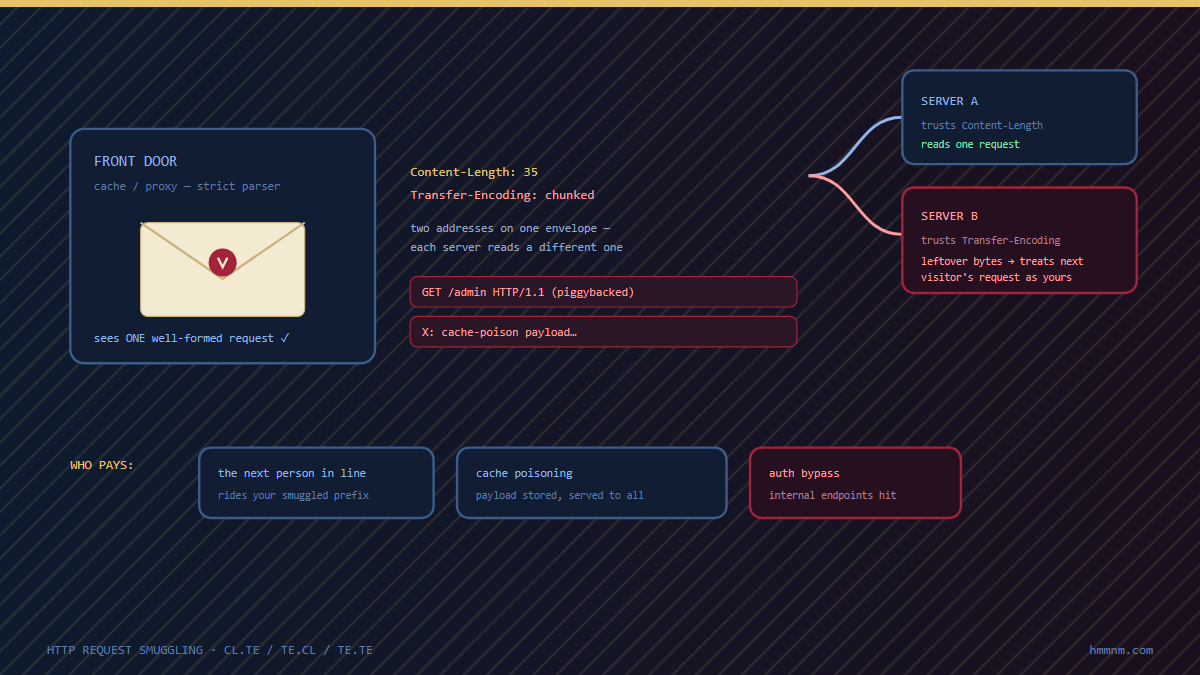
HTTP request smuggling elegant envelope desync

HTTP Request Smuggling: One Request, Two Interpretations

Your front end and your back end disagree about where one request ends and the next begins. The smuggled prefix slides under the WAF, defeats the rate limiter, and poisons the cache under someone else else URL. How CL-TE and TE-CL desyncs work, and the configuration discipline that closes them.

Continue ReadingHTTP Request Smuggling: One Request, Two Interpretations
Read more about the article AST04: Insecure Metadata and YAML Deserialization
OWASP Agentic Skills Top 10 series cover (cover_p5.png)

AST04: Insecure Metadata and YAML Deserialization

AST04 of the OWASP Agentic Skills Top 10: skill metadata is attacker-controlled input - brand impersonation, permission understating, risk-tier spoofing, invisible-character injections, and YAML !!python/object deserialization that executes code at parse time, before approval. Safe-parser and schema controls explained.

Continue ReadingAST04: Insecure Metadata and YAML Deserialization
Read more about the article AST03: Over-Privileged Skills and the DROP TABLE Problem
OWASP Agentic Skills Top 10 series cover (cover_p4.png)

AST03: Over-Privileged Skills and the DROP TABLE Problem

AST03 of the OWASP Agentic Skills Top 10: the risk where nothing is malicious and the damage still lands. Permission checks fire at tool-call level, not intent - so a SELECT-permitted skill can DROP TABLE. With Meta's inbox-deletion incident, LPCI and LAAF research, and the per-skill credential controls that close the gap.

Continue ReadingAST03: Over-Privileged Skills and the DROP TABLE Problem
Read more about the article CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them
CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.

Continue ReadingCORS Misconfigurations in Modern Web Apps: How to Find and Fix Them
Read more about the article XXE Injection: A Detection and Prevention Guide
XXE Injection: A Detection and Prevention Guide

XXE Injection: A Detection and Prevention Guide

XXE Injection remains one of the most dangerous web vulnerabilities, allowing attackers to read server files, execute SSRF, and even achieve remote code execution. Master in-band, out-of-band, and blind XXE techniques with practical payload examples.

Continue ReadingXXE Injection: A Detection and Prevention Guide