Skip to content
Hmmnm brand header logo displayed prominently across the top of the webpage
  • Home
  • Blog
  • About Us
  • Contact
  • Toggle website search
Press Escape to close the search panel.
Menu Close
  • Home
  • Blog
  • About Us
  • Contact
  • Toggle website search
Search this website

Security

  1. Home>
  2. Blog>
  3. Security>
  4. Page 2
Read more about the article Agentic AI Security Cheat Sheet: Threat Models, MCP Hardening Checklist and Detection Hooks

Agentic AI Security Cheat Sheet: Threat Models, MCP Hardening Checklist and Detection Hooks

  • Post author:Prabhu Kalyan Samal
  • Post published: October 7, 2026
  • Post category:Security

One-page agentic AI security cheat sheet: agent threat models, an MCP server hardening checklist, and the log sources and detection hooks blue teams need…

Continue ReadingAgentic AI Security Cheat Sheet: Threat Models, MCP Hardening Checklist and Detection Hooks
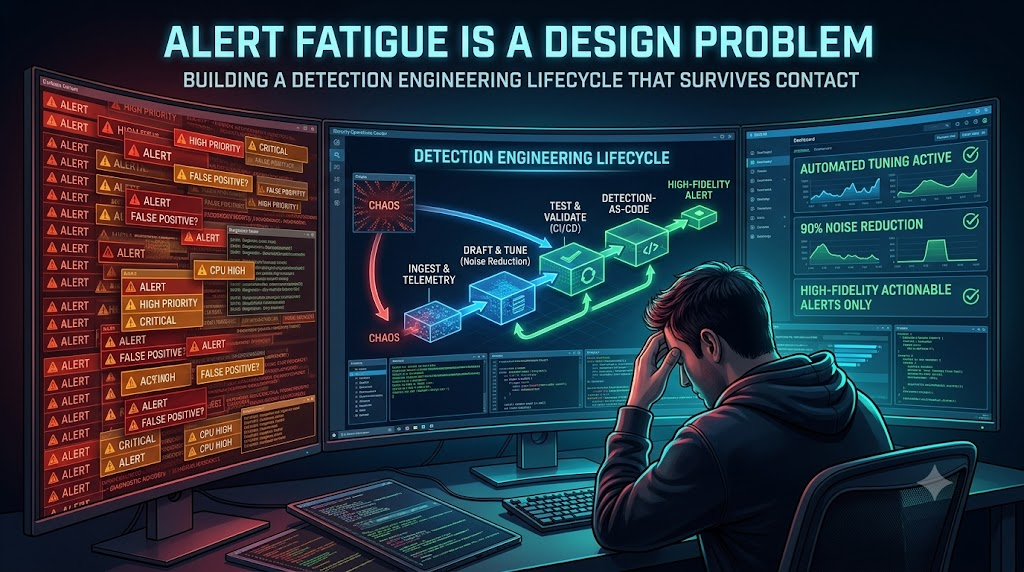
Read more about the article Alert Fatigue Is a Design Problem: Building a Detection Engineering Lifecycle That Survives Contact

Alert Fatigue Is a Design Problem: Building a Detection Engineering Lifecycle That Survives Contact

  • Post author:Prabhu Kalyan Samal
  • Post published: October 6, 2026
  • Post category:Security

Alert fatigue is a design flaw, not an analyst problem. Learn a full detection engineering lifecycle — hypothesis, build, tune, retire — with MTTD,…
Continue ReadingAlert Fatigue Is a Design Problem: Building a Detection Engineering Lifecycle That Survives Contact
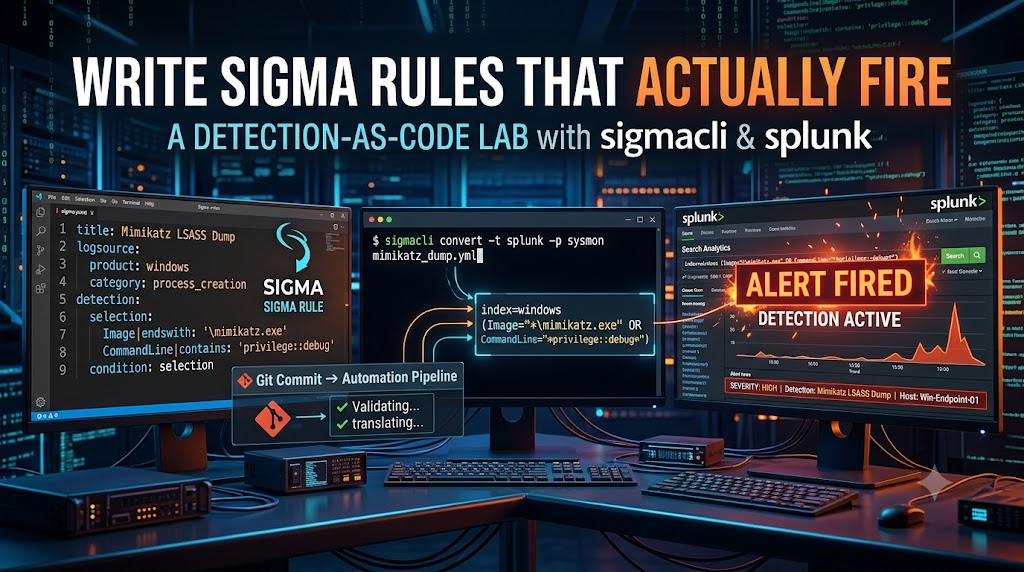
Read more about the article Write Sigma Rules That Actually Fire: A Detection-as-Code Lab with SigmaCLI and splunk-react

Write Sigma Rules That Actually Fire: A Detection-as-Code Lab with SigmaCLI and splunk-react

  • Post author:Prabhu Kalyan Samal
  • Post published: October 6, 2026
  • Post category:Security

Build a hands-on Detection-as-Code lab: author Sigma rules, validate them with sigma-cli, convert them to Splunk queries, and fire real detections in a CI…
Continue ReadingWrite Sigma Rules That Actually Fire: A Detection-as-Code Lab with SigmaCLI and splunk-react
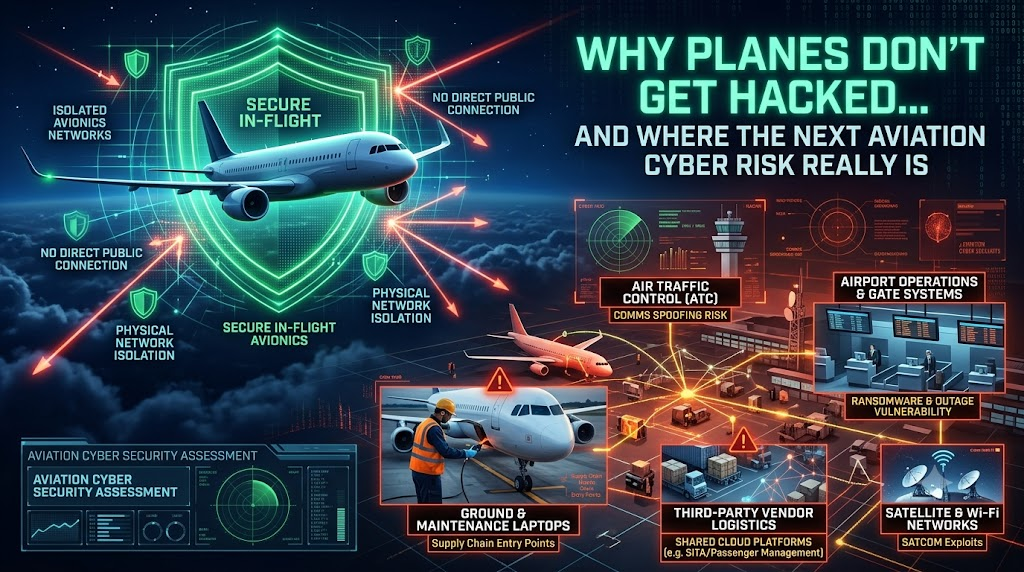
Read more about the article Why Planes Don’t Get Hacked — And Where the Next Aviation Cyber Risk Really Is

Why Planes Don’t Get Hacked — And Where the Next Aviation Cyber Risk Really Is

  • Post author:Prabhu Kalyan Samal
  • Post published: October 5, 2026
  • Post category:Security

A deep dive into aircraft cybersecurity: why planes resist hacking, the real attack surface in avionics, satcom, ADS-B, and ground systems, and where the…
Continue ReadingWhy Planes Don’t Get Hacked — And Where the Next Aviation Cyber Risk Really Is
Read more about the article What Is Prompt Injection and How to Prevent It: A Complete Exam Prep Guide

What Is Prompt Injection and How to Prevent It: A Complete Exam Prep Guide

  • Post author:Prabhu Kalyan Samal
  • Post published: October 4, 2026
  • Post category:Security

Learn what prompt injection attacks are, how they exploit LLMs, and the most effective defenses, ranked - a study guide for cybersecurity exam aspirants.
Continue ReadingWhat Is Prompt Injection and How to Prevent It: A Complete Exam Prep Guide
Read more about the article Pyramid of Pain to Production: How Detection Engineers Prioritize What to Hunt

Pyramid of Pain to Production: How Detection Engineers Prioritize What to Hunt

  • Post author:Prabhu Kalyan Samal
  • Post published: October 3, 2026
  • Post category:Security

A hands-on guide mapping the Pyramid of Pain and MITRE ATT&CK to real detection engineering decisions: what to hunt first, which telemetry to collect, and…
Continue ReadingPyramid of Pain to Production: How Detection Engineers Prioritize What to Hunt
Read more about the article Build a Free Elastic Security SOC: Ingest Sysmon, Create Dashboards and Triage Alerts

Build a Free Elastic Security SOC: Ingest Sysmon, Create Dashboards and Triage Alerts

  • Post author:Prabhu Kalyan Samal
  • Post published: October 3, 2026
  • Post category:Security

Learn how to build a free SOC lab with Elastic Security: install Sysmon, ingest Windows event logs via Winlogbeat, build detection rules, dashboards, and…
Continue ReadingBuild a Free Elastic Security SOC: Ingest Sysmon, Create Dashboards and Triage Alerts
Read more about the article Testing JWT Security with jwt-cli and Caido: Alg Confusion, Weak Secrets, and Expired Claims

Testing JWT Security with jwt-cli and Caido: Alg Confusion, Weak Secrets, and Expired Claims

  • Post author:Prabhu Kalyan Samal
  • Post published: October 3, 2026
  • Post category:Security

Hands-on tutorial covering the four most common JWT flaws—alg confusion, weak HMAC secrets, expired claims, and missing validation—using jwt-cli and Caido, with verifiable commands and hardened configs.
Continue ReadingTesting JWT Security with jwt-cli and Caido: Alg Confusion, Weak Secrets, and Expired Claims
Read more about the article Weekly Threat Intel: 30 September 2026 — npm Malware, Typosquat Waves and Autumn CVEs

Weekly Threat Intel: 30 September 2026 — npm Malware, Typosquat Waves and Autumn CVEs

  • Post author:Prabhu Kalyan Samal
  • Post published: October 2, 2026
  • Post category:Security

This week's threat intel digest: npm malware campaigns, typosquat waves, loader shifts and newly exploited CVEs — verified facts, IOCs and hands-on detection steps for practitioners.
Continue ReadingWeekly Threat Intel: 30 September 2026 — npm Malware, Typosquat Waves and Autumn CVEs
Read more about the article Evilginx3 Lab: Build a Safe AiTM Phishing Lab to Understand Session Cookie Theft (and Why FIDO2 Stops It)

Evilginx3 Lab: Build a Safe AiTM Phishing Lab to Understand Session Cookie Theft (and Why FIDO2 Stops It)

  • Post author:Prabhu Kalyan Samal
  • Post published: September 30, 2026
  • Post category:Security

Build a self-hosted Evilginx3 lab to safely study adversary-in-the-middle phishing, session cookie theft, and why FIDO2/WebAuthn defeats AiTM attacks.
Continue ReadingEvilginx3 Lab: Build a Safe AiTM Phishing Lab to Understand Session Cookie Theft (and Why FIDO2 Stops It)
Read more about the article MFA Fatigue and Push Bombing: How Attackers Wear Down Your Users

MFA Fatigue and Push Bombing: How Attackers Wear Down Your Users

  • Post author:Prabhu Kalyan Samal
  • Post published: September 30, 2026
  • Post category:Security

Deep dive into MFA fatigue and push bombing attacks: mechanics, the 2022 Uber breach, and practical defenses like number matching, rate limiting, and Conditional Access.
Continue ReadingMFA Fatigue and Push Bombing: How Attackers Wear Down Your Users
Read more about the article Shodan and Censys for Attack Surface Recon: A Hands-On OSINT Lab with Ethics Guardrails

Shodan and Censys for Attack Surface Recon: A Hands-On OSINT Lab with Ethics Guardrails

  • Post author:Prabhu Kalyan Samal
  • Post published: September 29, 2026
  • Post category:Security

Learn attack surface reconnaissance with Shodan, Censys, and crt.sh in this hands-on OSINT tutorial for blue-teamers and CTF players, with clear ethical…

Continue ReadingShodan and Censys for Attack Surface Recon: A Hands-On OSINT Lab with Ethics Guardrails
  • Go to the previous page
  • 1
  • 2
  • 3
  • 4
  • 5
  • …
  • 31
  • Go to the next page
Press Escape to close the search panel.

Categories

  • AI Security (1)
  • Aviation and Aerospace Security (9)
  • Beyond Security (2)
  • Security (370)
  • Technology (63)

Recent Posts

  • Build a Certificate Transparency Monitoring Pipeline with crt.sh and the CT Logs API (Hands-On Walkthrough)
  • Hands-On OpenSSL Lab: Generate, Inspect and Troubleshoot TLS Certificates with Real Commands
  • Build a Ransomware Sandbox with FLARE-VM and CAPE: Automated Config Extraction and IOC Dumping
  • Hunting Ransomware Pre-Encryption Behavior with Sysmon and Velociraptor: Shadow Copy Deletion, Batch Encryption, Ransom Notes
  • Weekly Threat Intel: LockBit Successor Shuffles, September 2026 Edge Device CVEs and Loader Chains
  • Weekly Threat Intel: Ransomware Affiliate Rotation, Autumn 2026 Exploitation and Infostealer Ops
  • Hunting Phishing Infrastructure with urlscan.io: Pivot from Screenshot to Campaign Takedown
  • Build a Docker Socket Escape Lab: Why Mounting /var/run/docker.sock Is a Root Kill Chain
  • Build an AiTM Phishing Lab with Evilginx: Understanding Session Cookie Theft and Detection
  • Wireshark + Scapy Lab: Replay and Dissect Aircraft ADS-B and ACARS Traffic
  • Build a PCAP Triage Lab with Zeek and T-Shark: Spot C2 Beacons in Real Traffic
  • Write YARA Rules That Catch Ransomware Families: A Detection Lab with yara-python
  • Agentic AI Security Cheat Sheet: Threat Models, MCP Hardening Checklist and Detection Hooks
  • Alert Fatigue Is a Design Problem: Building a Detection Engineering Lifecycle That Survives Contact
  • Write Sigma Rules That Actually Fire: A Detection-as-Code Lab with SigmaCLI and splunk-react

Archives

  • October 2026 (21)
  • September 2026 (272)
  • August 2026 (98)

Newsletter

Get all latest content delivered to your email a few times a month. Updates and news about all categories will send to you.
Email is required Email is not valid
This field is required
Thanks for your subscription.
Failed to subscribe, please contact admin.
Hmmnm

Our Other Sites

  • Hmmnm.in
  • Odia.hmmnm.in

Quick Links

  • Security Services
  • Learning Paths
  • About Us
  • Contact
  • Blog
  • Privacy Policy
  • Disclaimer
  • Security Products
  • Terms of Service

Contact Info

  • 📧 contact@hmmnm.com
  • 🌐 hmmnm.com
in
© 2026 @Hmmnm

We use cookies to understand how the site is used and to improve your experience. You can accept analytics cookies or continue with essential cookies only. Privacy Policy

  • Home
  • Blog
  • Security
  • Experience
  • About Us
  • Services
  • Contact