PwnKit: The 12-Year Local Root in Every Linux
CVE-2021-4034 gave instant root on default Linux installs via pure logic flaw. Why setuid code still deserves emergency attention.

CVE-2021-4034 gave instant root on default Linux installs via pure logic flaw. Why setuid code still deserves emergency attention.
Five years of notice, one expired root, and a clever cross-sign that kept old Android trusting Let’s Encrypt. The rehearsal for every future trust migration.
Tens of thousands of abandoned Western Digital NAS drives got factory-reset by strangers through a decade-old unpatched flaw. The definitive end-of-life IoT case study.
Since January 2024, ships manage cyber risk under IMO-derived requirements enforced by flag and port-state control, IACS E26 and E27 give class societies assessment criteria, and the US Coast Guard can detain deficient vessels. Bridge, cargo, propulsion, SATCOM and crew IT share one hull: treat the vessel as an OT estate.
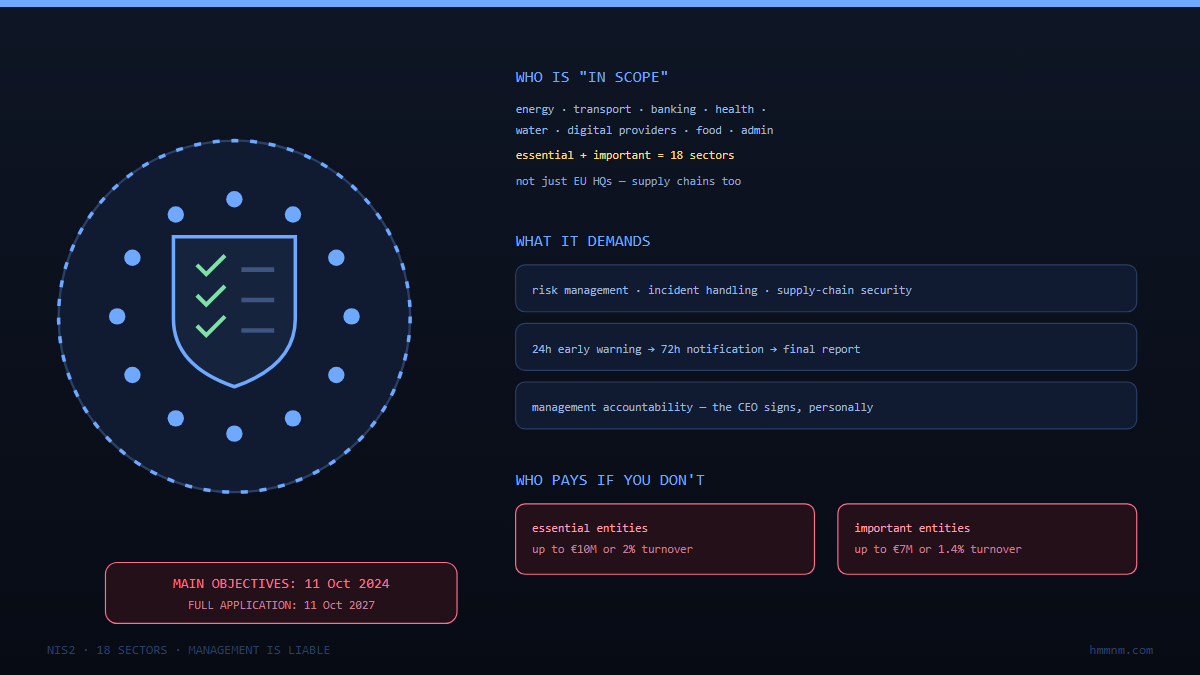
Food plants, logistics firms, waste management, research labs: 18 sectors are in scope, plus everyone their covered customers drag in via contracts. The duties read like an incident-readiness program — 24-hour early warning, 72-hour notification, personal accountability for executives — and the basics were overdue anyway.
CVE-2023-2868 gave pre-auth RCE in Barracuda’s email gateways via spreadsheet parsing, exploited since October 2022. The final verdict: replace every appliance. Remediation doctrine lessons.
A server-side fault in ASUS’s firmware-update mechanism crashed routers worldwide, requiring manual recovery — a global outage delivered through the trusted update path, no attacker required.
WD’s 2023 intrusion took My Cloud services offline mid-extortion claims, locking users out of their own files. Cloud-tethered storage lessons.
GoDaddy’s 2023 filing admitted intermittent intruder access since 2020, malware in cPanel servers, and email interception affecting ~6.95M customers.
ESXiArgs hit thousands of unpatched VMware ESXi hosts via old OpenSLP bugs in February 2023. Hypervisor ransomware and recovery-script lessons.
CVE-2023-4966 let attackers read valid session tokens out of NetScaler memory and inherit authenticated sessions wholesale — MFA already passed. CISA’s Emergency Directive 23-08 forced hunts and rebuilds as LockBit monetized the access.
Rackspace’s December 2022 ransomware incident took Hosted Exchange down for weeks, ended the product’s life, and cost $12M+. Legacy platform lessons.