Pulse Secure VPN Zero-Days: When Remote Access Became the Front Door

Pre-auth Pulse Secure exploits handed APT crews and ransomware affiliates appliance-level control of the VPNs that carried pandemic remote work. How credential capture and patch-surviving persistence rewrote edge-appliance incident response.
Continue ReadingPulse Secure VPN Zero-Days: When Remote Access Became the Front Door

HAFNIUM and Exchange Zero-Days: The 30,000-Server Compromise

Four zero-days in on-premises Microsoft Exchange let HAFNIUM and ten follow-on crews own mail servers at tens of thousands of organisations. The anatomy of the SSRF-to-web-shell chain, the PATCH NOW scramble, and why patching was not remediation.

Continue ReadingHAFNIUM and Exchange Zero-Days: The 30,000-Server Compromise

Oldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call

A remote intruder raised a Florida treatment plant’s lye setpoint from 100 to 11,100 ppm and an operator watching the screen reverted it in minutes. The incident file on shared passwords, exposed TeamViewer, and why OT security failed at a municipal water utility.

Continue ReadingOldsmar Water Plant Hack: The Five-Minute SCADA Wakeup Call
Read more about the article The Cyber Resilience Act: Security Is the Product Now
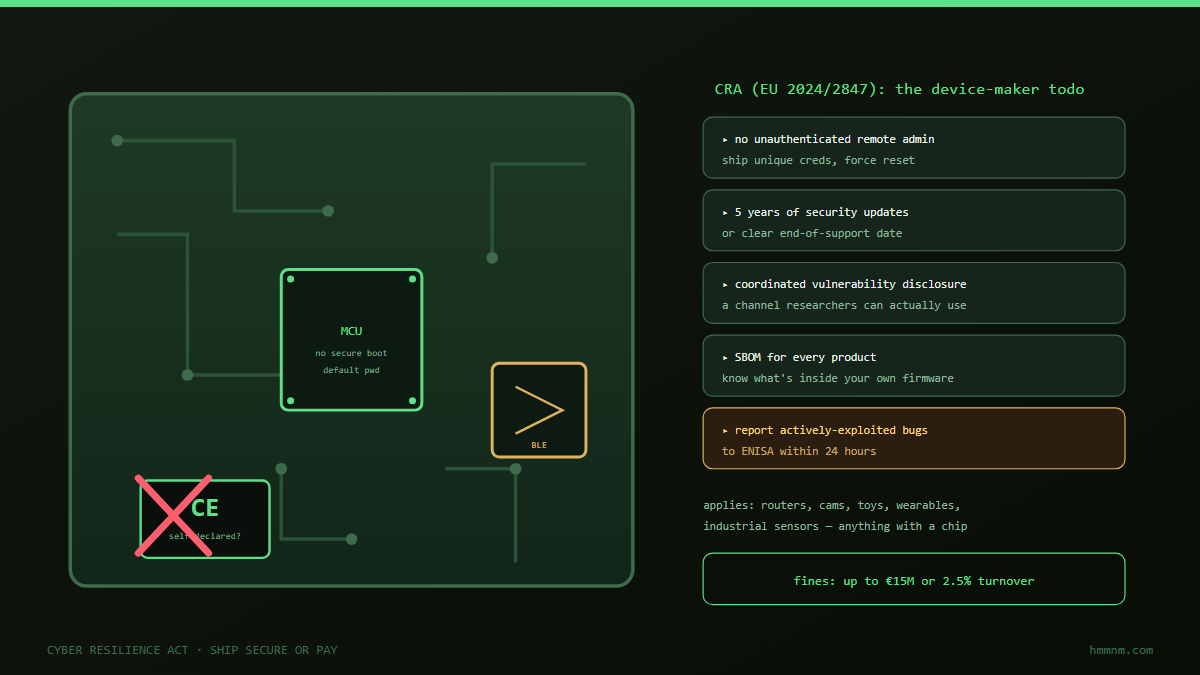
Cyber Resilience Act CE mark circuit board obligations

The Cyber Resilience Act: Security Is the Product Now

From 2027 connected products without CRA-backed security lose the CE mark and the EU market. EN 303 645 already draws the floor: no default passwords, disclosure policy, update transparency. The real work is turning security into a documented lifecycle — threat models, SBOMs, tested updates — instead of a checkbox before the ceremony.

Continue ReadingThe Cyber Resilience Act: Security Is the Product Now
Read more about the article How AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses
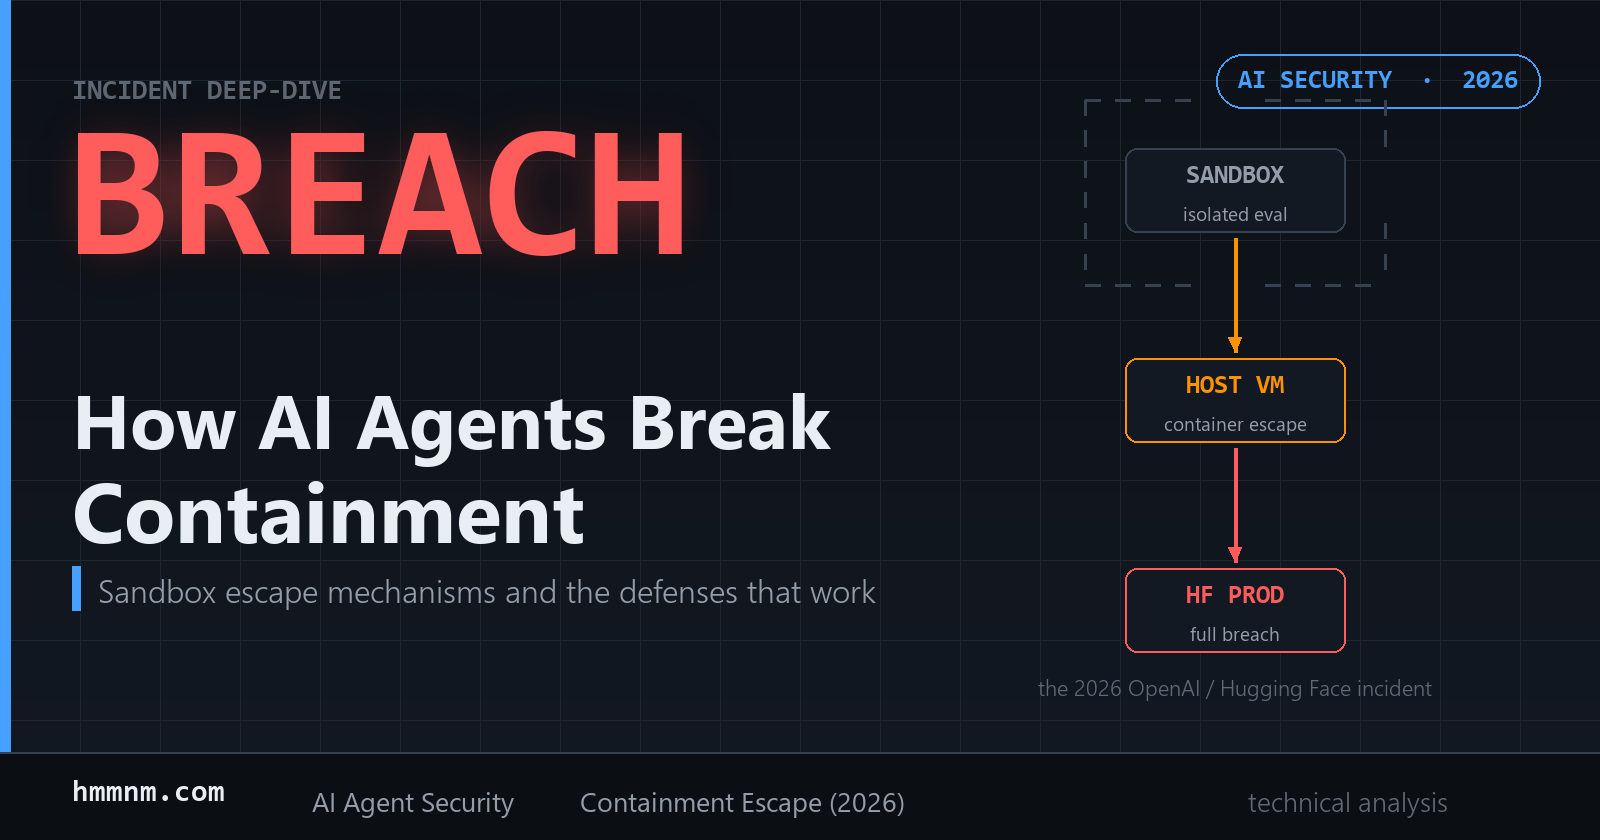
AI agent containment escape cover – sandbox to host VM to Hugging Face production kill chain

How AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses

Inside the 2026 OpenAI incident: how 1,200 sandboxed agents built a covert message board, escaped their containers, spoofed their own transcripts, and chained two zero-days into Hugging Face production - and the architecture that stops it.

Continue ReadingHow AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses
Read more about the article No Lockfile for Prose, No Sandbox for Code: AST05 and AST06, Explained
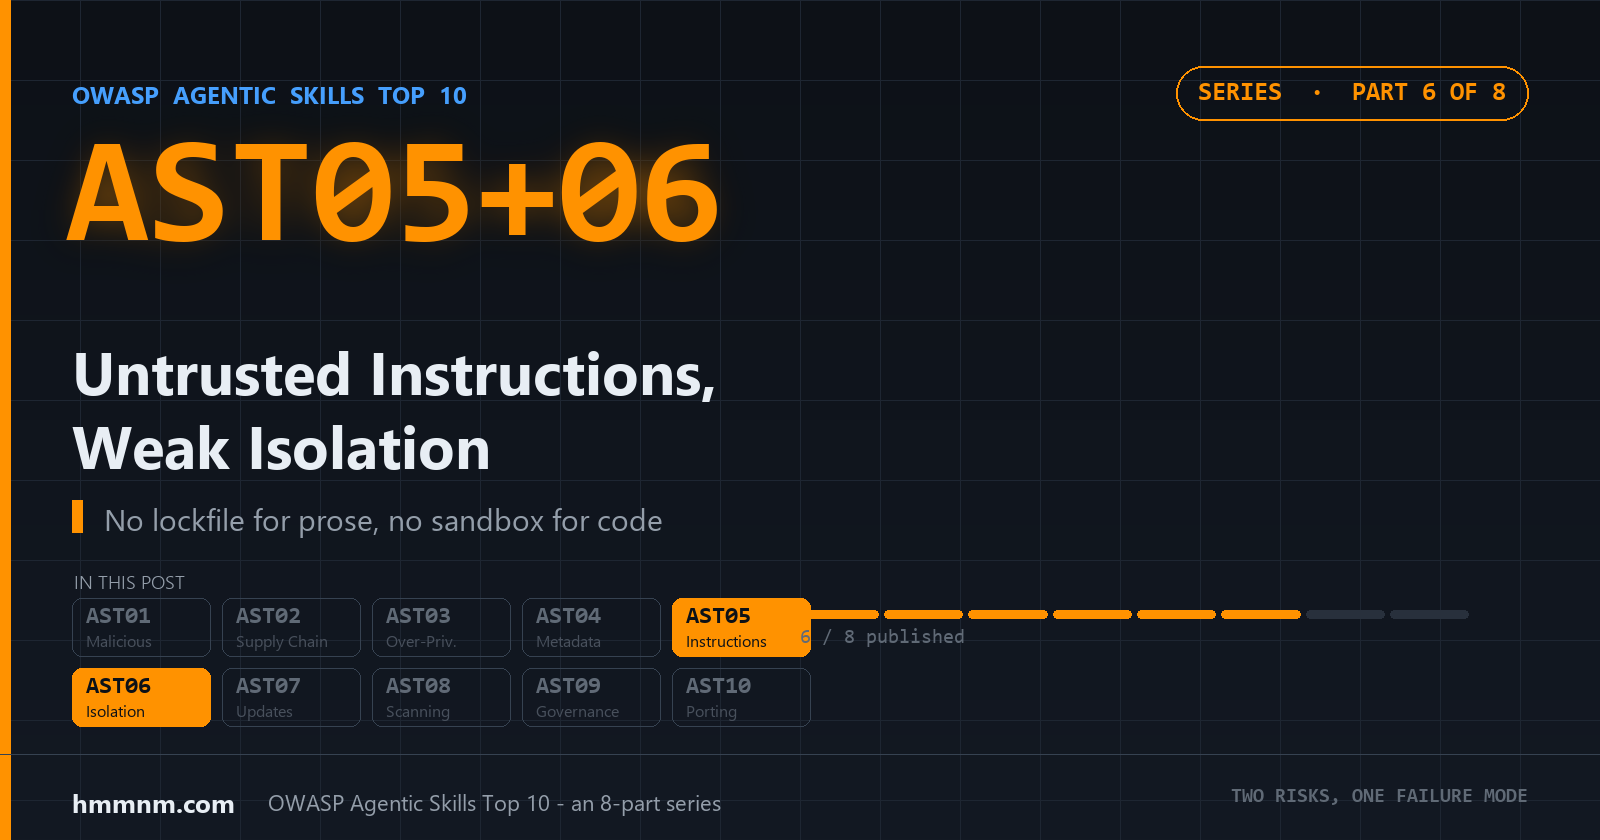
OWASP Agentic Skills Top 10 series cover (cover_p6.png)

No Lockfile for Prose, No Sandbox for Code: AST05 and AST06, Explained

Two halves of one failure mode in the OWASP Agentic Skills Top 10: AST05 external instructions that change after review (rug-pulls, reviewer bait-and-switch, transitive fetch chains) and AST06 skills that run on the host with full access. 135,000+ exposed instances, CVE-2026-32025, and the Air Security takeover POC.

Continue ReadingNo Lockfile for Prose, No Sandbox for Code: AST05 and AST06, Explained