eBPF Explained: Verified Programs Inside the Kernel
How eBPF runs verified, JIT-compiled programs safely in the Linux kernel — and why networking and security tools bet their stacks on it.

How eBPF runs verified, JIT-compiled programs safely in the Linux kernel — and why networking and security tools bet their stacks on it.
How SSRF turns one forged request into cloud-wide credential theft — the Capital One chain, IMDSv2, and the controls that actually block it.
Decode live aircraft ACARS and VDL2 datalink traffic with about $30 of SDR hardware, acarsdec, dumpvdls2 and Wireshark — a complete hands-on radio lab.
Agentic-AI abuse, the fall 2026 Edge CVE wave and infostealer tradecraft — this week’s defensive priorities in one briefing.
How Certificate Transparency Merkle logs, SCTs and monitors make every TLS certificate publicly auditable — and how they caught Symantec in 2015.
Stealer-log markets, edge-device exploitation and agentic-AI abuse: what defenders must patch, monitor and drill this week.
How Sigma turns SIEM detections into portable YAML, how pySigma pipelines compile them to any backend, and how to test rules like code with Atomic Red Team.
A hands-on recon-to-exploit walkthrough: fuzz hidden endpoints and parameters with ffuf and Caido, chain the findings, and document the impact.
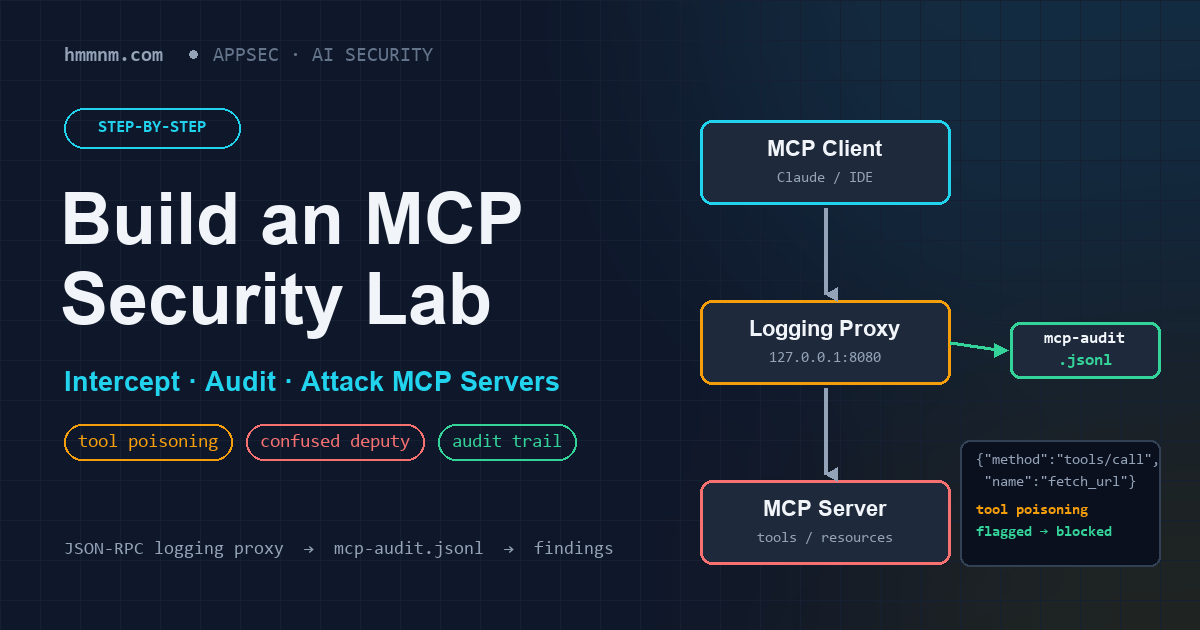
Build a local MCP security lab: intercept, audit and attack Model Context Protocol servers with proxies, rogue tools and logging you fully control.
Agentic-AI abuse, the September 2026 CVE wave and ransomware tradecraft — this week’s defensive checklist.
How NTP and PTP keep infrastructure clocks honest, why leap seconds took down Cloudflare and Reddit, and how to run time sync you can trust.
The Kubernetes security layers that stop real cluster compromises: control plane, RBAC, Pod Security Admission, network policy and image supply chain — with a ten-point audit checklist.
New threat analyses, tool guides and hardening playbooks — delivered straight to your inbox, the moment they go live.