Securing AI Agents in the Enterprise SOC
How AI agents transform enterprise SOC operations — autonomous triage, incident response, threat hunting, and compliance automation.

How AI agents transform enterprise SOC operations — autonomous triage, incident response, threat hunting, and compliance automation.
A deep dive into securing AI agent supply chains — MCP server vetting, dependency integrity, sandboxing, and trust anchors for AI infrastructure.
Master the three-layer model for AI agent identity: cryptographic identity, capability permissions, and runtime least privilege for autonomous AI systems.
Zero Trust for AI systems requires rethinking identity, data flows, and access control. Learn the five pillars of AI Zero Trust — identity verification, input validation, least privilege, monitoring, and encryption — with practical architecture patterns and implementation roadmap.
Post-quantum cryptography is no longer a research-only topic. With NIST's first PQC standards finalized and organizations facing long-term risks such as harvest-now, decrypt-later, cyber teams need to understand how PQC affects PKI, TLS, code signing, firmware trust, crypto agility, and migration planning. This guide explains what PQC is, where QKD fits, how hybrid deployments work, and what defenders should prioritize first.
A practical guide to software supply chain security covering dependency risks, secrets exposure, CI/CD trust failures, artifact integrity verification, SBOM management, and real-world attack case studies.
A comprehensive guide to SSH to VPS security pentesting covering practical attack scenarios, validation commands, real-world case studies, and hardening steps for Linux infrastructure.
CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.
100 essential networking topics to revise before your technical interview. Covers OSI model, TCP/IP fundamentals, routing protocols, switching concepts, security basics, and troubleshooting methodologies.
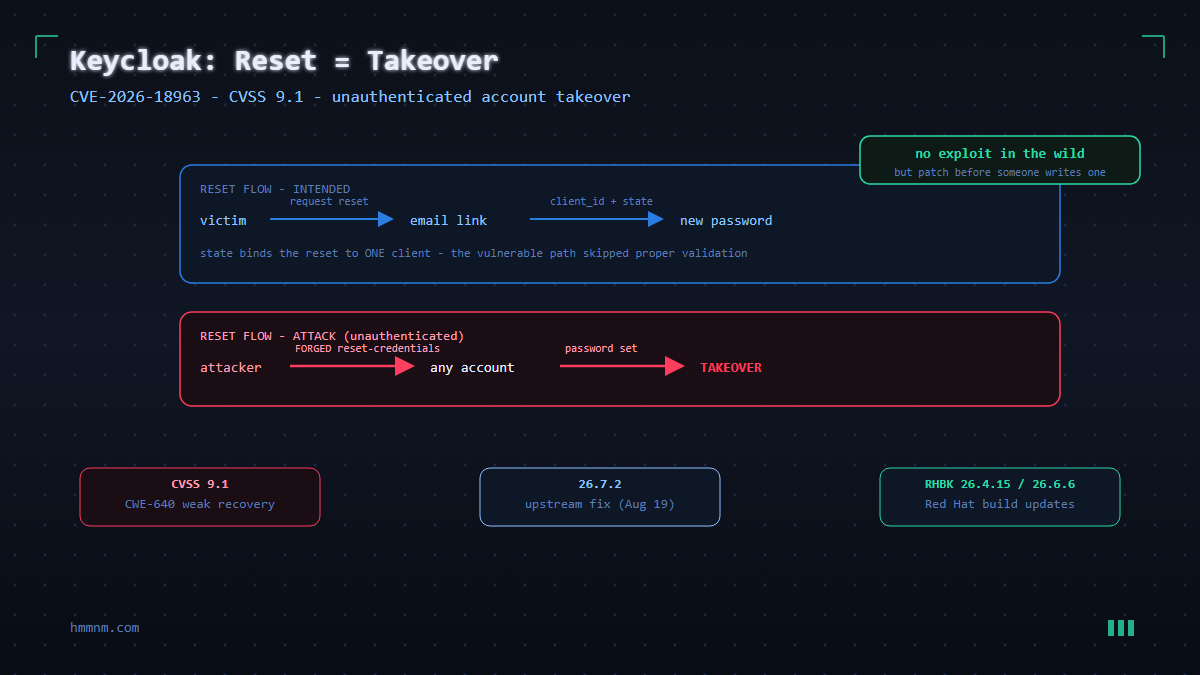
Keycloak’s reset-credentials flow skips its own email action token: an unauthenticated attacker can set a new password on any account, including admins. CVSS 9.1, fixed in 26.7.2 – patch guide, detection hunting, and the temporary mitigation inside.
GitLab CVE-2026-19478 went from disclosure to in-the-wild exploitation in days; a compromised maintainer account backdoored three Rust crates with 245M downloads for 86 minutes; Citrix shipped a CVSS 9.3 NetScaler auth bypass. The week's threats, IoCs, and your Monday patch list.
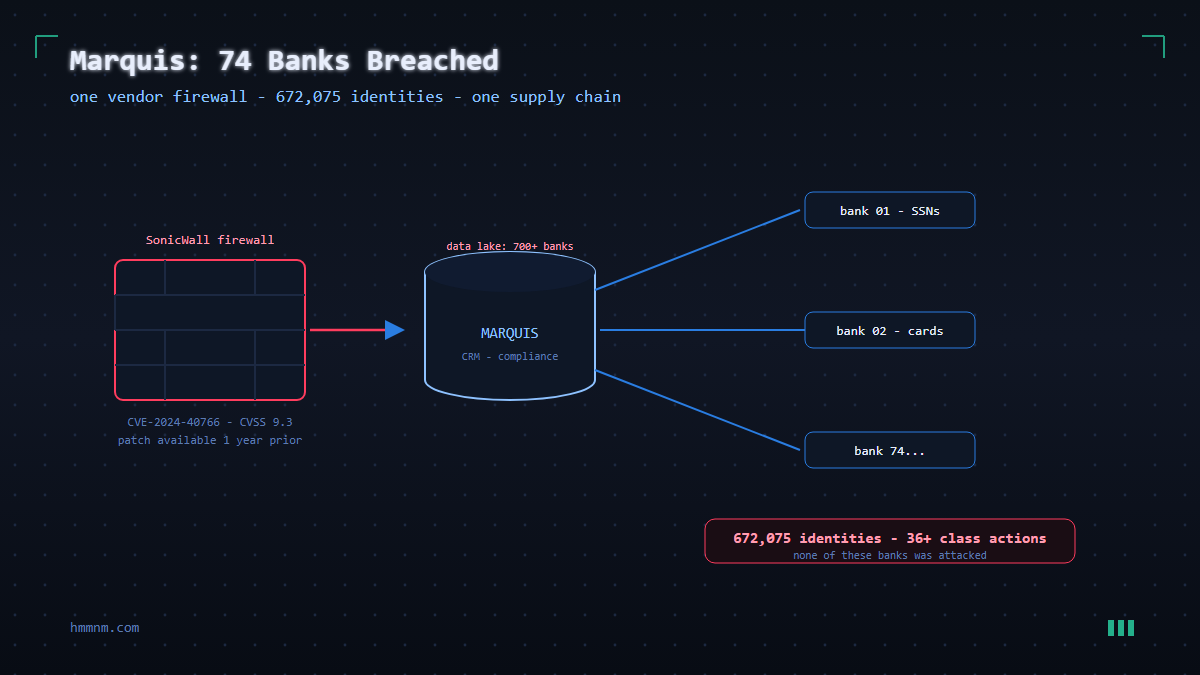
Attackers entered Texas fintech Marquis through a SonicWall firewall and reached data for 700+ client banks - 672,075 identities, 74 institutions disrupted. The supply-chain anatomy and five break-points.
New threat analyses, tool guides and hardening playbooks — delivered straight to your inbox, the moment they go live.