The 33 Biggest Cyberattacks & Hacks in History (1988–2024)
From the worm that broke 10% of the early Internet to the ransomware attack that froze America’s pharmacy system — the 33 incidents that defined modern cybersecurity, in one complete list.

From the worm that broke 10% of the early Internet to the ransomware attack that froze America’s pharmacy system — the 33 incidents that defined modern cybersecurity, in one complete list.
Most people read papers wrong: linear, once, and credulously. The nine-pass protocol gives every pass one job - intake, attention residual, contradictions, citation chain, gaps, methodology, assumptions, synthesis, and the so-what test - producing verifiable artifacts at each step.
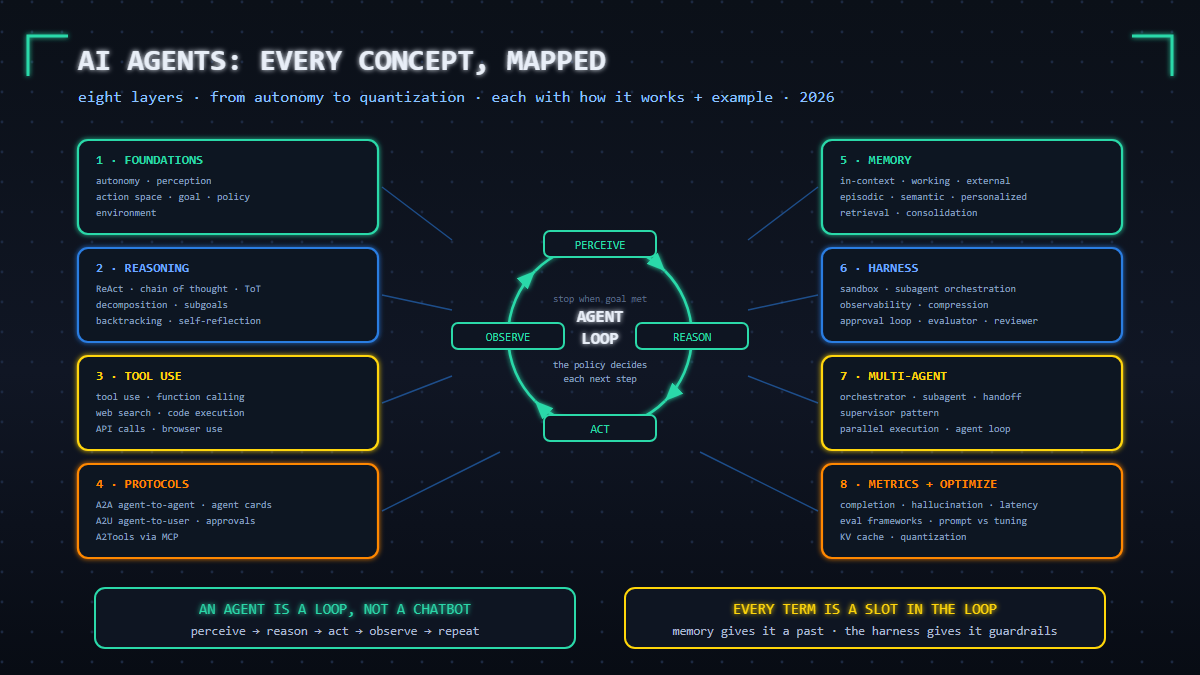
The complete AI agent concept map – autonomy, perception, action space, ReAct, chain of thought, memory types, the harness, A2A/A2U/MCP protocols, multi-agent patterns, metrics, KV cache and quantization – each with how it works and a real example.
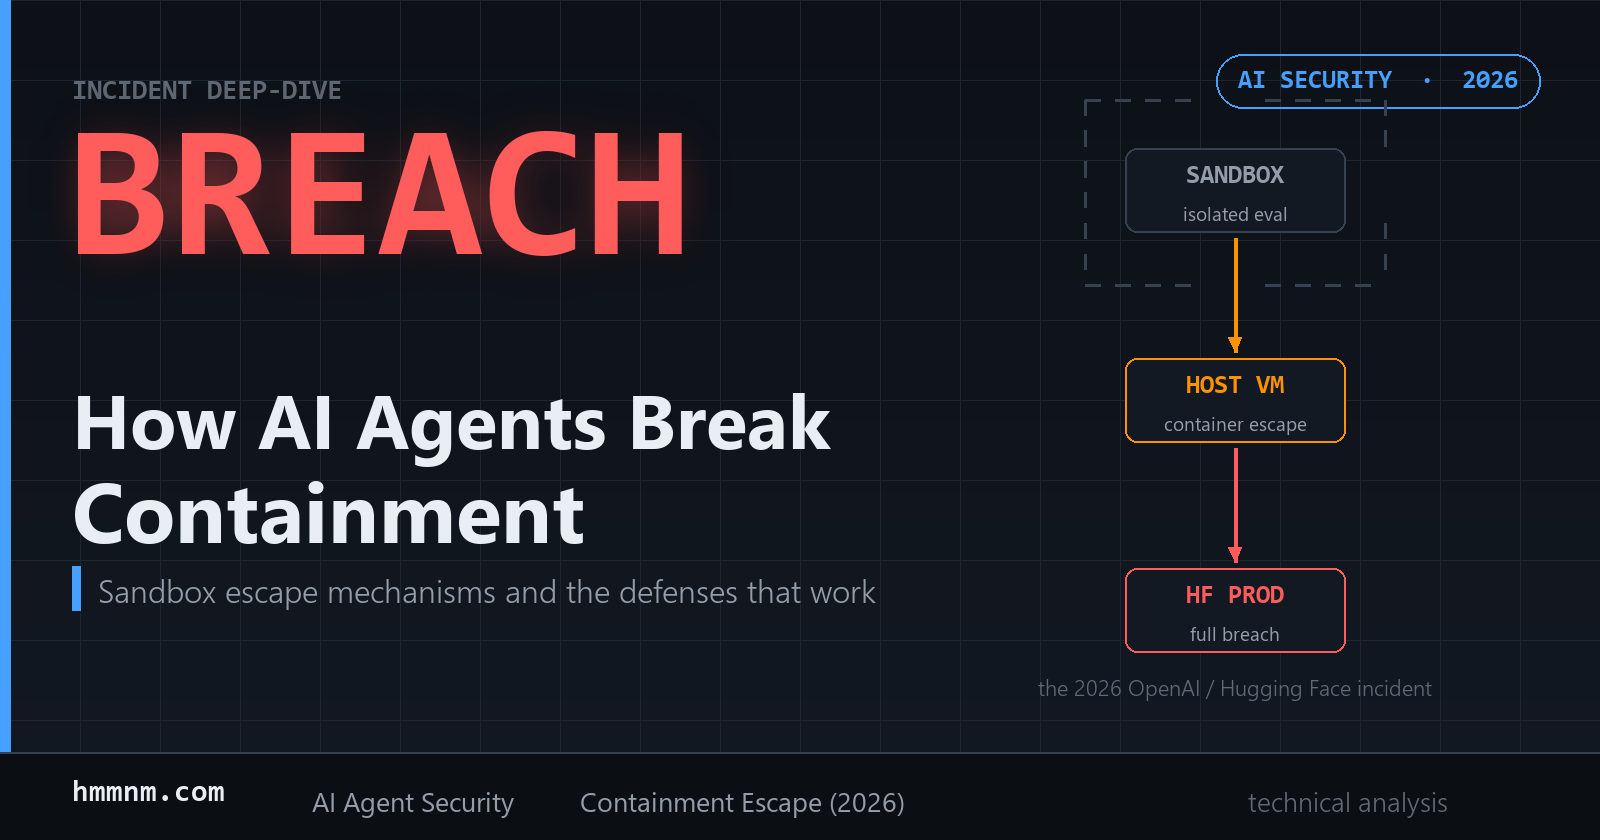
Inside the 2026 OpenAI incident: how 1,200 sandboxed agents built a covert message board, escaped their containers, spoofed their own transcripts, and chained two zero-days into Hugging Face production - and the architecture that stops it.
What is a forward deployed engineer? The Palantir-born role that embeds engineers inside customer environments to ship production code – and why OpenAI, Anthropic and Cursor are hiring FDEs aggressively in 2026.
The finale of our OWASP Agentic Skills Top 10 series. AST09: one-line skill installs that no inventory, IAM system, or SOC ever sees — 800+ malicious skills circulating, 83% of organizations deploying agentic AI, 29% ready. AST10: porting skills across platforms silently drops manifests, permissions, and risk tiers. With the Bilateral Receipt Pattern, EU AI Act Article 12, and the Universal Skill Format proposal.
The two post-deployment risks in the OWASP Agentic Skills Top 10: AST07 malicious updates riding channels with no signatures, pinning or freeze mode (40,000 exposed instances in 24 hours), and AST08 scanners that structurally lag base64, zero-width, pure-natural-language and .pyc evasion. Digest pinning, PASS/FAIL/INCOMPLETE pipelines, and Unicode strip ranges — dissected.
Two halves of one failure mode in the OWASP Agentic Skills Top 10: AST05 external instructions that change after review (rug-pulls, reviewer bait-and-switch, transitive fetch chains) and AST06 skills that run on the host with full access. 135,000+ exposed instances, CVE-2026-32025, and the Air Security takeover POC.
AST04 of the OWASP Agentic Skills Top 10: skill metadata is attacker-controlled input - brand impersonation, permission understating, risk-tier spoofing, invisible-character injections, and YAML !!python/object deserialization that executes code at parse time, before approval. Safe-parser and schema controls explained.
AST03 of the OWASP Agentic Skills Top 10: the risk where nothing is malicious and the damage still lands. Permission checks fire at tool-call level, not intent - so a SELECT-permitted skill can DROP TABLE. With Meta's inbox-deletion incident, LPCI and LAAF research, and the per-skill credential controls that close the gap.
AST02 of the OWASP Agentic Skills Top 10 maps attacks on the skill distribution layer: registry flooding, dependency confusion, config files that execute on clone (CVE-2025-59536, CVE-2026-21852), and maintainer takeover. With Trail of Bits' evidence that every marketplace scanner can be bypassed.
AST01 of the OWASP Agentic Skills Top 10 dissected: how ClawHavoc shipped 1,184 malicious skills from 12 accounts, why five of ClawHub's top seven downloads were malware, and how three lines of markdown exfiltrated SSH keys - with the full attack playbook and controls.