JWT Security: alg=none, Key Confusion and Why the Header Lies
The JWT vulnerability class explained: alg=none, RS256/HS256 key confusion, jwk and kid injection — and the RFC 8725 defenses.

The JWT vulnerability class explained: alg=none, RS256/HS256 key confusion, jwk and kid injection — and the RFC 8725 defenses.
How SSRF turns one forged request into cloud-wide credential theft — the Capital One chain, IMDSv2, and the controls that actually block it.
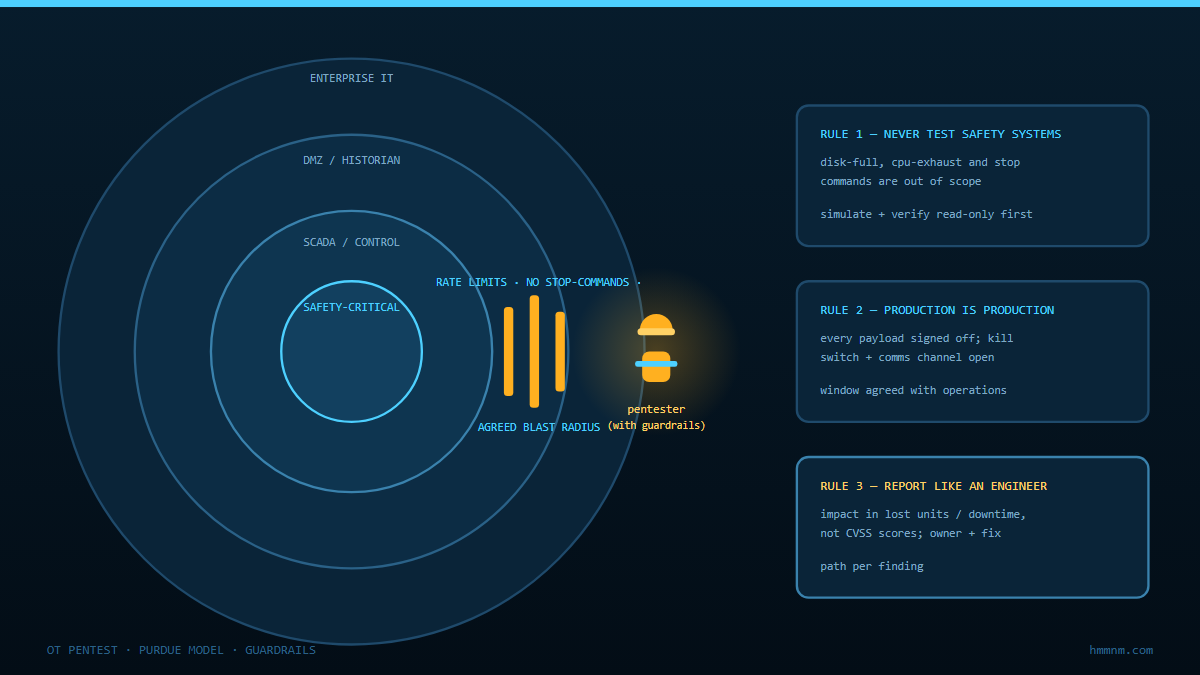
Oldsmar proved an intruder can move a plant setpoint from a browser tab. This is the safe method: passive-first discovery, read-only active testing, writes proven on clone benches, and findings ranked in downtime currency — not CVSS.
In-depth guide to HTTP request smuggling attacks. Learn how to exploit discrepancies between frontend proxies and backend servers in both HTTP/1.1 and HTTP/2 environments with practical examples.
Comprehensive guide to securing login and registration systems. Covers authentication vulnerabilities, brute-force protection, session management, CAPTCHA implementation, and security best practices.
December 2023 brought one of email’s most elegant attacks: SMTP smuggling, a parser-level desync that tricks receiving servers into writing attacker-authored messages that pass SPF and DMARC because the victim’s own infrastructure vouches for them. This deep dive covers the technique mechanics (end-of-data ambiguity, the second hidden MAIL FROM conversation), the December 19 disclosure and DHL demonstration, the two anchoring CVEs, which product families patched, and the durable lessons for mail admins running anything that speaks SMTP.
CVE-2023-46747 let unauthenticated attackers smuggle requests through BIG-IP TMM into the iControl REST management plane — a framing bug that became full device compromise. Exploitation followed the October patch within days, and CISA put it on the KEV catalog before month end.
Learn error-based exploitation techniques used by pentesters to extract sensitive data from vulnerable applications. Covers SQL injection, SSTI, and other injection-based attacks with practical examples and mitigation strategies.
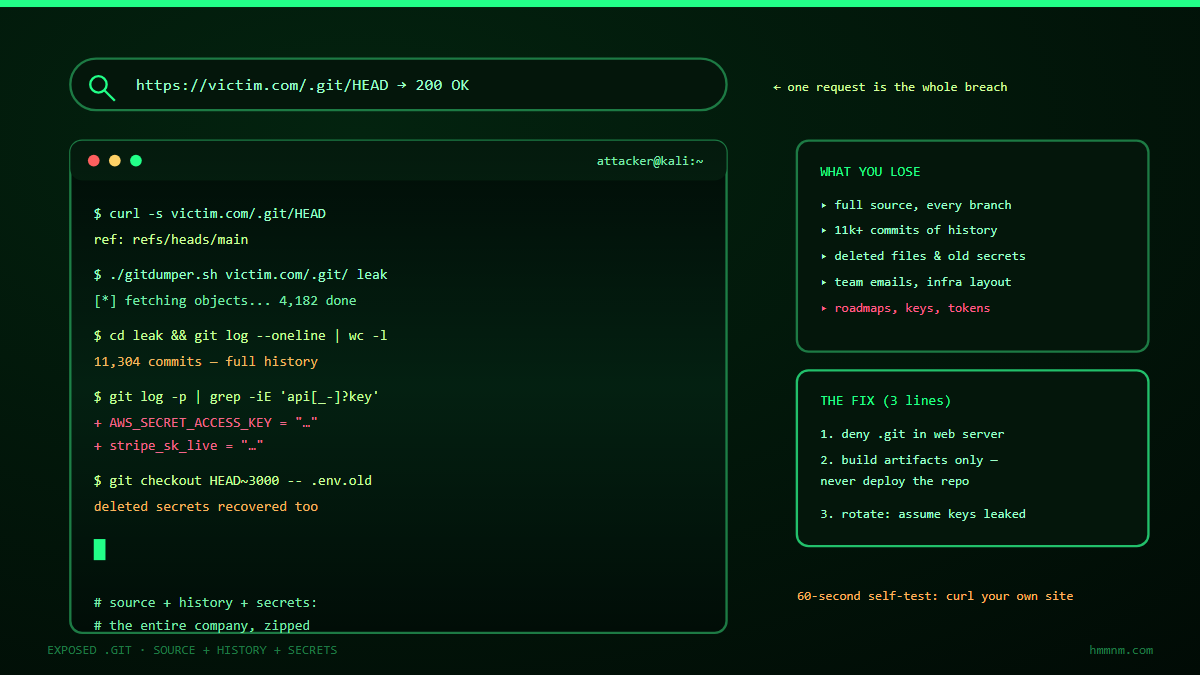
One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.
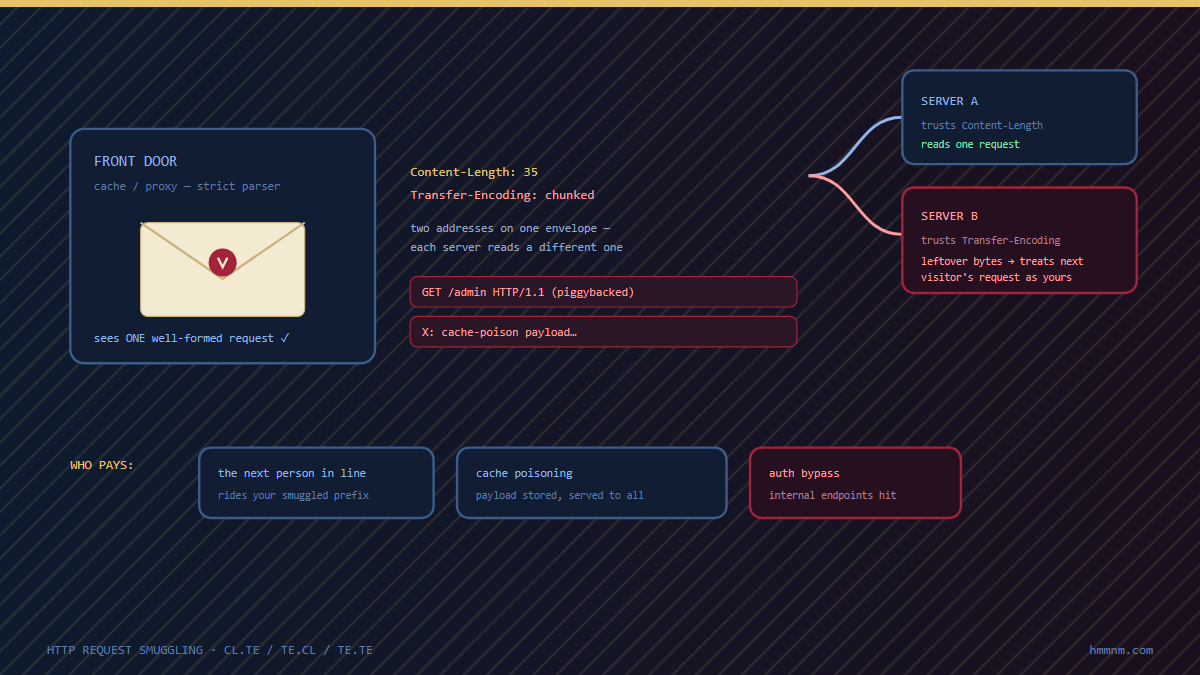
Your front end and your back end disagree about where one request ends and the next begins. The smuggled prefix slides under the WAF, defeats the rate limiter, and poisons the cache under someone else else URL. How CL-TE and TE-CL desyncs work, and the configuration discipline that closes them.
A comprehensive guide to SSH to VPS security pentesting covering practical attack scenarios, validation commands, real-world case studies, and hardening steps for Linux infrastructure.
CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.