Read more about the article The Exposed .git Mistake We Keep Finding After 10 Years
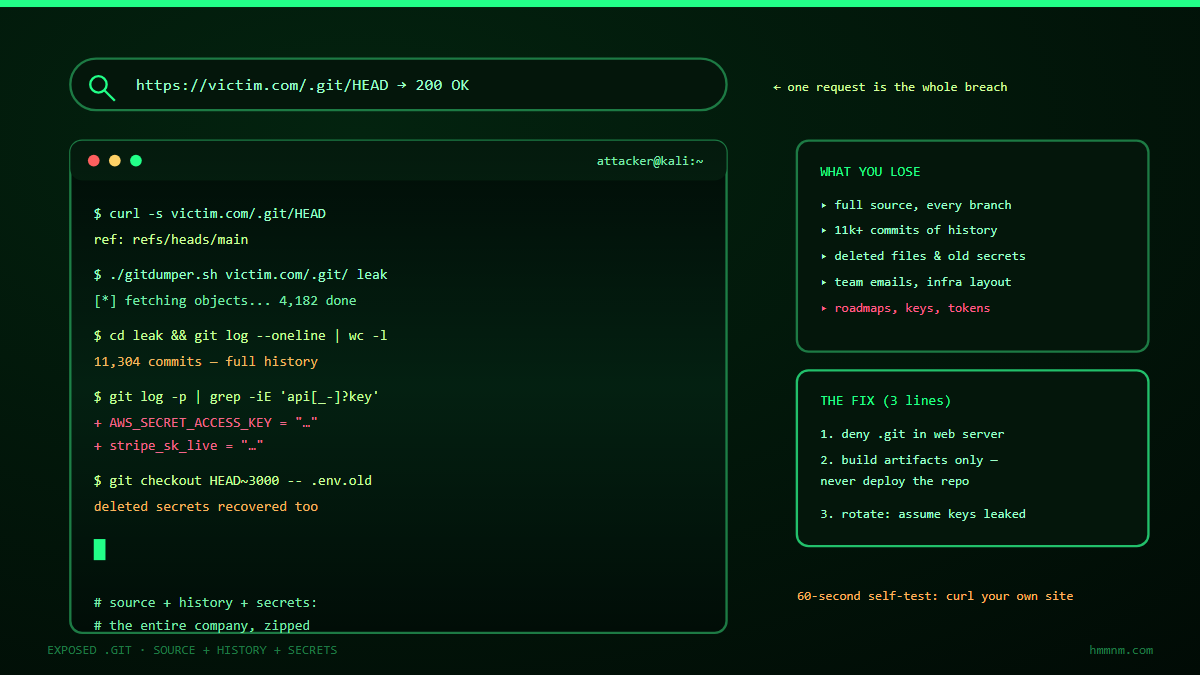
Exposed git directory terminal session

The Exposed .git Mistake We Keep Finding After 10 Years

One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.

Continue ReadingThe Exposed .git Mistake We Keep Finding After 10 Years
Read more about the article HTTP Request Smuggling: One Request, Two Interpretations
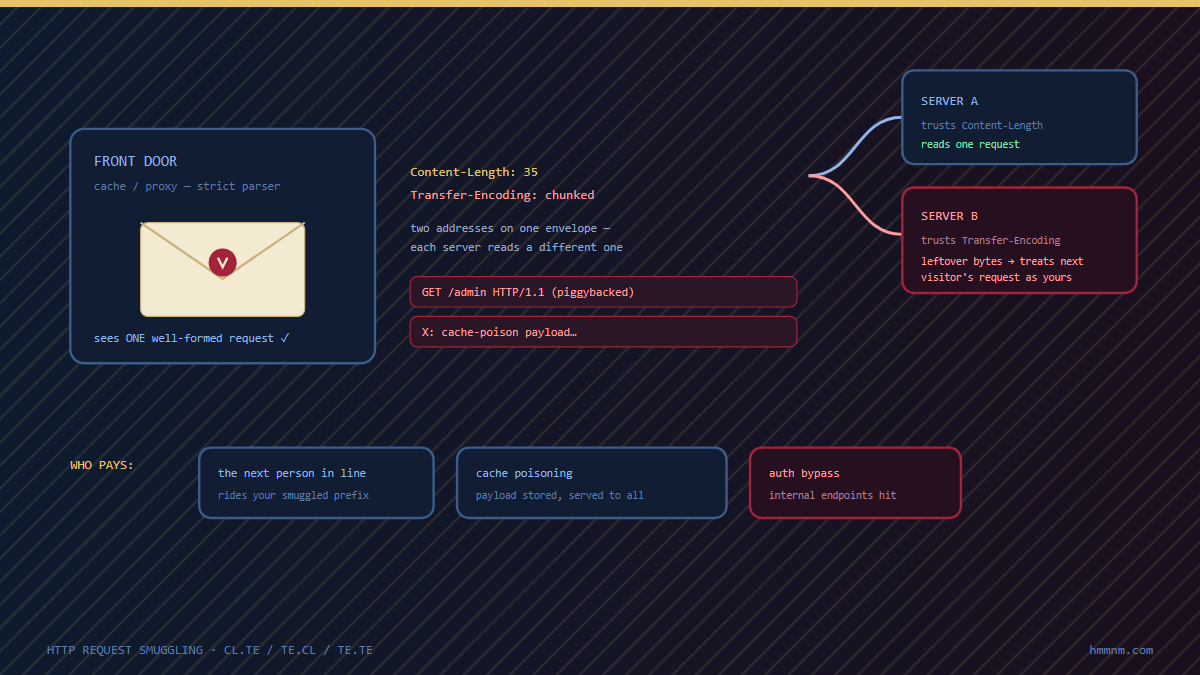
HTTP request smuggling elegant envelope desync

HTTP Request Smuggling: One Request, Two Interpretations

Your front end and your back end disagree about where one request ends and the next begins. The smuggled prefix slides under the WAF, defeats the rate limiter, and poisons the cache under someone else else URL. How CL-TE and TE-CL desyncs work, and the configuration discipline that closes them.

Continue ReadingHTTP Request Smuggling: One Request, Two Interpretations
Read more about the article CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them
CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS Misconfigurations in Modern Web Apps: How to Find and Fix Them

CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.

Continue ReadingCORS Misconfigurations in Modern Web Apps: How to Find and Fix Them