
F5 BIG-IP Request Smuggling 2023: The 9.8 Desync

CVE-2023-46747 let unauthenticated attackers smuggle requests through BIG-IP TMM into the iControl REST management plane — a framing bug that became full device compromise. Exploitation followed the October patch within days, and CISA put it on the KEV catalog before month end.
Continue ReadingF5 BIG-IP Request Smuggling 2023: The 9.8 Desync
Read more about the article HTTP Request Smuggling: One Request, Two Interpretations
HTTP request smuggling elegant envelope desync

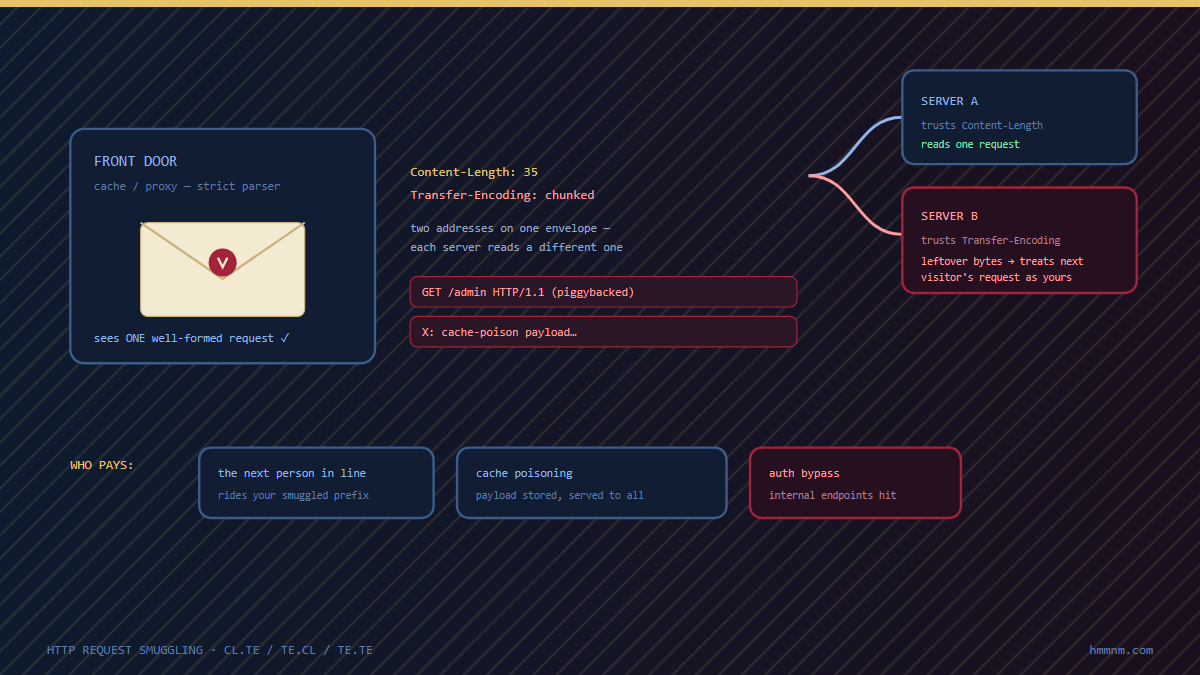
HTTP Request Smuggling: One Request, Two Interpretations

Your front end and your back end disagree about where one request ends and the next begins. The smuggled prefix slides under the WAF, defeats the rate limiter, and poisons the cache under someone else else URL. How CL-TE and TE-CL desyncs work, and the configuration discipline that closes them.

Continue ReadingHTTP Request Smuggling: One Request, Two Interpretations