ESXiArgs: The Ransomware Wave That EncryptEd Whole Estates
ESXiArgs hit thousands of unpatched VMware ESXi hosts via old OpenSLP bugs in February 2023. Hypervisor ransomware and recovery-script lessons.

ESXiArgs hit thousands of unpatched VMware ESXi hosts via old OpenSLP bugs in February 2023. Hypervisor ransomware and recovery-script lessons.
A single compromised API credential let an actor scrape ~37 million T-Mobile accounts over six weeks. Machine-identity governance lessons from a repeat offender.
CVE-2023-4966 let attackers read valid session tokens out of NetScaler memory and inherit authenticated sessions wholesale — MFA already passed. CISA’s Emergency Directive 23-08 forced hunts and rebuilds as LockBit monetized the access.
In September 2023 two extortion crews — Rhysida and the short-lived Ransomed.vc — both posted Sony data claims, complete with a Bitcoin auction and a leaked code-signing certificate. Sony investigated; the claimed 6TB scale never verified.
Ransomware forced the Guardian’s newsroom off its networks for weeks in late 2022 — yet print and web kept publishing. Editorial continuity lessons.
A cloned intranet page harvested an employee’s password and MFA code, opening hours of internal access. Phishing-resistant MFA and self-report lessons.
LockBit encrypted Royal Mail’s international sorting operations in January 2023 and demanded $80M. Royal Mail paid nothing and kept the letters moving.
Rackspace’s December 2022 ransomware incident took Hosted Exchange down for weeks, ended the product’s life, and cost $12M+. Legacy platform lessons.
Operation Cookie Monster seized the market selling browser sessions, cookies, and saved credentials for ~2M identities, with 119 arrests across 17+ countries. Session-security lessons.
LastPass confirmed attackers copied encrypted vault backups after pivoting through a DevOps engineer’s endpoint. KDF legacy and unencrypted metadata set the real risk.
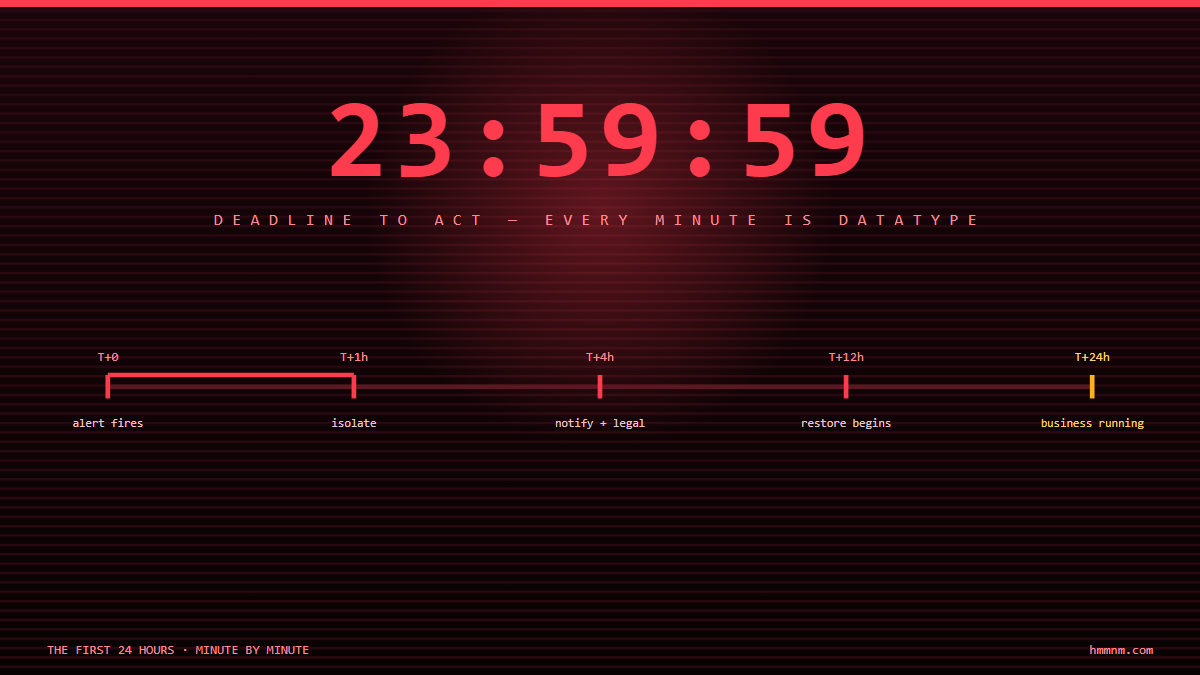
Change Healthcare lost the claims pipeline of a nation in hours. This minute-by-minute playbook covers hour zero containment, the command structure by hour four, backup verification, pay/no-pay, regulatory clocks — and the non-technical decisions that decide survival.
A defunct test tenant, a legacy password without MFA, and a residential-proxy password spray gave Russia’s Midnight Blizzard a foothold inside Microsoft’s own corporate estate in January 2024 — culminating in stolen executive email and a downstream supplier breach wave. This account explains the password-spray tradecraft, how the actors abused OAuth apps to mine mailboxes, why the failure drew a czar-memo mea culpa, and the SEC disclosure mechanics that made the saga public.