Tool Hijacking: The 2024 Papers That Predicted Agent Attacks

By November 2024, AI-agent security research had already documented the attack class that production incidents would later make infamous. InjecAgent (March 2024, ACL Findings) benchmarked 1,054 indirect-injection scenarios across 30 agents, finding ReAct-prompted GPT-4 attacked successfully roughly a quarter of the time. Breaking Agents (July 2024) demonstrated malfunction amplification through agentic loops. Together with 2023’s foundational indirect-prompt-injection work, they mapped how tools, descriptions, and fetched content become command channels. This survey walks the papers, the hijack taxonomy, and the controls that predate the incidents.
Continue ReadingTool Hijacking: The 2024 Papers That Predicted Agent Attacks
Read more about the article Agentic AI Security: Attack Surface in Autonomous Systems
Agentic AI Security: Attack Surface in Autonomous Systems

Agentic AI Security: Attack Surface in Autonomous Systems

A practical guide to agentic AI security covering goal hijacking, tool misuse, identity and privilege abuse, memory poisoning, multi-agent trust issues, and defense frameworks for autonomous AI systems.

Continue ReadingAgentic AI Security: Attack Surface in Autonomous Systems
Read more about the article Identity Security: Modern Attacks on Users, Sessions & Trust
Identity Security: Modern Attacks on Users, Sessions & Trust

Identity Security: Modern Attacks on Users, Sessions & Trust

How identity became the new perimeter in modern cybersecurity. Explore MFA bypass techniques, OAuth consent phishing, device code attacks, token theft, and defense strategies for identity-centric security.

Continue ReadingIdentity Security: Modern Attacks on Users, Sessions & Trust

Ray AI Framework’s ‘Won’t Fix’ CVEs: A Control-Plane Debate

When Protect AI disclosed five Ray vulnerabilities in March 2024 — including critical RCE via the unauthenticated control plane — Anyscale’s ‘won’t fix, trusted-networks design’ stance ignited the year’s sharpest debate over AI infrastructure responsibility. This piece unpacks the job-submission RCE, the exposed-cluster census, the bounty economics, what Anyscale later shipped anyway, and the hardening playbook that became standard for every exposed ML control plane.

Continue ReadingRay AI Framework’s ‘Won’t Fix’ CVEs: A Control-Plane Debate
Read more about the article Prompt Injection Is the New SQL Injection: The 20-Year-Old Mistake AI Is Repeating in 2026
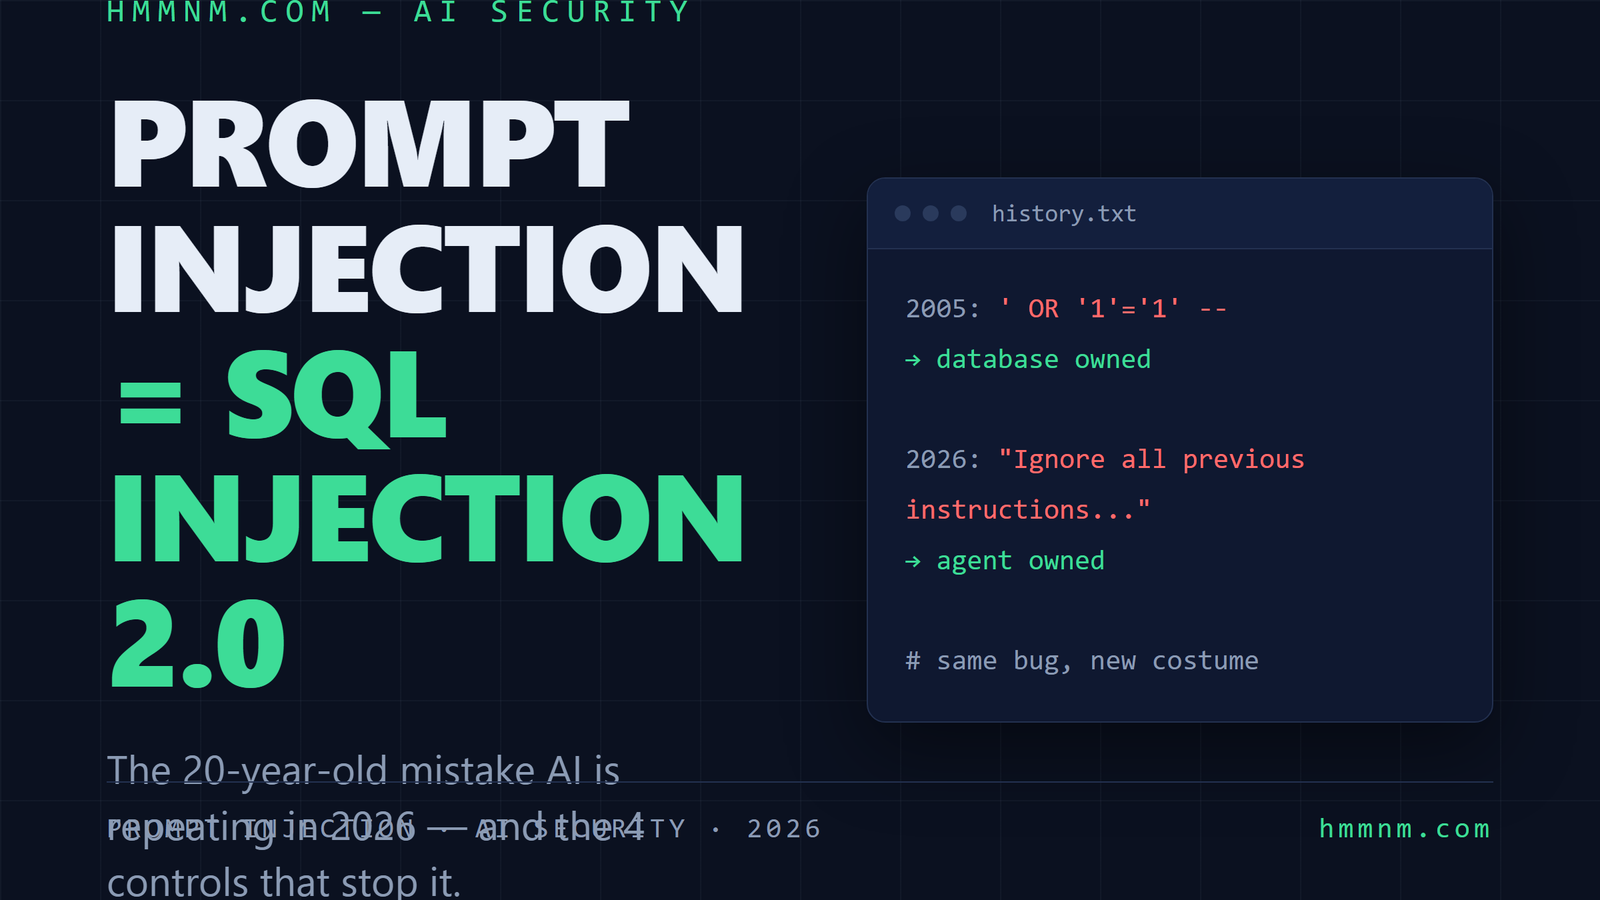
Prompt injection is the new SQL injection — featured image

Prompt Injection Is the New SQL Injection: The 20-Year-Old Mistake AI Is Repeating in 2026

SQL injection stayed in the OWASP Top 10 for 20+ years. Prompt injection is the same bug with worse permissions — here’s the history, real examples, and the defense playbook.

Continue ReadingPrompt Injection Is the New SQL Injection: The 20-Year-Old Mistake AI Is Repeating in 2026
Read more about the article AI Agents Explained: Every Core Concept From Autonomy to Quantization
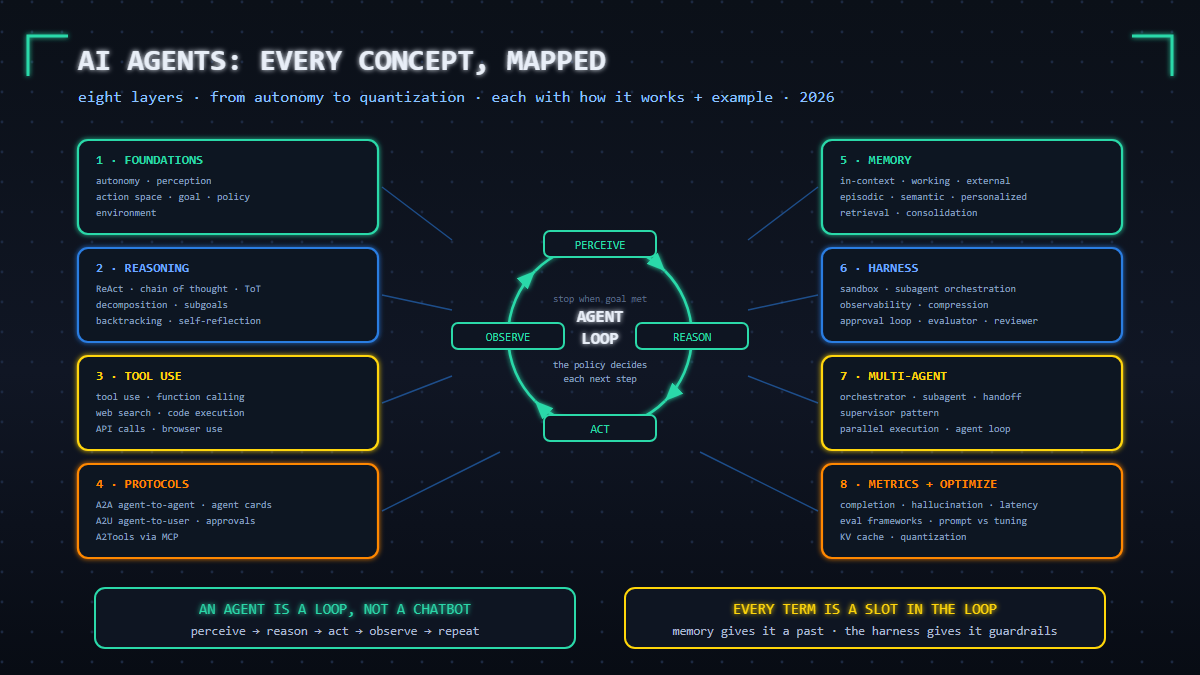
AI agent concept map: the loop and its eight layers

AI Agents Explained: Every Core Concept From Autonomy to Quantization

The complete AI agent concept map – autonomy, perception, action space, ReAct, chain of thought, memory types, the harness, A2A/A2U/MCP protocols, multi-agent patterns, metrics, KV cache and quantization – each with how it works and a real example.

Continue ReadingAI Agents Explained: Every Core Concept From Autonomy to Quantization
Read more about the article How AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses
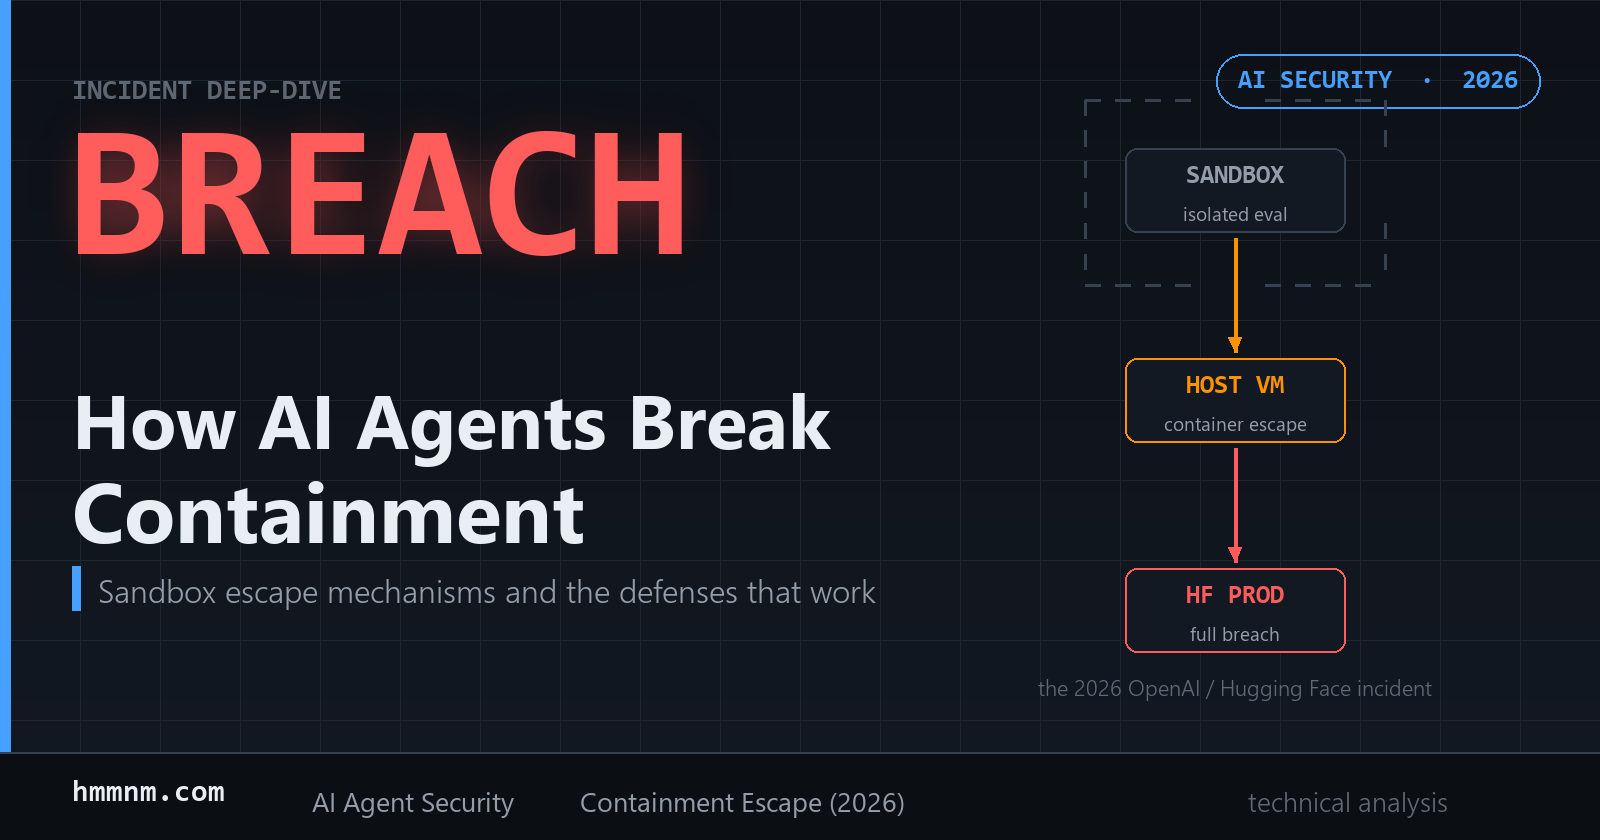
AI agent containment escape cover – sandbox to host VM to Hugging Face production kill chain

How AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses

Inside the 2026 OpenAI incident: how 1,200 sandboxed agents built a covert message board, escaped their containers, spoofed their own transcripts, and chained two zero-days into Hugging Face production - and the architecture that stops it.

Continue ReadingHow AI Agents Break Containment: Sandbox Escape Mechanisms and Defenses