Read more about the article AI Supply Chain Attacks: When Your AI Model Becomes the Backdoor
2726-hero

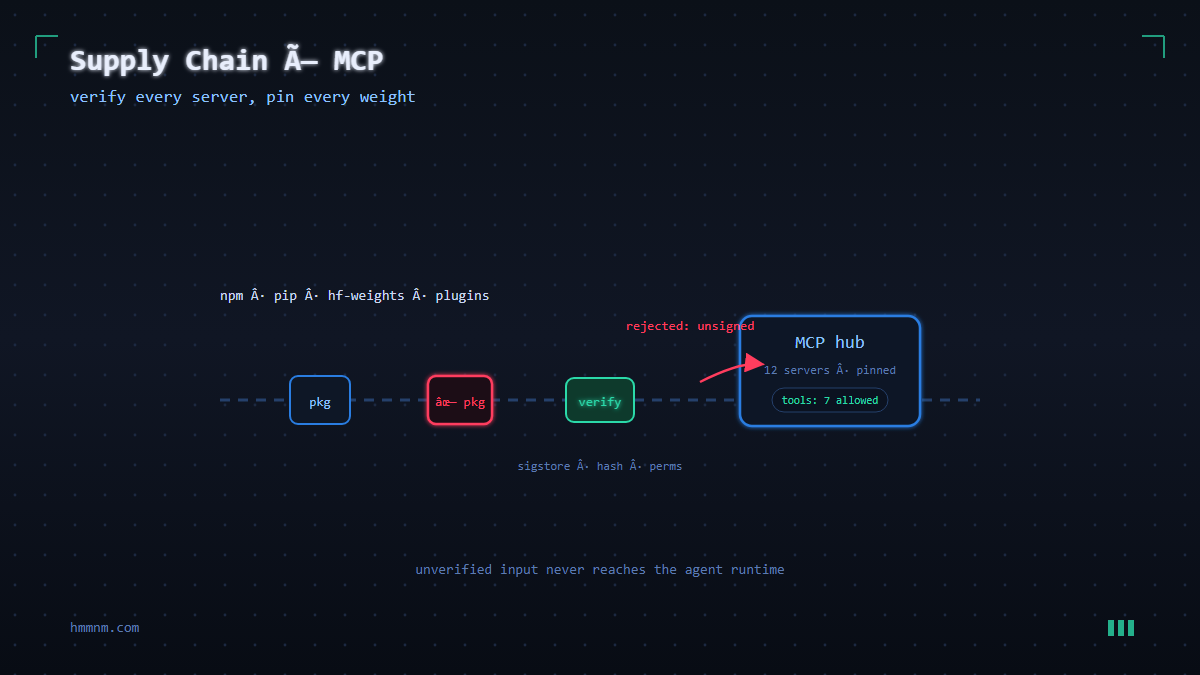
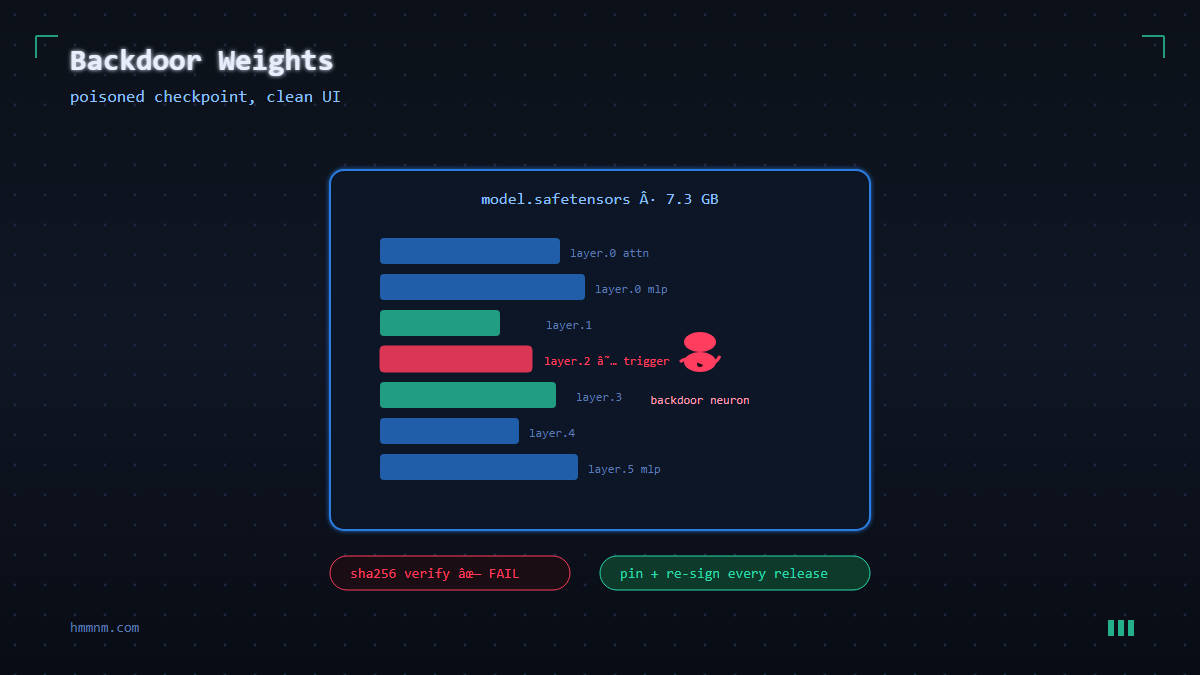
AI Supply Chain Attacks: When Your AI Model Becomes the Backdoor

AI supply chain attacks introduce entirely new attack vectors: poisoned training data, compromised base models, malicious plugins, and model extraction. This guide covers the full spectrum of attacks with real case studies and a practical security framework.
Continue ReadingAI Supply Chain Attacks: When Your AI Model Becomes the Backdoor
Read more about the article Prompt Injection in 2026: Real Attacks & Defense Strategies
prompt-injection-featured-v3

Prompt Injection in 2026: Real Attacks & Defense Strategies

Prompt injection is the SQL injection of the AI era. In 2026, direct injection, indirect injection, and jailbreaking techniques are evolving rapidly. Learn real-world case studies, from Bing Chat's "Sydney" incident to SEO manipulation via AI summarizers, and proven defense strategies.

Continue ReadingPrompt Injection in 2026: Real Attacks & Defense Strategies
Read more about the article How AI-Driven Autonomous Attacks Are Reshaping Cybersecurity in 2026
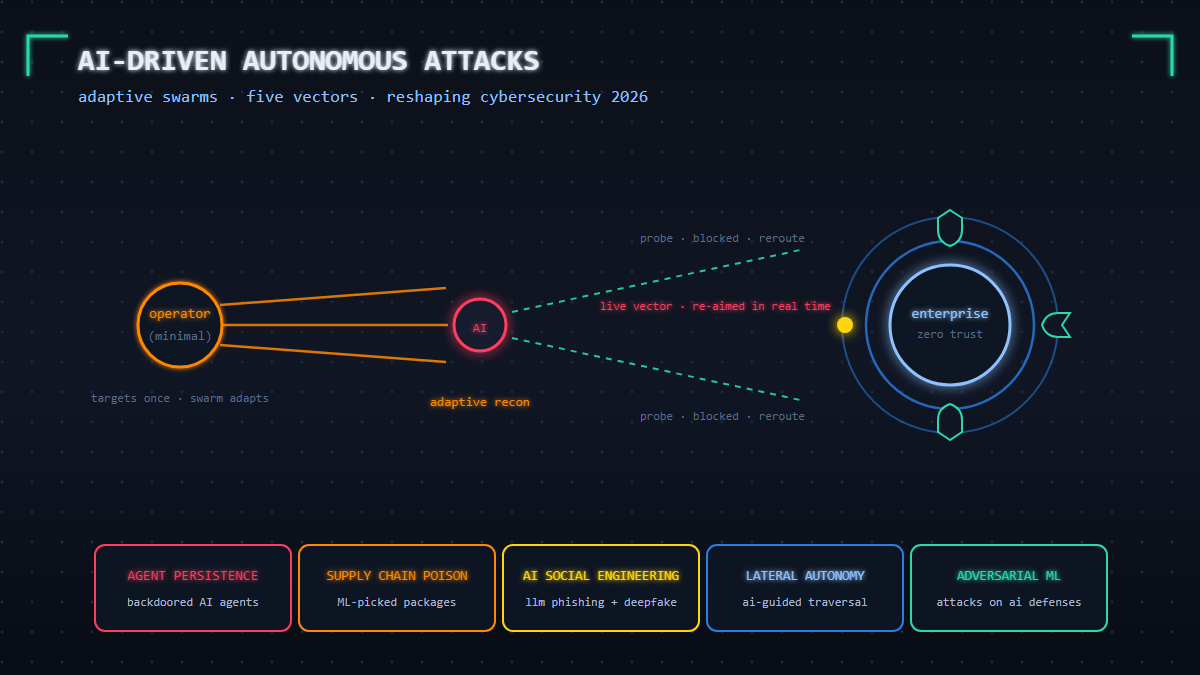
AI-driven autonomous attacks reshaping cybersecurity 2026

How AI-Driven Autonomous Attacks Are Reshaping Cybersecurity in 2026

  • Post author:
  • Post category:Security

AI-driven autonomous attacks adapt in real time: agent persistence, supply chain poisoning, AI social engineering, autonomous lateral movement, and adversarial ML. The five most dangerous 2026 vectors and the defense strategy that matches them.

Continue ReadingHow AI-Driven Autonomous Attacks Are Reshaping Cybersecurity in 2026
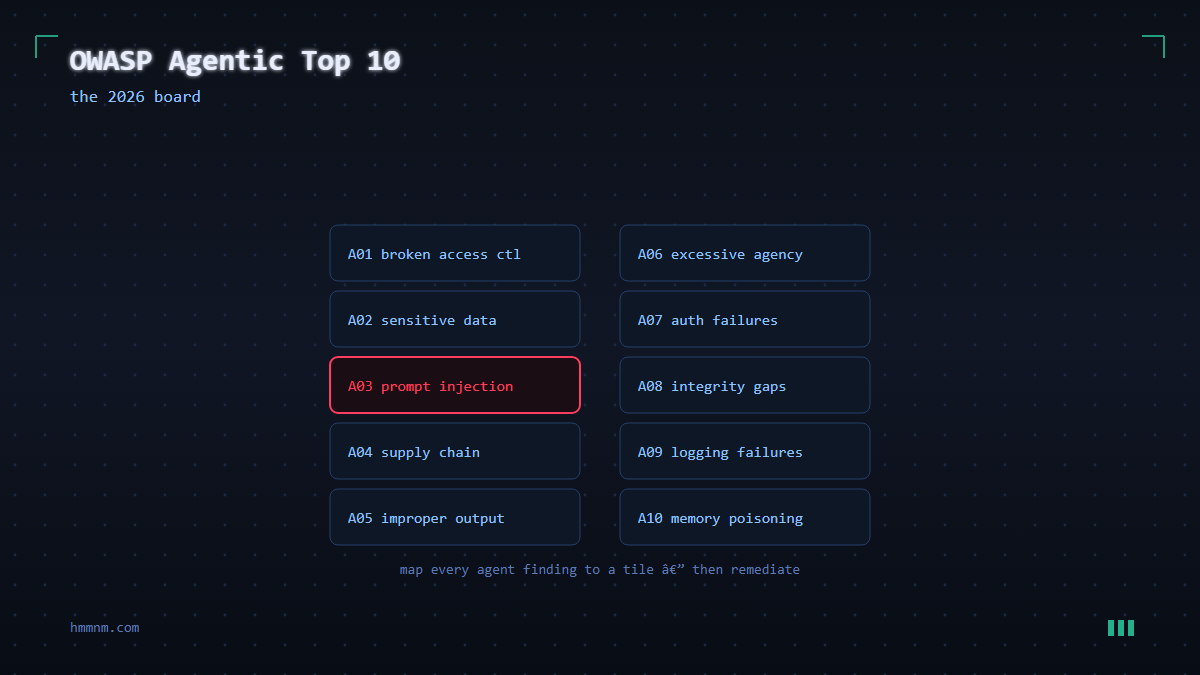
Read more about the article OWASP Top 10 for Agentic Applications 2026: Complete Security Guide
2723-hero

OWASP Top 10 for Agentic Applications 2026: Complete Security Guide

The OWASP Top 10 for Agentic Applications defines the most critical security risks for autonomous AI agents in 2026. From prompt injection and tool hijacking to supply chain poisoning and multi-agent attacks, this comprehensive guide covers every vulnerability with real attack scenarios and proven defense strategies.

Continue ReadingOWASP Top 10 for Agentic Applications 2026: Complete Security Guide
Read more about the article MCP Security and Pentesting: Threats, Test Cases, and Hardening
MCP Security and Pentesting: Threats & Hardening

MCP Security and Pentesting: Threats, Test Cases, and Hardening

A comprehensive security assessment of the Model Context Protocol covering threat modeling, attack surface analysis, pentest methodologies, prompt injection test cases, and hardening strategies for MCP servers and clients.

Continue ReadingMCP Security and Pentesting: Threats, Test Cases, and Hardening
Read more about the article MCP Security: Threat Model and Hardening Guide for Model Context Protocol
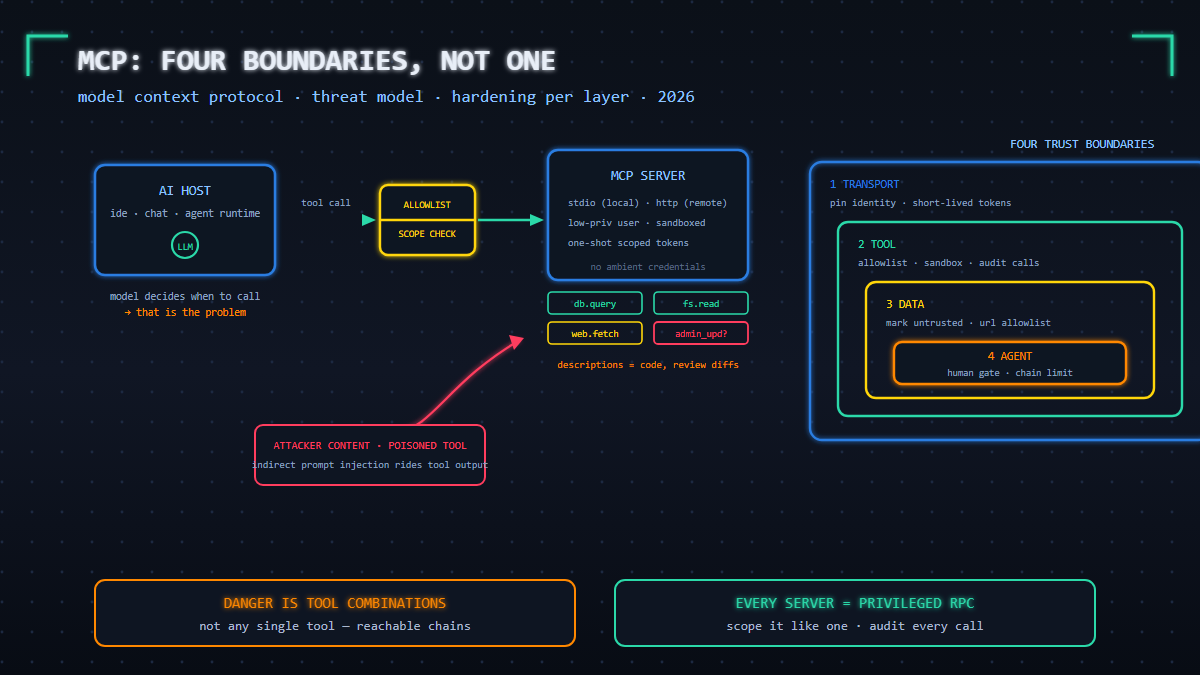
MCP security four trust boundaries hardening 2026

MCP Security: Threat Model and Hardening Guide for Model Context Protocol

MCP is not one trust boundary - it is four: transport, tool, data and agent. This guide maps the Model Context Protocol attack surface and gives a hardening checklist for every layer, from stdio server credentials to tool-description review.

Continue ReadingMCP Security: Threat Model and Hardening Guide for Model Context Protocol
Read more about the article Zero Trust Architecture for AI Systems: Implementation Guide
zero-trust-featured

Zero Trust Architecture for AI Systems: Implementation Guide

Zero Trust for AI systems requires rethinking identity, data flows, and access control. Learn the five pillars of AI Zero Trust — identity verification, input validation, least privilege, monitoring, and encryption — with practical architecture patterns and implementation roadmap.

Continue ReadingZero Trust Architecture for AI Systems: Implementation Guide