LastPass 2022: The Dev-Environment Breach That Came Back
August’s ‘contained’ developer-account compromise returned in December as stolen vault backups. Inside the two-act breach.

August’s ‘contained’ developer-account compromise returned in December as stolen vault backups. Inside the two-act breach.
GitHub’s OAuth tokens lived in Heroku’s infrastructure. One compromised CI cache later, an ecosystem learned where vendor tokens really live.
The finale of our OWASP Agentic Skills Top 10 series. AST09: one-line skill installs that no inventory, IAM system, or SOC ever sees — 800+ malicious skills circulating, 83% of organizations deploying agentic AI, 29% ready. AST10: porting skills across platforms silently drops manifests, permissions, and risk tiers. With the Bilateral Receipt Pattern, EU AI Act Article 12, and the Universal Skill Format proposal.
The two post-deployment risks in the OWASP Agentic Skills Top 10: AST07 malicious updates riding channels with no signatures, pinning or freeze mode (40,000 exposed instances in 24 hours), and AST08 scanners that structurally lag base64, zero-width, pure-natural-language and .pyc evasion. Digest pinning, PASS/FAIL/INCOMPLETE pipelines, and Unicode strip ranges — dissected.
AST02 of the OWASP Agentic Skills Top 10 maps attacks on the skill distribution layer: registry flooding, dependency confusion, config files that execute on clone (CVE-2025-59536, CVE-2026-21852), and maintainer takeover. With Trail of Bits' evidence that every marketplace scanner can be bypassed.
AST01 of the OWASP Agentic Skills Top 10 dissected: how ClawHavoc shipped 1,184 malicious skills from 12 accounts, why five of ClawHub's top seven downloads were malware, and how three lines of markdown exfiltrated SSH keys - with the full attack playbook and controls.
The OWASP Agentic Skills Top 10 maps the 10 risks of the AI-agent skill ecosystem - malicious skills, supply chain compromise, over-privileged manifests, metadata attacks, weak isolation, update drift, scanning gaps, governance failures and cross-platform reuse - with real 2026 evidence.
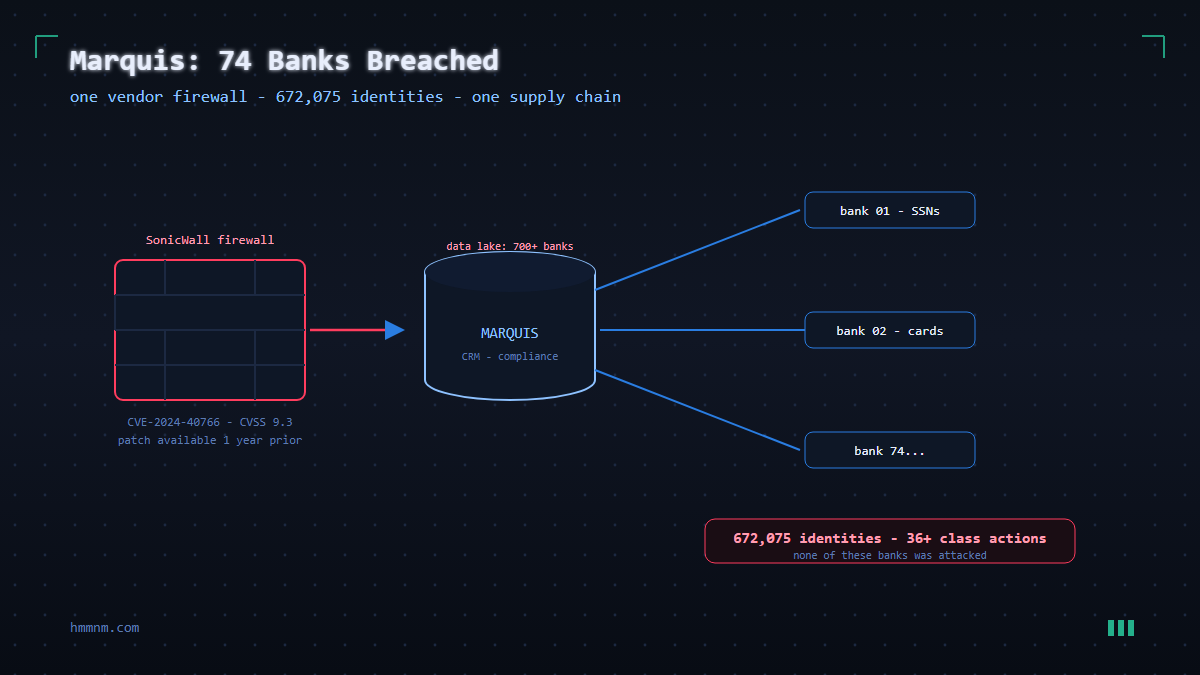
Attackers entered Texas fintech Marquis through a SonicWall firewall and reached data for 700+ client banks - 672,075 identities, 74 institutions disrupted. The supply-chain anatomy and five break-points.
Three versions of node-ipc (10.1.1-10.1.3) shipped a stealer backdoor - CVE-2026-44338 - harvesting SSH keys, AWS credentials and .npmrc from 1.2M-weekly-download installs via DNS tunneling and HTTPS C2. Technical breakdown and hardening guide.
Two AI security incidents in 48 hours: Bleeding Llama (CVE-2026-7482, CVSS 9.1) leaks full process memory from 300K+ exposed Ollama servers via malicious GGUF files, while a fake OpenAI Privacy Filter on Hugging Face hit #1 trending and delivered a Rust infostealer to 244K+ victims. Verification and patching playbook inside.
Three AI-adjacent CVEs hit CISA’s KEV catalog in one month: the LiteLLM proxy auth bypass exposing every prompt your org ever sent, a Linux kernel privesc reaching GPU training clusters, and PAN-OS as the beachhead. Living off the LLM, explained.
Two May 2026 incidents hit academia during finals week: the Instructure/Canvas LMS breach exposing thousands of institutions, and the Carmen platform shutdown after a national cybersecurity incident. The education sector's vendor graph is the new attack surface.