
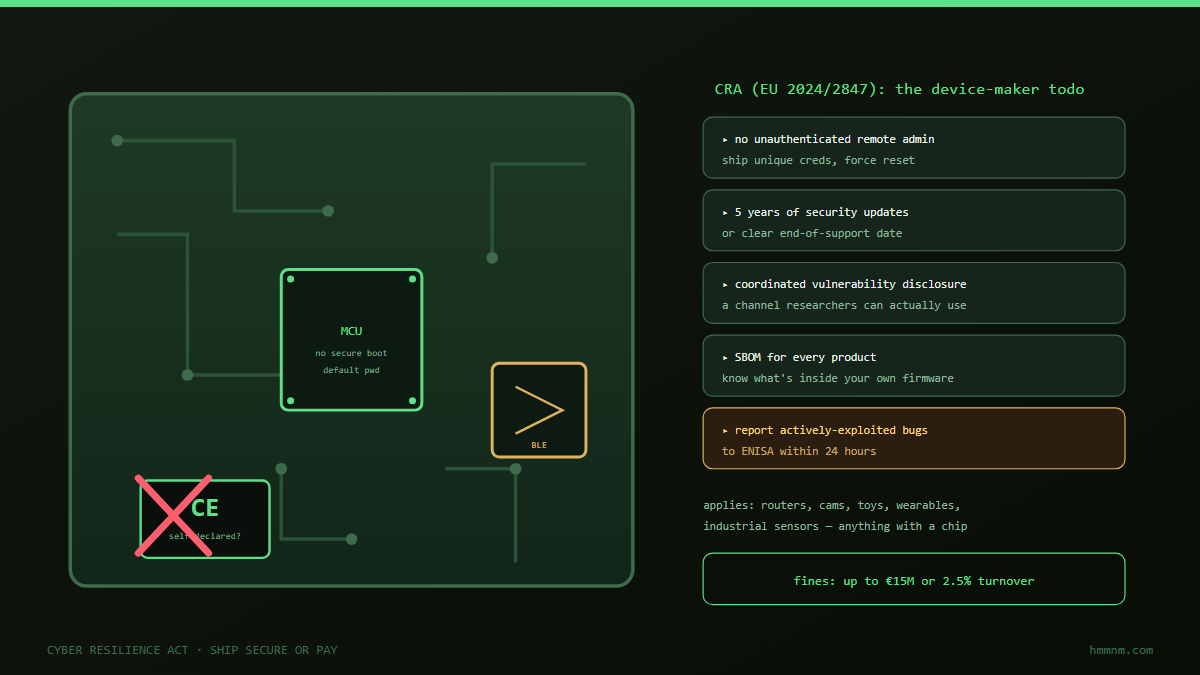
Read more about the article The Cyber Resilience Act: Security Is the Product Now
Cyber Resilience Act CE mark circuit board obligations

The Cyber Resilience Act: Security Is the Product Now

From 2027 connected products without CRA-backed security lose the CE mark and the EU market. EN 303 645 already draws the floor: no default passwords, disclosure policy, update transparency. The real work is turning security into a documented lifecycle — threat models, SBOMs, tested updates — instead of a checkbox before the ceremony.
Continue ReadingThe Cyber Resilience Act: Security Is the Product Now
Read more about the article Software Supply Chain Security: Risks in Dependencies, Builds, and Secrets
Supply Chain Security: Risks in Dependencies, Builds & Secrets

Software Supply Chain Security: Risks in Dependencies, Builds, and Secrets

A practical guide to software supply chain security covering dependency risks, secrets exposure, CI/CD trust failures, artifact integrity verification, SBOM management, and real-world attack case studies.

Continue ReadingSoftware Supply Chain Security: Risks in Dependencies, Builds, and Secrets