
Skip to content
Hmmnm brand header logo displayed prominently across the top of the webpage
  • Home
  • Blog
  • About Us
  • Contact
  • Services
  • Products
  • Cybersecurity Learning Paths
  • Toggle website search
Press Escape to close the search panel.
Menu Close
  • Home
  • Blog
  • About Us
  • Contact
  • Services
  • Products
  • Cybersecurity Learning Paths
  • Toggle website search
Search this website

Lateral Movement

  1. Home>
  2. Blog>
  3. Lateral Movement
Read more about the article Ransomware Evolution 2016-2026: What Defenders Keep Missing
Ransomware Evolution 2016-2026: What Defenders Keep Missing

Ransomware Evolution 2016-2026: What Defenders Keep Missing

  • Post author:Prabhu Kalyan Samal
  • Post published:August 22, 2026
  • Post category:Ransomware & Malware/Security

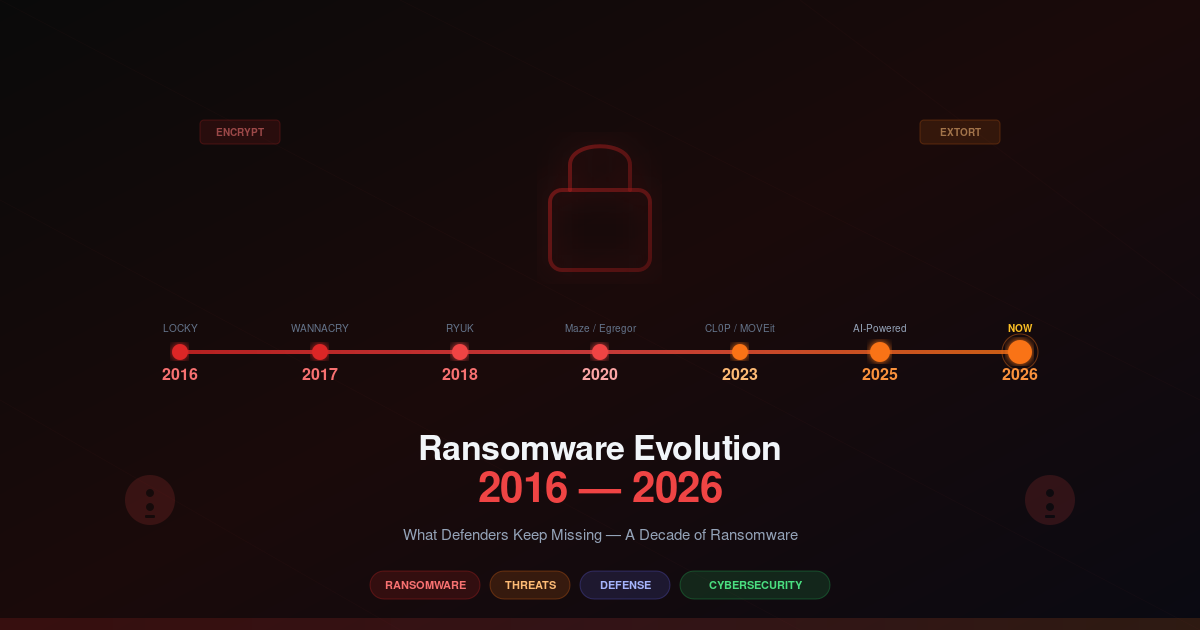
A decade analysis of ransomware evolution from 2016 to 2026, covering RaaS operations, double extortion, initial access brokers, living off the land techniques, and what defenders keep missing.

Continue ReadingRansomware Evolution 2016-2026: What Defenders Keep Missing
Press Escape to close the search panel.

Categories

  • AI Security (1)
  • Aviation and Aerospace Security (9)
  • Beyond Security (1)
  • Security (337)
  • Technology (62)

Recent Posts

  • Terraform State: The Most Sensitive File in Your Infrastructure
  • Hands-On Container Escape Lab: Privilege Escalation from Pod to Node with Real Commands
  • JWT Security: alg=none, Key Confusion and Why the Header Lies
  • Weekly Threat Intel: Supply Chain Compromises, Autumn CVE Exploitation and Infostealer Trends
  • UEFI Secure Boot and BlackLotus: The Boot Chain of Trust Under Attack
  • Weekly Threat Intel: Edge CVEs, MCP Agent Abuse, Stealer Cashouts
  • HTTP/3 and QUIC: How the Web Moved to a New Transport
  • Dependency Confusion Lab: Reproduce and Defend Your Pipeline
  • Cosign Signing and Verification Lab: Sign, Verify, Enforce
  • Kerberos Attack Paths: Golden Tickets, Silver Tickets and Kerberoasting
  • DNSSEC Explained: Chain of Trust, NSEC3 and the October 2026 Root Rollover
  • BOLA and Broken Auth API Attacks with Burp Suite: Lab Guide
  • OWASP ZAP DAST Lab: Authenticated API Scanning Explained
  • eBPF Explained: Verified Programs Inside the Kernel
  • SSRF to Cloud Metadata: The Attack Behind Capital One and How to Stop It

Archives

  • September 2026 (258)
  • August 2026 (98)

Newsletter

Get all latest content delivered to your email a few times a month. Updates and news about all categories will send to you.
Email is required Email is not valid
This field is required
Thanks for your subscription.
Failed to subscribe, please contact admin.
Hmmnm

Our Other Sites

  • Hmmnm.in
  • Odia.hmmnm.in

Quick Links

  • Security Services
  • Learning Paths
  • About Us
  • Contact
  • Blog
  • Privacy Policy
  • Disclaimer
  • Security Products
  • Terms of Service

Contact Info

  • 📧 contact@hmmnm.com
  • 🌐 hmmnm.com
in
© 2026 @Hmmnm

We use cookies to understand how the site is used and to improve your experience. You can accept analytics cookies or continue with essential cookies only. Privacy Policy

  • Home
  • Blog
  • Security
  • Experience
  • About Us
  • Services
  • Contact