Software Supply Chain Security for AI Agents and MCP Servers
A deep dive into securing AI agent supply chains — MCP server vetting, dependency integrity, sandboxing, and trust anchors for AI infrastructure.

A deep dive into securing AI agent supply chains — MCP server vetting, dependency integrity, sandboxing, and trust anchors for AI infrastructure.
Zero Trust for AI systems requires rethinking identity, data flows, and access control. Learn the five pillars of AI Zero Trust — identity verification, input validation, least privilege, monitoring, and encryption — with practical architecture patterns and implementation roadmap.
Post-quantum cryptography is no longer a research-only topic. With NIST's first PQC standards finalized and organizations facing long-term risks such as harvest-now, decrypt-later, cyber teams need to understand how PQC affects PKI, TLS, code signing, firmware trust, crypto agility, and migration planning. This guide explains what PQC is, where QKD fits, how hybrid deployments work, and what defenders should prioritize first.
CORS misconfigurations rank among the most critical web security vulnerabilities in modern applications. Learn how to identify, exploit, and remediate cross-origin resource sharing flaws including origin reflection, null origin trust, and subdomain bypass techniques.
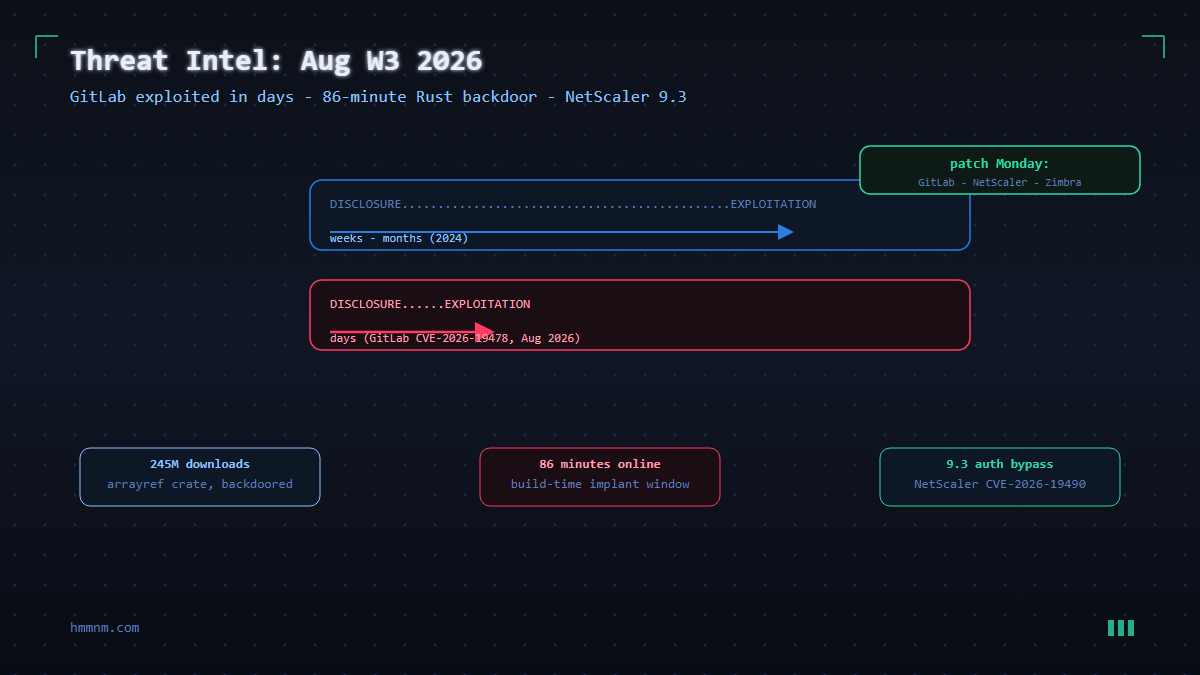
GitLab CVE-2026-19478 went from disclosure to in-the-wild exploitation in days; a compromised maintainer account backdoored three Rust crates with 245M downloads for 86 minutes; Citrix shipped a CVSS 9.3 NetScaler auth bypass. The week's threats, IoCs, and your Monday patch list.
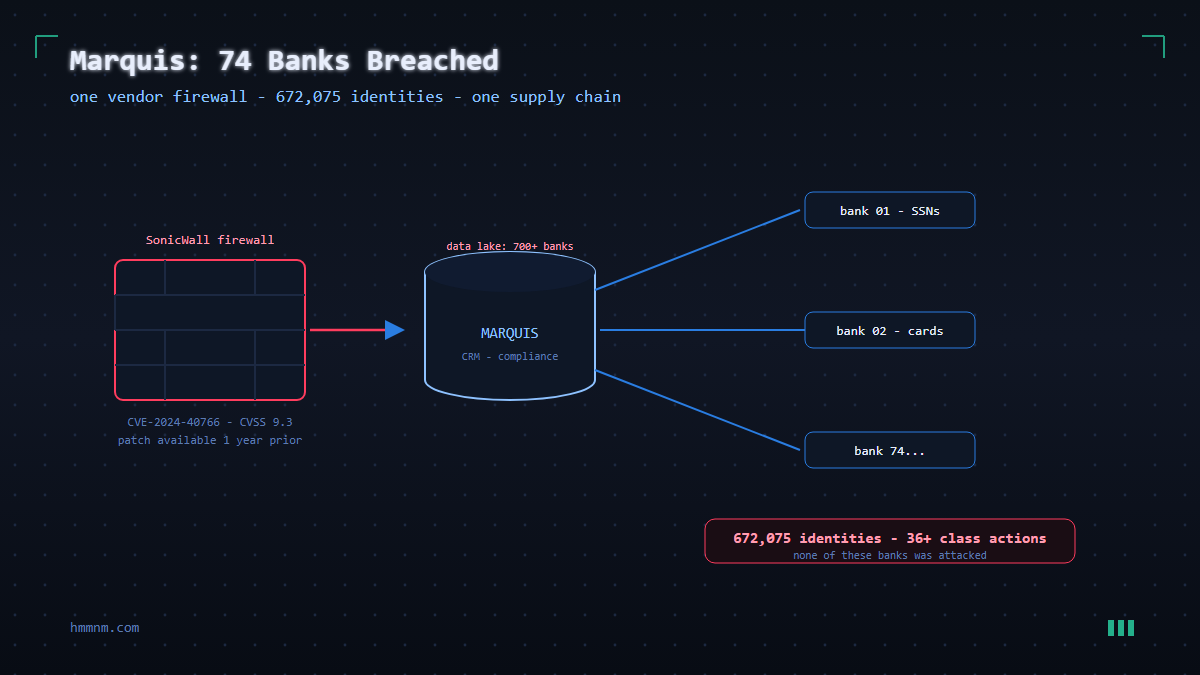
Attackers entered Texas fintech Marquis through a SonicWall firewall and reached data for 700+ client banks - 672,075 identities, 74 institutions disrupted. The supply-chain anatomy and five break-points.
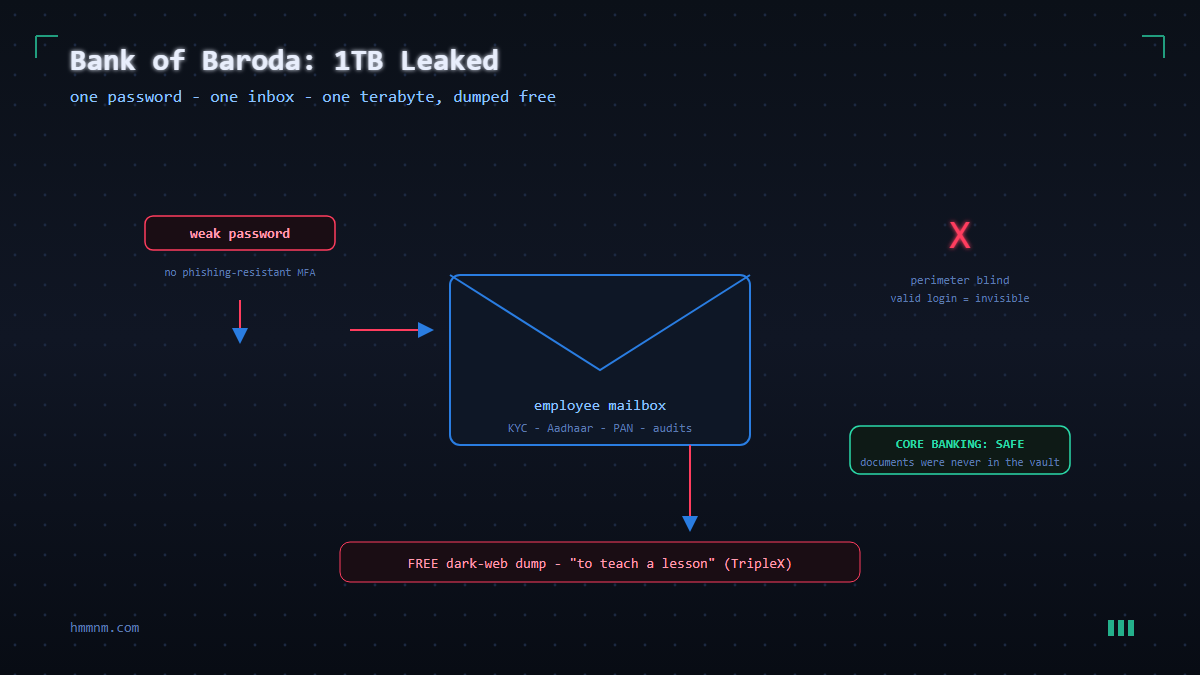
TripleX published 1TB of Bank of Baroda customer data for free after a credential-only intrusion - no malware, no core banking access. Full attack anatomy and the five break-points that would have stopped it.
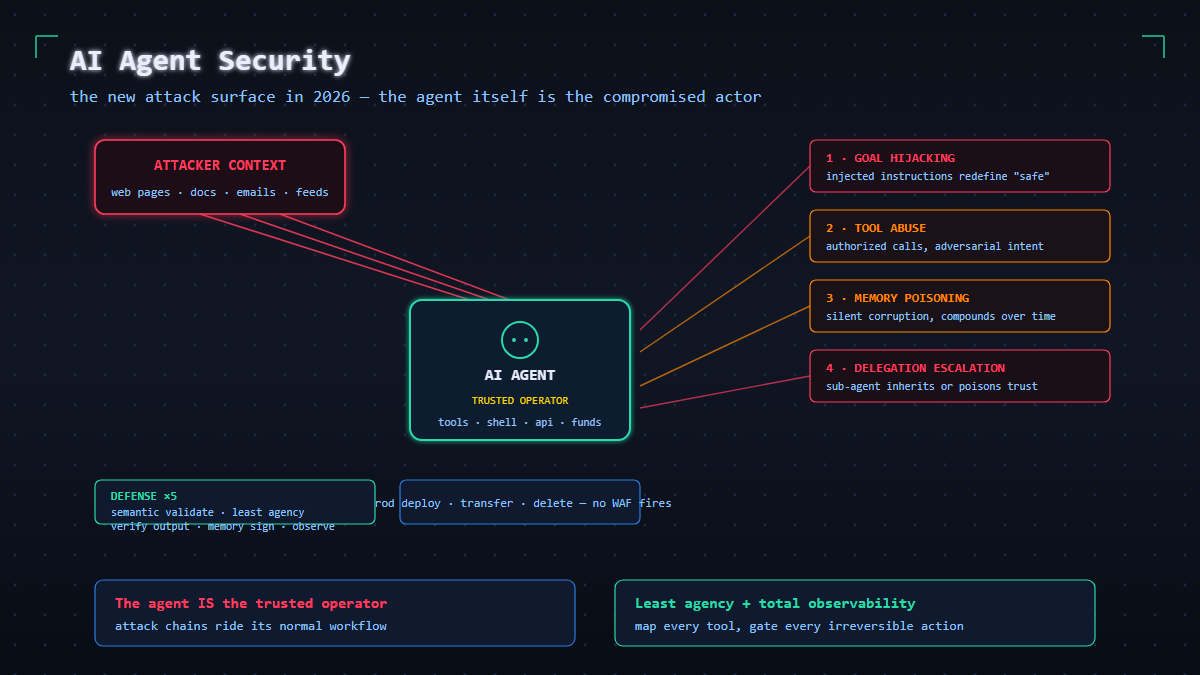
AI agents are the new attack surface: goal hijacking, tool abuse, memory poisoning, and delegation escalation — plus the five-layer defense framework that catches what WAFs and code review can’t.
What should a penetration test cost in 2026? Real price ranges by test type, the five factors that move quotes, a build-your-own estimate formula, and the red flags of scanner resale dressed up as pentesting.
Security Operations Centers are drowning in alerts. This guide covers how SOAR platforms, AI-driven playbook automation, and autonomous triage are transforming SOC efficiency in 2026.
Discover how AI is revolutionizing ransomware attacks in 2026 — from automated RaaS platforms to deepfake-powered extortion and actionable defense strategies.
June 2026 threat briefing: Cordyceps CI/CD flaws exposed 300+ GitHub repos, Cisco SD-WAN zero-days exploited in the wild, and AI-powered agentic adversaries are compressing the attack lifecycle from weeks to hours.