SSRF to Cloud Metadata: The Attack Behind Capital One and How to Stop It
How SSRF turns one forged request into cloud-wide credential theft — the Capital One chain, IMDSv2, and the controls that actually block it.

How SSRF turns one forged request into cloud-wide credential theft — the Capital One chain, IMDSv2, and the controls that actually block it.
The Kubernetes security layers that stop real cluster compromises: control plane, RBAC, Pod Security Admission, network policy and image supply chain — with a ten-point audit checklist.
On 28 February 2020, Virgin Media confirmed that a marketing database containing the personal details of around 900,000 people had been left insecure and accessible online, discovered not by criminals but by a researcher during unrelated work. The dataset, stored on an unsecured cloud instance, included names, home and email addresses, and phone numbers, and had been reachable for at least ten months. This post explains exactly what was exposed, how the misconfiguration happened, how Virgin Media responded, and what happened next: a textbook non-hack data breach that still required full disclosure, notification, and regulatory scrutiny.
A notebook container bug, an embedded certificate, and a confused gateway let any Cosmos DB customer read every other tenant’s data. Fixed in 48 hours, taught forever.
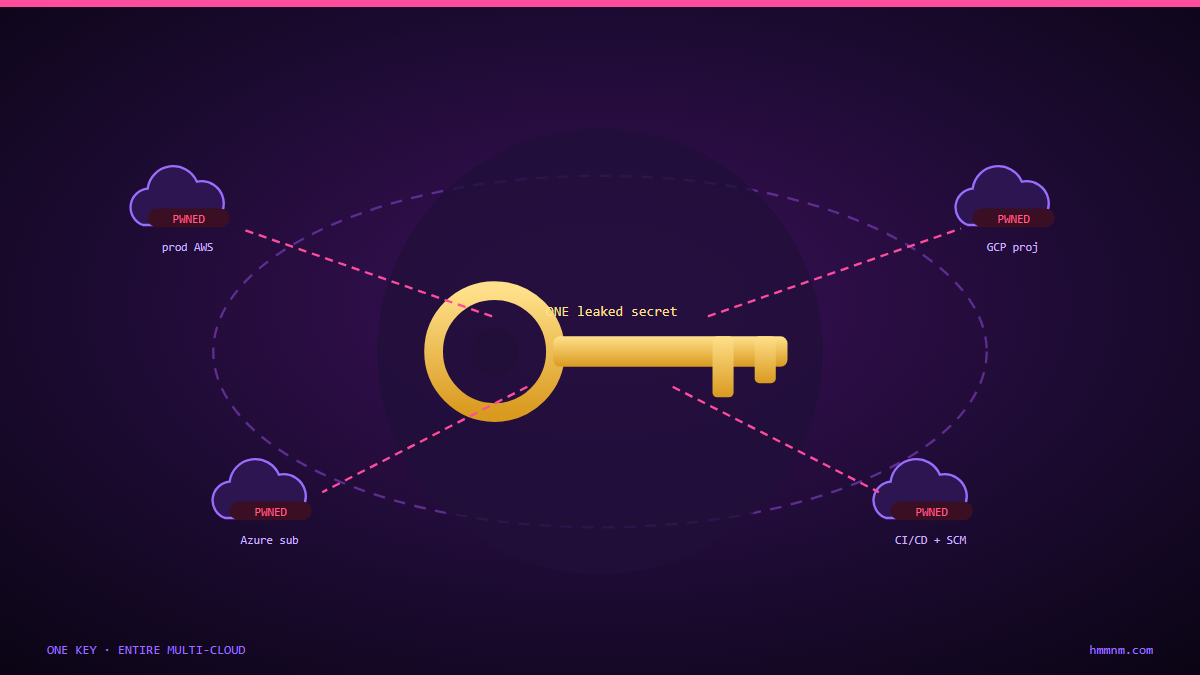
Toyota left one access key on GitHub for five years. This is the full chain: where cloud secrets leak, how attackers turn a found key into root, and the architecture that survives a leak they cannot prevent.
Zero Trust for AI systems requires rethinking identity, data flows, and access control. Learn the five pillars of AI Zero Trust — identity verification, input validation, least privilege, monitoring, and encryption — with practical architecture patterns and implementation roadmap.
A comprehensive guide to the top 10 emerging cybersecurity threats in 2026, including AI-powered attacks, post-quantum risks, cloud-native exploits, and deepfake fraud.
This week: FIFA World Cup 2026 phishing campaigns, PCPJack cloud server hijacking, Claude Code GitHub Action repo takeover, Cisco SD-WAN zero-day CVE-2026-20245, and the rise of agentic AI in cybersecurity defense.