Deep Dive into Server-Side Template Injection (SSTI)
A deep dive into Server-Side Template Injection (SSTI) — how template engines turn attacker input into RCE, with discovery, exploitation and defense patterns.
CVE-2026-41940 let unauthenticated attackers bypass cPanel/WHM/Webmail logins entirely — exploits hit before the patch existed. Ports 2082-2096 went dark industry-wide within the hour. Patched versions, response timeline, and audit steps inside.
XXE Injection remains one of the most dangerous web vulnerabilities, allowing attackers to read server files, execute SSRF, and even achieve remote code execution. Master in-band, out-of-band, and blind XXE techniques with practical payload examples.
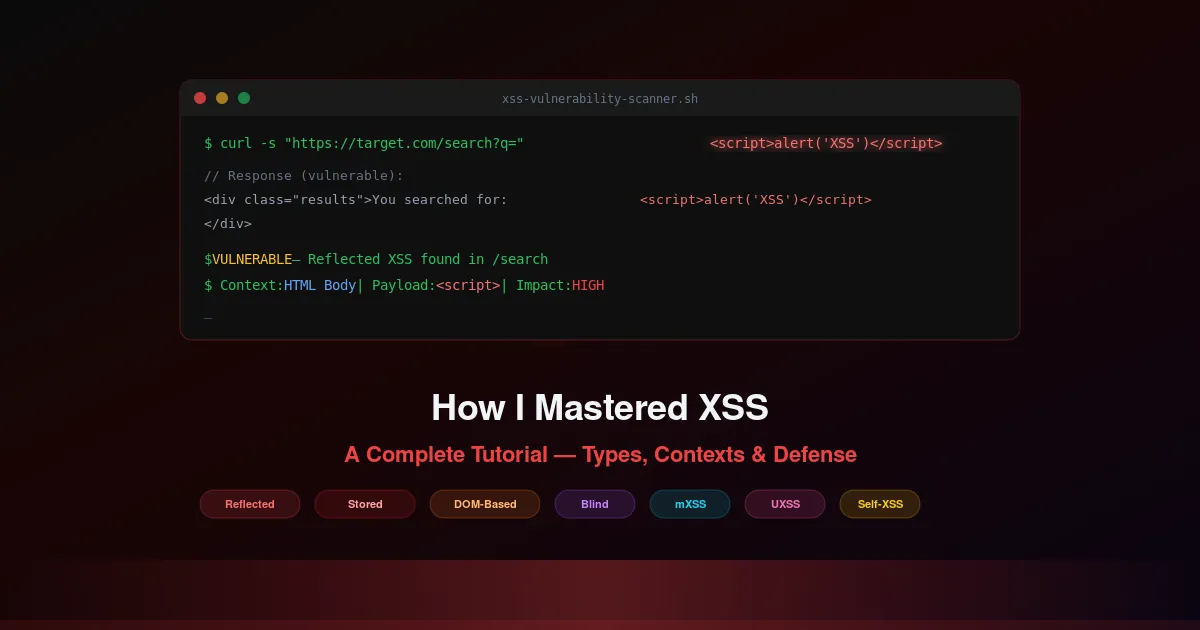
Complete cross-site scripting (XSS) tutorial covering stored, reflected, and DOM-based XSS with practical exploitation examples and prevention strategies including CSP.