
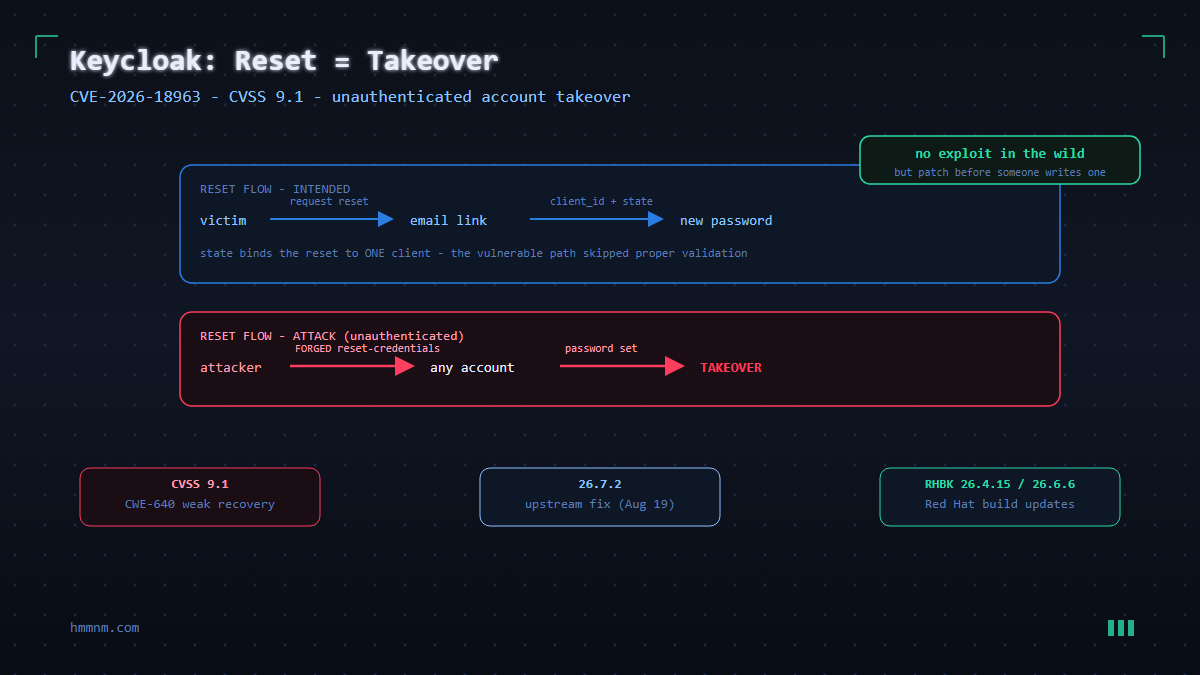
Keycloak CVE-2026-18963 reset-credentials takeover – broken handshake diagram
Keycloak CVE-2026-18963: Account Takeover via Password Reset
Keycloak’s reset-credentials flow skips its own email action token: an unauthenticated attacker can set a new password on any account, including admins. CVSS 9.1, fixed in 26.7.2 – patch guide, detection hunting, and the temporary mitigation inside.